API Rate Limiting Defensibility — The Throttle Stack
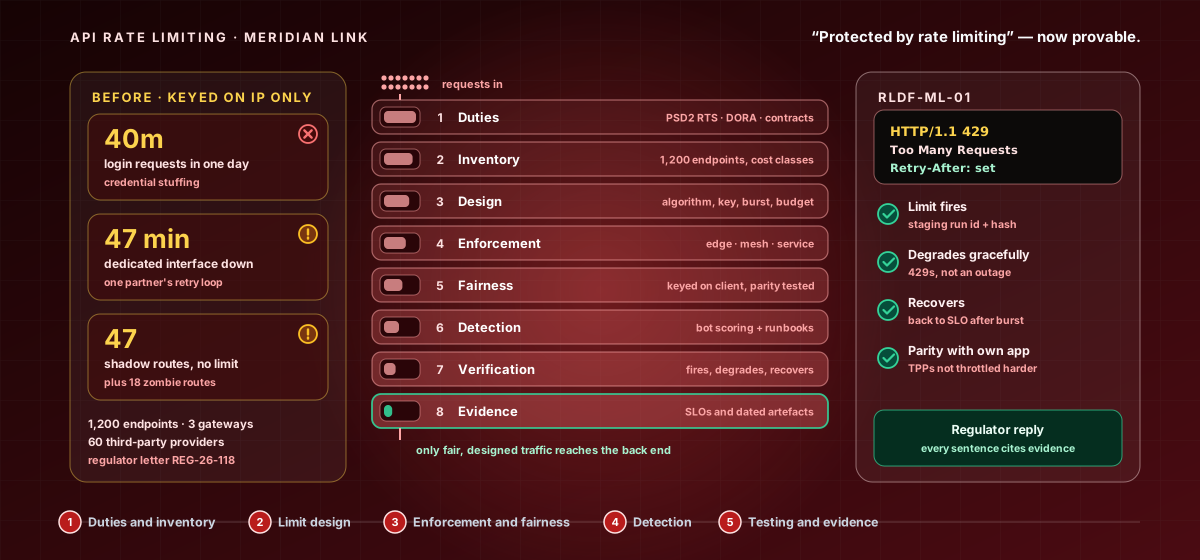
An expert-level course that turns 'our APIs are protected by rate limiting' into something a regulator, a customer or a third-party provider can check. Work the throttle stack - eight layers a rate limit passes from a default setting to evidence: Duties, Abuse Cases & Risk Mapping; Endpoint Inventory & Cost Classes; Limit Design: Algorithms, Keys & Budgets; Gateway, Service & Data-Layer Enforcement; Client Identity, Quotas & Fairness; Abuse Detection, Bot Management & Response; Verification Testing & Evidence; and Metrics, Customer Commitments & Regulator Dialogue - across one continuous open-banking case, building a single capstone rate limiting defensibility file one component per chapter.
What you'll learn
- Map every rate limit to the regulatory, security and contractual duties and the OWASP abuse cases it controls, and inventory every routed endpoint with an owner, a sensitivity and a measured cost class.
- Design limits with the right algorithm and key, derive budgets from measured backend capacity and cost per request with the arithmetic shown, and enforce them at gateway, mesh, service and data layers with shared counters, correct 429 semantics and signed fail modes.
- Register client identities that cannot be cheaply multiplied, publish fair quota tiers with measurable criteria, prove parity with the own channel pair by pair, and detect the automated abuse that stays below every configured limit.
- Verify on authorised own staging that each limit fires, degrades and recovers, file every run as reconstructable evidence behind a regression gate, and answer regulators and customers with measured figures, dated citations and a disclosed roadmap.
Sign in to enrol — you can pay by bKash or Nagad, or apply a promo code.