Course catalogue
545 courses across five levels. Explore any course to see what it covers — sign in to enrol.
Beginner · 112 courses
Cybersecurity Foundations (English + বাংলা)
A ten-hour guided course that teaches how security actually works — from the CIA triad to running a security programme — using one clinic as a continuous case study. Switch between English and বাংলা…
Emergency Change Control — The Midnight Release
A nine-hour change-war-room simulation where you classify risk, challenge approvals, rehearse rollback, command a midnight emergency, reconstruct evidence, and design a complete operating model.
Vulnerability Validation Range — From Scanner Finding to Exploitability Decision
A nine-hour authorized technical range where you scope safely, interrogate scanner output, validate with minimum proof, rate exploitability, model attack paths, write findings, and defend retest…
Crypto Agility Drill — Surviving Algorithm and Certificate Change
A nine-hour engineering workbench where you inventory cryptography, control certificates and keys, migrate TLS, prepare post-quantum transition, command a CA compromise, and defend a measurable…
Vulnerability Remediation Control Tower — From Finding Noise to Exposure Reduction
A nine-hour live operations queue where you recover asset coverage, validate findings, rank attacker opportunity, govern remediation and exceptions, verify closure, and defend a 90-day…
Asset Truth Expedition — Find, Name, Own, and Retire What the Bank Depends On
A nine-hour guided missing-asset investigation where one unknown branch device opens a map of hardware, software, information, identities, cloud resources, suppliers, lifecycles, and accountable…
Wireless Airspace Lab — From Radio Evidence to Trusted Access
A nine-hour RF field survey and engineering lab where you map propagation, trace 802.11 sessions, build WPA identity, isolate guests and devices, command a rogue-AP incident, and defend a measurable…
Human Signal Studio — Design Safer Decisions, Not Blame
A nine-hour behavioral-design studio where you diagnose real work, prototype moment-of-action controls, run ethical simulations, build role missions, strengthen reporting, and defend an evidence-led…
Detection Foundry — From Threat Hypothesis to Trusted Alert
A nine-hour detection-content foundry where you qualify telemetry, model behavior, build and test analytics, design usable alerts, tune from evidence, validate end to end, and defend transparent…
Network Access Control — From Unknown Device to Trusted Access
A nine-hour analyst simulation where you discover a real network, contain rogue access, build identity-aware policy, troubleshoot 802.1X and RADIUS, and defend a safe rollout.
Application Security Field Lab — From Attack Surface to Secure Program
A nine-hour engineering workbench where you map an application's attack surface, neutralize injection, harden authentication and access control, protect data and secrets, control dependencies, build…
Secure SDLC Phase-Gate — Building Security In, Not Bolting It On
A nine-hour lifecycle simulation where you follow one payments feature through requirements, design, build, review, verification, supply chain, deployment, and response — passing a security gate at…
DevSecOps Pipeline Command — Guardrails at the Speed of Delivery
A nine-hour pipeline-and-on-call simulation where you turn security into automated guardrails across CI/CD, containers, infrastructure as code, secrets, runtime, and incident response — without…
Own Your Cloud — Cloud Security Essentials
A nine-hour posture studio where you map shared responsibility on a live architecture diagram, then harden identity, network, data, posture, logging, workloads, and governance for a company…
Zero Trust Architecture Studio — Never Trust, Always Verify
A nine-hour architecture studio where you redesign a bank away from castle-and-moat, deciding identity, device, segmentation, least-privilege, continuous verification, and data-centric controls…
IAM Access Desk — Who Gets Into What, and Why
A ten-hour beginner course where you work the access desk of a company, learning identity and access management by deciding who gets into which systems — reading an access matrix, applying least…
Email Security Desk — Spot the Phish, Handle It Safely
A ten-hour beginner course where you work a company's reported-messages desk, learning to read emails the way an attacker hopes you won't — spotting red flags, understanding email authentication and…
Physical Security — The Security Zones
A thorough, highly interactive beginner course where you assess a facility's physical security as layered zones — perimeter, grounds, building, interior, secure area, and asset. Deter, detect, delay…
Cryptography Foundations — How Encryption Works
A gentle, jargon-free beginner's course on how cryptography actually works. Follow a secret message from Alice to Bob — past Eve, the eavesdropper — and build up encryption, keys, public keys…
Social Engineering Defense — Spotting the Human Hack
A gentle, jargon-free beginner's course on recognizing and defeating the scams that target people instead of computers — phishing emails, scam texts and calls, impersonation, fake login pages…
Data Protection — Follow the File
A gentle, story-driven beginner course that follows one student's file through every room data lives in — collecting, labeling, storing, sharing, keeping, destroying, and answering for it — teaching…
Cyber Law & Ethics — Doing the Right Thing Online at Work
A gentle, plain-language start to using computers and data the right way at work — built around one simple question, could this hurt someone, and am I allowed? — for anyone in their first job or…
AI Security — Working Safely with AI at Work
A gentle, plain-language guide to using AI tools safely and sensibly at work — built around one simple way of working, treat it as a clever assistant you check, keep private things from, and stay in…
Patch Management — Keeping Your Software Up to Date
A gentle, plain-language guide to keeping your software up to date — why those 'update available' messages matter, and the simple habit that closes the holes attackers rely on: turn on automatic…
Security Operations — Keeping Watch, Together
A gentle, plain-language guide to how a security team keeps watch — and your genuine part in it — built around one simple idea: you're part of the watch, so notice what seems wrong, report it, and…
Privacy Management — Looking After People's Information, Properly
A gentle, plain-language guide to how a workplace looks after people's personal information as an organised system, not by luck — know what you hold and why, name an owner, live the rules, mind the…
Disaster Recovery — When Things Go Wrong, and How to Be Ready
A gentle, plain-language guide to being ready for a workplace's worst day — the backups, the one-page plan, the shared basics, and the hour of practice that turn fire, theft, ransomware, or a dead…
OT & ICS Security — The Computers Inside Things
A gentle, plain-language guide to the hidden computers that run machines, factories, and buildings — why their world plays by different rules (the computers have hands), and the ordinary person's…
Container Security — Apps in Boxes, Shipped Safe
A friendly first course on how modern software ships — apps packed into containers — and the six questions that keep the boxes trustworthy: what's in it, where's it from, how fresh, any secrets, how…
SIEM — The Signal Line: How the Alarm System Hears
A friendly first course on how an organisation hears its own systems — every action leaves a trace, traces travel to one listening post, rules turn them into questions, and people give the questions…
Understanding Software Flaws — How Cracks Are Found and Mended
A defensive, plain-language guide to the life story of a software flaw: why all software has them, what makes one serious, who finds them, how finders tell responsibly, how fixes are raced out — and…
Patient Privacy — Holding a Record Well
A gentle, practical guide to health-information privacy for people who work around patients: why records carry extra weight, who may see them and why, the curiosity problem, careful talk, proper…
What Could Go Wrong? — Thinking a Change Through
Threat modelling as an everyday thinking habit rather than a formal method: four plain questions, asked early, of the people who do the work — and they fit a key cupboard as well as a database.
Who Decides? — Governance in Plain Words
A forbidding word for a simple thing: who is allowed to decide what, and how decisions stick. Authority, records, policies, exceptions, accountability, and checking — for the people who meet all of…
Being Audited Well — When Someone Comes to Look
The auditee's side of an audit: what auditors actually want, why evidence beats assurances, how to prepare honestly, how to answer on the day, and what to do with the findings afterwards.
Looking From Outside — Attacker Thinking for People Who Defend
The perspective shift that lets anyone look at their own workplace the way somebody outside would — where the easy way in usually is, what is actually worth wanting, where the permission line sits…
The Unwelcome Program — Malicious Software and What to Do About It
Malicious software for people who aren't analysts: what it actually is, how it ordinarily arrives, what it does to an organisation, the four habits that keep most of it out, and exactly what to do in…
How It All Fits Together — The Shape of the Systems You Work With
Architecture without the word: what exists, what's joined to what, and what sits between them — why flat arrangements turn one problem into every problem, and the four questions that make you useful…
What the Rules Say — Policies, Standards, and the Documents Nobody Reads
What a policy is actually for, how policies, standards, procedures, and guidelines differ, how to read one without reading all of it, why some are never followed, how to ask properly to differ, and…
Holding the Ground — What Defending Actually Looks Like
The defender's craft as a set of habits: learning what normal looks like, doing the boring work consistently, making the safe way the easy way, slowing down when something's off, learning without…
Whose Number Is Right? — Looking After the Information You Work With
Two departments, two figures, and nobody wrong — what a word actually means, where a number came from, whether it's good enough for what you're doing with it, who owns it, what it was collected for…
Talking to the Machine — Using Language Models at Work
What a language model actually is, what it doesn't know and can't tell you it doesn't know, why it sounds equally sure when it's wrong, what happens to what you type — and how to use one at work…
What the Record Says — Logs, Gaps, and Being Able to Find Anything
What a record is for, what's actually in one, why 'we'll check the logs' so often fails, why time is harder than it looks, how long things are kept and by whose decision, and whether anybody can find…
Who's On At Three In The Morning — Cover, Handover, and the Hours Nobody Watches
Who is genuinely on at any given hour, what they can actually do, what the night does to a decision, how a handover loses things, who may wake whom, and which hours you have honestly chosen not to…
The Person Who Checks — Looking At Your Own Organisation and Still Working There On Monday
What checking is actually for, why the insider is both the best-placed and the least objective person available, how to ask so people tell you the truth, and how to say what you found without losing…
The Laptop In Your Bag — What You're Actually Carrying Around
What has quietly accumulated on the machine you carry, the fact that it takes your employer's things outside your employer's walls every evening, why losing the account matters more than losing the…
Somebody Else's Hands — Depending On People You Don't Control
What you actually bought as against what you actually depend on, what each supplier can reach, the suppliers behind your suppliers, what happens on their bad week, and how you would ever get your…
The Things That Are Always On — Connected Kit In An Ordinary Building
How much of an ordinary building turns out to be a computer, why nobody owns any of it, the password it arrived with, why nothing ever prompts an update, and the fact that it outlives the company…
You Only See The Tap — Where Your Work Actually Lives
Your work is not on your machine and never has been, the sign-in is the whole of the protection, services get turned on in ninety seconds and nobody ever turns one off, and a sharing link outlives…
Somebody Wrote That Rule — What It Means To Hand A Decision To A Machine
What 'automatic' actually is, which decisions are safe to hand over and which are not, why every automatic rule looks more accurate than it is, who is standing at the other end of one, and why 'the…
Authorised, And Wrong — How Money Leaves An Organisation
Every route money can go out by, why a change of bank details is the highest-consequence task in the building, why the second signature takes four seconds, and the uncomfortable fact that almost…
Sign To Confirm — Why Access Reviews Certify Everything
Three thousand lines sent to people with eleven minutes, entitlement names nobody in the building can explain, and the asymmetry that makes certifying everything the rational answer.
It Was On The Register — Living With Risk You Have Accepted
What a risk register actually is, what the word 'accepted' commits anybody to, why an unchanged rating tells you nothing about the risk, and the entry that was correct in every respect on the morning…
It Keeps Happening — What A Management System Actually Is
A forbidding phrase for an ordinary object: the arrangement by which something keeps happening without anybody having to remember — and the several you already run without calling them that.
Out Of Five — How Anybody Actually Assesses A Risk
Nobody found the scale; somebody chose it. What a score is shorthand for, how people compare a broken minibus with a leaked passenger list, and why the finding is almost never in the numbers.
Nineteen Questions — Collecting Less Of Other People's Information
The one protection that is complete, permanent and free: not having it. Why forms only ever grow, what the field nobody can explain is doing there, and the four words that empty most of them.
The First Hour — What To Do When You Find Something
You are not the investigator. Your job is to leave it possible for somebody else to investigate — and most of what makes that impossible is done by helpful people in the first ten minutes, or by a…
Our Website — The One You're Responsible For And Didn't Build
It is not one thing; it is nine, bought from seven suppliers over eleven years, and four of them are in the name of somebody who left in 2021. What to find out, in what order, without any technical…
The Monthly Return — Eight Boxes And What They Are Actually Saying
Twenty-six months of returns, nobody had asked who reads them, and the backups box had been green for fourteen months without anybody ever testing a restore. Reporting a number honestly, from the…
Side By Side — Arranging An Exercise Honestly
Two groups who do not normally talk, at an agreed time, with written permission, finding out what each of them can actually see. The arrangement, the authorisation and the write-up — and no technique…
Somebody Has Asked — The Day You Have To Produce Everything
A letter asking for everything about one matter, a deadline that started before anybody read it, and nine places nobody had ever written down. What to do first, what counts as a record, and why the…
A Number You Did Not Make — Relying On What A Model Tells You
A score a machine produces, a decision about a real person, and a box you cannot see inside. What the number is and is not, when it has quietly stopped being right, and why the human still has to…
The Backup You Never Tested — Keeping A Copy You Can Actually Go Back To
A copy you keep so that losing the live version is an inconvenience, not the end. Where it should live, why a sync is not one, and the question that decides whether it is real: have you ever restored…
Running the Incident — How a Small Team Handles One Without Falling Apart
Once something is confirmed real, a handful of ordinary people have to run it together. Who is in charge, the running log, telling the right people, deciding without all the facts, calling it over…
Reading the Audit — What a Cybersecurity Audit Is, and What Its Findings Actually Mean
You have been told you need a cybersecurity audit, or a report has landed on your desk. What an audit is, why independence and the standard matter, what a finding really means, why it is a sample at…
On the Radar — Using Threat Intelligence in a Small Organisation
You are drowning in threat bulletins and none the wiser. What threat intelligence actually is, how to tell the few threats that are yours from the many that aren't, where a small firm gets it, how to…
The Chain — How a Supply-Chain Compromise Reaches You, and What a Small Firm Can Do
The attack does not come from a stranger. It rides in on a software update, a plugin, a component you installed because you trusted its source. Why your chain is longer than you think, why you…
The Phone — Keeping Safe the Most Exposed Device You Own
Your phone is not a gadget. It is the master key to your accounts and your business, carried everywhere and used among strangers. The lock screen, the apps you let in, the message that is the new…
The Tiles — Securing a Business That Lives in Software It Doesn't Run
Your business now lives inside browser apps you log into — email, docs, accounting, the CRM. The provider secures the software; you secure your use of it. The login is the whole front door, and the…
The Signs — How a Small Business Spots Trouble Without a Security Team
You will never build a detection system or run a SIEM. For a small business, detection means one thing: noticing when something is wrong. Knowing your normal, the free alerts you already have, your…
The Note — Being Ready for Ransomware Without Paying
Ransomware locks everything at once and demands payment. You can't be sure to prevent it — so being ready means being able to recover without paying. What it is, how it gets in, why paying is a trap…
The Framework — Using NIST CSF and CIS Controls Without Drowning
You don't have to invent security — experts wrote down what good looks like. NIST CSF is a map, CIS Controls a prioritised checklist. Above all: you don't do all of it. You choose the essentials…
The Settings — Why Configuration Is the Security You Already Have
The same device is safe or wide open depending on how it's set up — so the settings are the security. Default isn't safe. Set things to a baseline, change the settings that matter, expect drift, and…
The Register — Keeping Up With the Rules That Apply to You
Compliance is keeping up with the rules that apply to you — an ongoing practice, not a certificate. Know which rules apply, keep them in one register, map each to what you do, hold the evidence, keep…
The Oversight — Managing Your Use of AI Responsibly
AI increasingly makes decisions about real people, so its use must be managed. Know what AI you use, have a policy, check its risks and impacts, keep a human in charge, never trust it blindly, and…
The Lifeline — Keeping the Business Running When Something Stops You
Business continuity is keeping the essential things running when something disrupts you — not just recovering the computers. Know your essentials, how long you could survive without each, and have a…
The Connections — Securing the Keys That Link Your Apps
Every time you connect one app to another, you create a door into your data. An API key is a password; each connection can do whatever access it was given. Know your connections, give the least…
The Engine — Letting Tools Do the Repetitive GRC Work
Keeping on top of rules and risks is full of repetitive admin. Automation means letting tools do the repetitive parts — reminders, evidence, issue-tracking — automatically, on a good process…
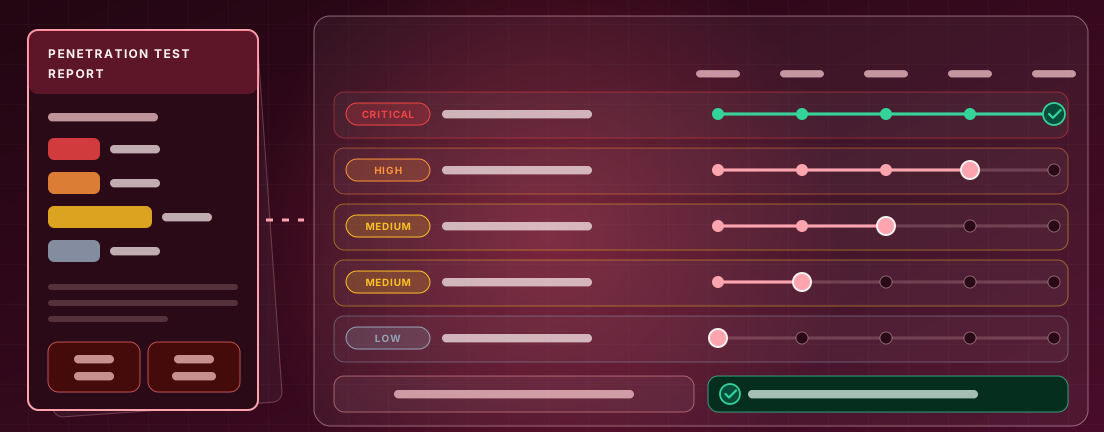
The Findings — Reading and Acting on a Penetration Test Report
A penetration test is a hired, ethical test that finds your weaknesses so you can fix them first. Its report is a to-do list, not a grade. Read it calmly for impact, fix the worst first by severity…
The Scope — PCI DSS for a Small Merchant Taking Card Payments
PCI DSS is the set of rules for taking card payments safely. The key is scope: the less card data you touch, the less applies. Let a compliant provider handle the cards, never store the number, do…
The Shortlist — Buying Suppliers and Software Without Bringing In Risk
When you buy software, a service, or a supplier, you bring their security into your business. So treat a purchase as a security decision: ask before you sign, choose who'll protect your data, put it…
The Layers — Why One Defence Is Never Enough
No single defence is perfect, so you use several — layers — and if one fails, the next holds. Learn to stack different kinds of layer, put the most around what matters most, count your people as a…
The Undo — Making Changes Without Breaking Things
Most things break right after a change — so change carefully and reversibly. Know what a change touches, have a way to put it back, change one thing at a time, check it worked, and tell people. Never…
The Check-Up — Getting Your Systems Tested for Weaknesses
You can't fix what you can't see, so a test finds your weaknesses before an attacker does. A scan is broad and shallow; a test is narrow and deep. Match the check to your need, test what matters…
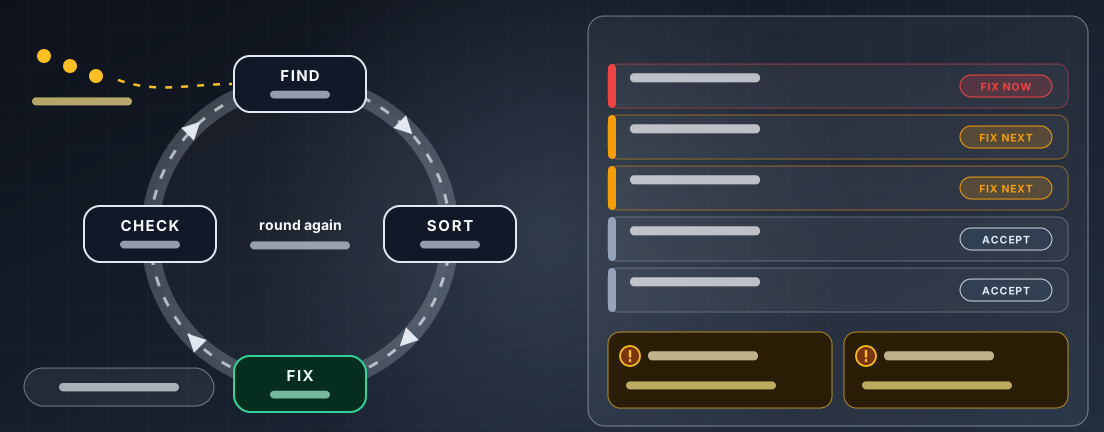
The Cycle — Keeping On Top of Your Weaknesses
New weaknesses keep appearing, so you can never be 'done' — you run a loop. Keep a running list, fix the worst first by risk, decide on each, check fixes hold, and keep the loop turning. Don't chase…
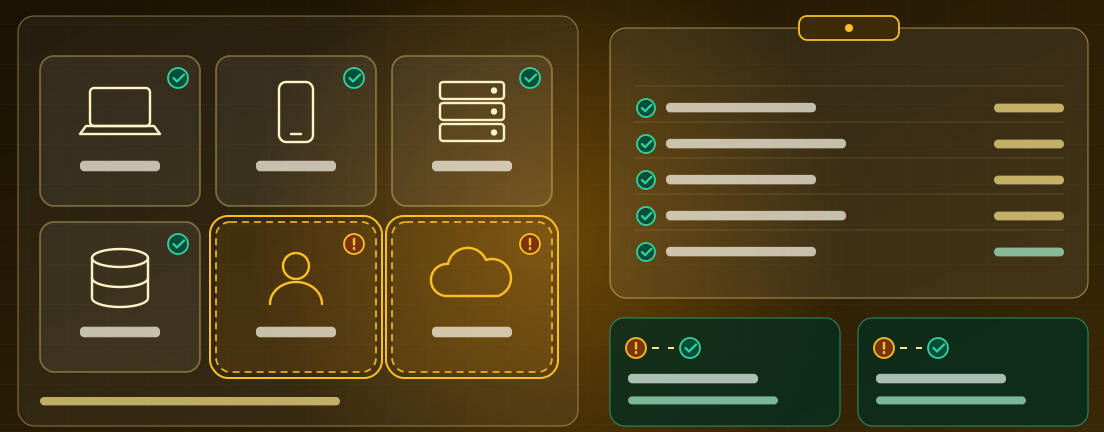
The Inventory — Knowing What You've Got
You can't protect what you don't know you have — and the forgotten things are the dangerous ones. So keep a complete, current list of everything: devices, accounts, services, and data. Hunt the…
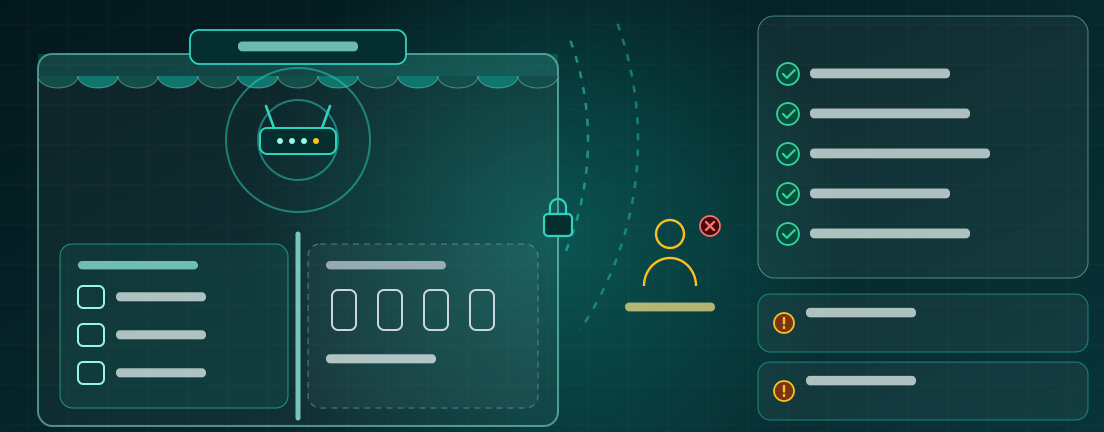
The Airwaves — Securing Your Small Business Wifi
Your wifi is a door into your business, and its signal reaches past your walls — so anyone nearby can try it. Lock it with a strong password and modern encryption, change the router's known defaults…
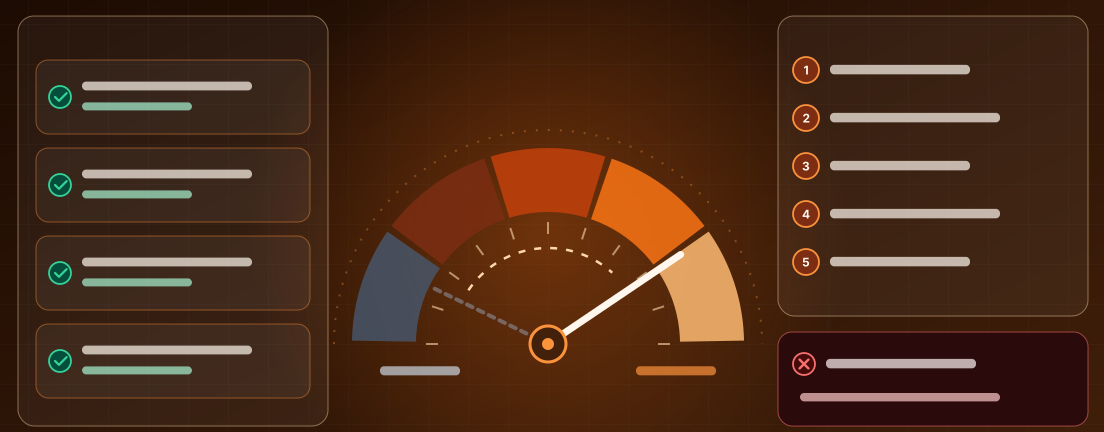
The Dial — Staying Switched On to Security at Work
Being security-aware isn't a technical skill or a once-a-year training — it's keeping the dial turned up: a little calm attention woven through your ordinary work. Security is everyone's business…
The Drill — Commissioning and Learning From a Security Drill
A red team sounds alarming, but it's really a drill: a safe, planned rehearsal in which, with your permission, a team plays a realistic attacker to see how you'd really cope. It's better to find your…
The Line — Using the Access You're Trusted With
The access you're given to systems and data is a trust, lent to you for your job. So just because you can see something doesn't mean you may look at it. Use your access only for your job, don't go…
The Draft — Using AI Output Responsibly
What an AI tool gives you is a draft, not an answer: a fast, useful first version that can be confidently wrong and never knows it. So you stay in charge, check what matters — especially before you…
The Later Button — Why You Shouldn't Put Off Updates
A security update closes a known hole in your software, so pressing 'remind me later' leaves that hole open — and 'later' rarely comes, while attackers race to exploit known holes. So you press…
The First Move — What To Do When Something Goes Wrong
When a security incident happens — a dodgy link clicked, an account acting up, a device lost, a ransom message — the calm first move is simple: stay steady, tell the right person straight away, and…
Travel Light — Holding Only the Personal Data You Need
Every piece of personal data you hold is a liability as well as an asset — a risk and a responsibility, not just something useful. So travel light: collect only what you genuinely need, don't keep…
The Gatekeeper — How a Firewall Protects Your Network
Your network has an inside and an outside, and the firewall is the gate between them. Keep it closed by default, open only the few things you genuinely need, and it blocks the uninvited from the…
The Foundations — Building Security In From the Start
When you get something new built, bought, or set up, security works best built in from the start — like a building's foundations — not bolted on at the end. Ask what needs protecting and what could…
The Safety Copy — Backups That Actually Save You
The single most useful thing you can do to survive a data disaster is keep a safety copy of what matters. But a copy in the same place dies with the original, one copy can fail, a manual one gets…
Not the Office — Looking After the Computers That Run Machines
The computers that run machines and physical processes aren't office PCs, and the office security playbook doesn't fit them. They control physical things, can't just be patched or rebooted, are often…
What's in the Box — Keeping Your Containers Clean
A container is a box that ships everything inside it, so its security is mostly about what's in the box. You build on a base image someone else made — and inherit its problems too. Keep the box…
The Footage — Keeping Records So You Can Look Back
Your systems' logs are their footage — the recorded evidence of what happened. Without it you're blind, live and afterwards. So keep good footage: record the things that would matter if something…
The Warning Ladder — How Serious Is This Weakness?
A reported weakness isn't yet an attack. How urgent it is depends on how close it is to being a usable, working attack — a ladder from 'a weakness is reported' up to 'it's being used in the wild'.…
The Three Safeguards — How a Practice Keeps Health Records Safe
A gentle, practical guide for a small healthcare practice: keeping the health records you hold safe rests on three safeguards held up together — rules & people, doors & desks, and screens & passwords…
The Crossings — Spotting Where Your Data Is At Risk Before You Build
The craft of threat modelling for a small project, made plain: before you build, draw it simply, follow the data through it, and find the crossings — where data passes between what you control and…
The Steering Loop — Governing Security on a Rhythm, Not in a Panic
Security governance in plain words, and in motion: a group steering security on purpose, on a regular rhythm — set the direction, meet on a rhythm, look at what matters, decide and make it stick, and…
The Spot Check — Checking Your Security by Evidence, Not Assuming
The checker's craft in plain words: find out whether your security basics are actually being done by looking, not assuming. Know the field of what could be checked, check a fair sample by evidence…
The Agreed Test — Commissioning a Safe Security Check
A decision-maker's plain guide to safely commissioning and receiving an authorised security test: what such a test is, why written permission is everything, how to agree the scope and rules of…
The Tiers — Protecting Data by How Sensitive It Is
A gentle, practical guide to the plainest idea in data protection: not all data is equal, so sort it by how sensitive it is and protect each level accordingly. Sort it into a few tiers, label it…
The Sealed Room — Handling a Suspicious File Safely
A gentle, non-technical guide to the one habit that keeps a suspicious file from hurting you: treat it as a suspect. Don't run it on your real machine and don't just delete it. Contain it, look at…
The Blueprint — Building Security In From the Start
A gentle, non-technical guide to the plainest idea in security architecture: build security IN when you design, choose, or set something up — don't bolt it on afterwards. Ask the security questions…
The Outbox — Being Careful With What You Send by Email
A gentle, non-technical guide to the other half of email safety — not the threats that arrive, but the mistakes that leave. A send can't be unsent, so a moment's care before you send prevents the…
Digital Marketing — From Zero to Your First Campaign (English + বাংলা)
A twelve-hour, plain-language, hands-on course: find your customers, set up Facebook, Instagram, WhatsApp and Google properly, make content with a phone, run your first small ads, sell through…
Cybersecurity Awareness for Everyone (English + বাংলা)
An eight-hour, plain-language course for anyone with a phone: how ordinary people in Bangladesh actually get scammed and hacked — bKash calls, Facebook links, fake shops, lost phones — and the…
Mid Level · 112 courses
SOC Analyst Command — Working the Live Alert Queue
A sixteen-hour, hands-on-the-console course where you take the analyst's seat on a SOC floor and work real shifts — triaging the queue, investigating to a verdict, responding, escalating, and handing…
Privacy Engineering — Following the Data
A twenty-hour mid-level course where you are a privacy engineer at a consumer health app, following one piece of personal data along its whole journey — collection, use, storage, sharing, retention…
Threat Intelligence Cell — Tradecraft and Judgement
A seventeen-hour mid-level course where you work a financial firm's threat intelligence cell tracking an adversary campaign — turning feeds into decision-ready intelligence on the Diamond Model and…
LLM Application Security — Building AI Features Safely
A twenty-hour, highly interactive mid-level course where you secure an AI assistant along a live LLM-application pipeline — treating the model as untrusted, assuming prompt injection can succeed…
Cyber Resilience & Business Continuity — Ready Before the Disruption
A twenty-hour, highly interactive mid-level course where you are a resilience lead at a logistics company, working along the resilience curve — analysing impact, setting recovery objectives, building…
API Security — The Request Checkpoint
A twenty-hour, highly interactive mid-level course where you secure an API at every request — authenticating the caller, authorizing on the server, validating input, controlling data, limiting…
Network Traffic Analysis — Reading the Wire
A deeply technical, hands-on mid-level course that reads network traffic at the byte and protocol level. Peel each frame apart on the packet dissector — Ethernet, IP, TCP/UDP, and the application…
Linux Server Hardening — The Hardening Bench
A hands-on, workshop-style mid-level course that hardens a Linux server one control at a time. Work the hardening surface board — Accounts, SSH, Services, Firewall, Filesystem, Kernel, Logging…
Web Security — Hardening the Exchange
A hands-on, task-first mid-level course that hardens a real web application one defense surface at a time. Work the exchange inspector across eight surfaces — TLS, headers, cookies, CSP, auth…
IoT Security — The Device Floor
A technical, field-driven course on securing the connected devices a hospital runs but cannot treat like computers — infusion pumps, monitors, cameras, building systems — across eight attack…
Mobile Security — The Fleet in Your Pocket
A technical, hands-on course on securing a fleet of smartphones and tablets — the most personal, portable, and least controllable computers an enterprise runs — across eight aspects of mobile…
Identity & Access Operations — The Lifecycle Rail
A hands-on mid-level course that runs identity as a living pipeline. Work the access lifecycle rail — Request, Approve, Provision, Authenticate, Elevate, Move, Review, Deprovision — driving…
Vulnerability Management Operations — The Remediation Funnel
A hands-on mid-level course that runs vulnerability management as a flow: thousands of raw findings in, a proven-fixed few out. Work the remediation funnel — Discover, Scan, Enrich, Prioritize…
Logging & Telemetry Engineering — The Telemetry Ring
A deeply technical mid-level course that builds the telemetry every detection, investigation, and audit depends on. Follow a security event clockwise around the telemetry ring — Sources, Collect…
Cloud Security Posture Management — The Posture Board
A hands-on mid-level course that operates the security posture of a multi-account cloud estate. Work the posture board — Identity, Network, Data, Compute, Guardrails, Secrets, Visibility, and Posture…
Compliance Operations — The Assurance Staircase
A mid-level course that runs a security compliance program as continuous operations, not an annual scramble. Climb the assurance staircase — Obligations, Scope, Controls, Implement, Evidence…
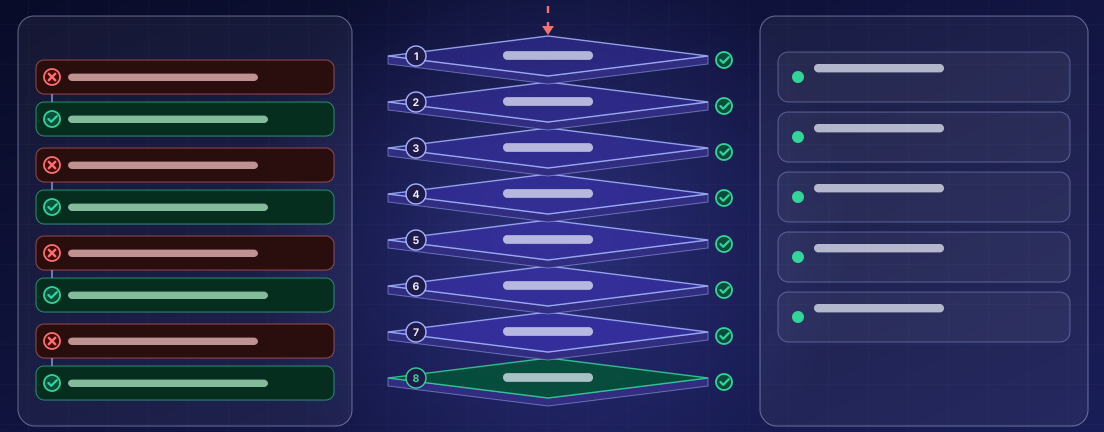
Application Security Engineering — The Defense Stack
A hands-on mid-level course that secures a web application layer by layer, as the engineer who builds and fixes it. Work the defense stack — Edge & Transport, Authentication, Authorization, Input…
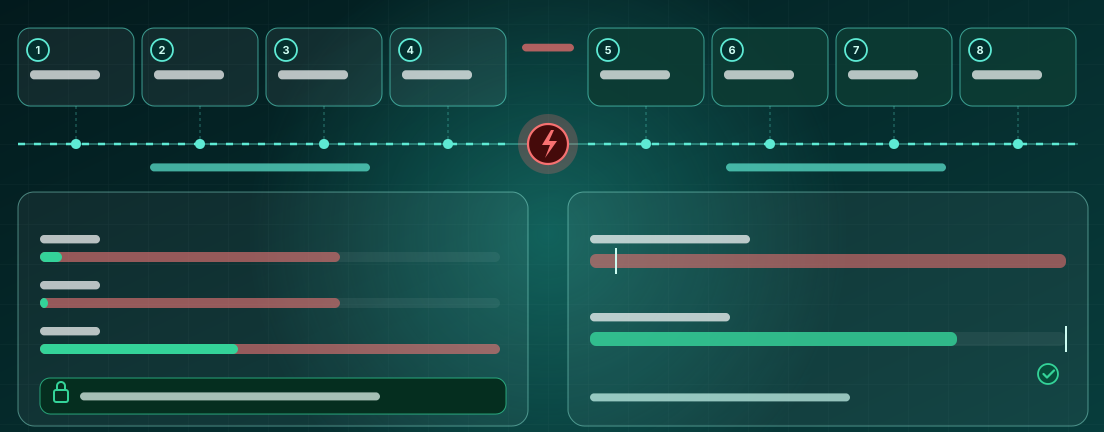
Backup & Recovery Resilience — The Recovery Timeline
A hands-on mid-level course that builds backups which actually restore, and the ability to recover fast and completely from ransomware or disaster. Work the recovery timeline - four readiness stages…
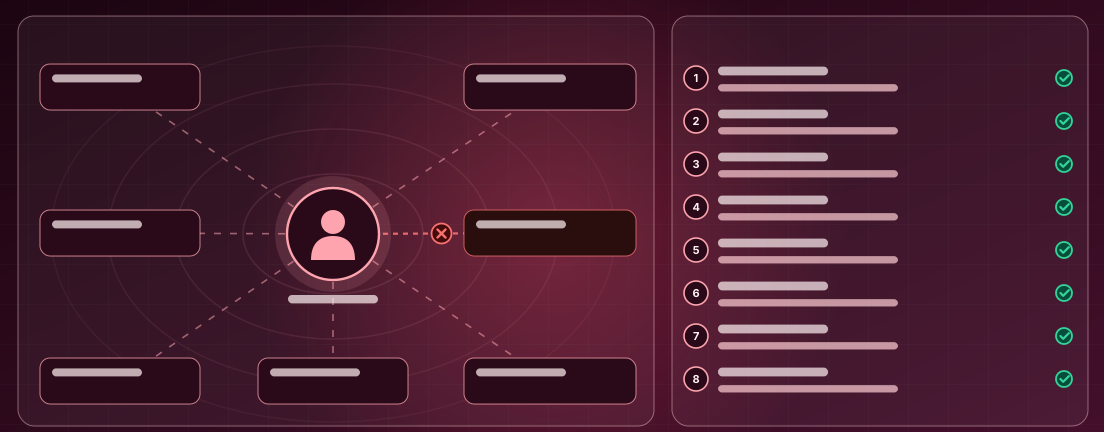
Privacy Engineering — The Privacy Map
A hands-on mid-level course that engineers privacy into a product handling a great deal of personal data. Work the privacy map - the person's data at the centre, protected by eight disciplines: Data…
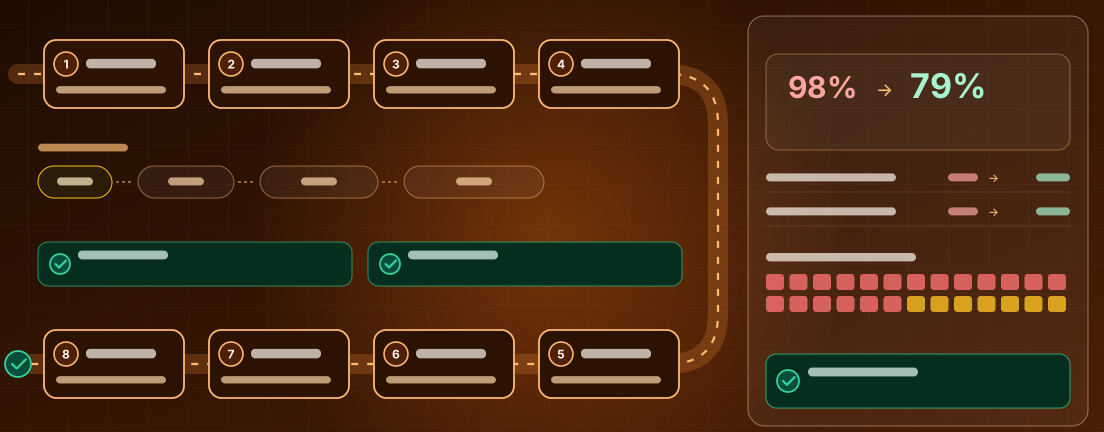
Patch Management Operations — The Patch Pipeline
A hands-on mid-level course that patches a fleet promptly, safely, and verifiably - closing known vulnerabilities before they are exploited without breaking production. Work the patch pipeline…
Configuration Management & Secure Baselines — The Config Lifecycle
A hands-on mid-level course that keeps every system in a known, secure configuration and stops it drifting away. Work the config lifecycle - eight stages: Baseline, Harden, Enforce, Detect…
SaaS Security Posture Management — The SaaS Estate
A hands-on mid-level course that secures the sprawling estate of SaaS applications an organization runs, where most of its data and identity now live. Work the SaaS estate - eight domains: Discovery…
Threat Modeling — The Threat Model Loop
A hands-on mid-level course that finds security problems in a design before they are built, by modeling the system and reasoning about what can go wrong. Work the threat model loop - eight stages a…
Email Security Operations — The Email Defense Stack
A hands-on mid-level course that defends an organization's email against phishing, business email compromise, and malware - the channel most attacks arrive through. Work the email defense stack…
Secure CI/CD Pipeline Security — The Pipeline Gates
A hands-on mid-level course that secures the software delivery pipeline so only trusted, verified code and artifacts reach production and the pipeline itself cannot be turned into an attack. Work the…
IoT & OT Device Security — The OT Security Board
A hands-on mid-level course that secures the operational technology and connected devices running physical processes, where a compromise can stop production or endanger safety. Work the OT security…
Applied Cryptography & Key Management — The Key Lifecycle
A hands-on mid-level course that uses cryptography correctly and manages keys through their whole life. Work the key lifecycle - eight stages a key climbs from birth to retirement: Generate…
Zero Trust Architecture — The Zero Trust Fabric
A hands-on mid-level course that re-architects a network built on implicit trust into one that never trusts and always verifies. Work the zero trust fabric - eight pillars an architect must make…
Detection Engineering — The Detection Pipeline
A hands-on mid-level course that builds detections which catch real attacks without drowning the SOC in noise. Work the detection pipeline - eight stages from idea to measured value: Sources…
Incident Response Operations — The Response Funnel
A hands-on mid-level course that runs a security incident from first alert to lessons learned. Work the response funnel - eight stages a case passes through: Prepare, Detect, Triage, Contain…
Digital Forensics & Evidence Handling — The Evidence Staircase
A hands-on mid-level course that turns a suspect system into defensible evidence. Climb the evidence staircase - eight steps from scene to stand: Identify, Preserve, Acquire, Authenticate, Examine…
Endpoint Detection & Response Operations — The Endpoint Defense Stack
A hands-on mid-level course that operates an EDR/XDR platform across a fleet of endpoints. Work the endpoint defense stack - eight layers from Prevention and Telemetry through Detection, Triage…
Container & Kubernetes Security — The Cluster Security Board
A hands-on mid-level course that hardens containers and the Kubernetes clusters that run them. Work the cluster security board - eight domains: Images, Supply Chain, Cluster Config, Network Policy…
Secrets Management — The Secret Lifecycle
A hands-on mid-level course that keeps API keys, credentials, and tokens out of code and safely managed. Work the secret lifecycle - eight stations: Generate, Store, Distribute, Inject, Rotate…
API Security Engineering — The API Defense Loop
A hands-on mid-level course that secures the REST and GraphQL APIs you build and operate. Work the API defense loop - eight arcs: Inventory, Authentication, Authorization, Input Validation, Rate…
Data Loss Prevention Operations — The DLP Pipeline
A hands-on mid-level course that keeps sensitive data from leaving where it shouldn't. Work the DLP pipeline - eight stages: Classify, Discover, Monitor, Detect, Enforce, Educate, Investigate, and…
DNS Security — The DNS Defense Rail
A hands-on mid-level course that secures resolvers, zones, and DNS traffic. Work the DNS defense rail - eight stations: Resolve, Validate, Filter, Encrypt, Authenticate, Monitor, Harden, and Respond…
DDoS Defense & Mitigation — The DDoS Defense Stack
A hands-on mid-level course that keeps a service online under attack. Work the DDoS defense stack - eight layers: Edge & Anycast, Network Filtering, Rate Limiting, Protocol Defenses, Application…
Database Security — The Database Defense Stack
A hands-on mid-level course that secures the databases behind a payments platform. Work the database defense stack - eight layers: Access Control, Authentication, Encryption, Network Isolation, Query…
Windows Server Hardening — The Hardening Board
A hands-on mid-level course that hardens a fleet of Windows Servers to a defensible baseline. Work the hardening board - eight domains: Accounts, Authentication, Services & Roles, Network, Logging &…
Security Awareness Program Management — The Awareness Loop
A hands-on mid-level course that runs a human-risk program that actually changes behaviour. Work the awareness loop - eight stages: Assess, Plan, Build Content, Deliver, Phishing Simulation, Measure…
Threat Intelligence Operations — The Intelligence Staircase
A hands-on mid-level course that runs a threat-intelligence function that feeds the SOC. Climb the intelligence staircase - eight steps: Direction, Collection, Processing, Analysis, Production…
Network Segmentation & Firewall Engineering — The Segmentation Board
A hands-on mid-level course that carves a flat network into defensible zones. Work the segmentation board - eight domains: Zones & Design, Firewalls, Rule Hygiene, Micro-segmentation, East-West…
Privileged Access Management — The Privilege Lifecycle
A hands-on mid-level course that brings privileged accounts under control. Work the privilege lifecycle - eight stations: Discover, Vault, Broker, Elevate, Session, Rotate, Audit, and Revoke…
TLS & PKI Certificate Management — The Certificate Lifecycle
A hands-on mid-level course that runs certificates and trust without outages or weak crypto. Climb the certificate lifecycle - eight steps: Plan, Generate, Issue, Deploy, Validate, Monitor, Renew…
Ransomware Defense — The Ransomware Defense Stack
A hands-on mid-level course that hardens an organisation against ransomware end to end. Work the ransomware defense stack - eight layers: Email & Web, Endpoint, Identity, Network, Backups, Detection…
Wireless Network Security — The Wireless Security Board
A hands-on mid-level course that secures enterprise Wi-Fi and the airspace around it. Work the wireless security board - eight domains: Architecture, Authentication, Encryption, Segmentation, Rogue…
VPN & Secure Remote Access — The Remote Access Rail
A hands-on mid-level course that gives remote users safe access without opening the network. Work the remote access rail - eight stations: Design, Authenticate, Tunnel, Authorize, Posture, Segment…
Insider Threat Program — The Insider Risk Loop
A hands-on mid-level course that builds a fair, effective insider-risk program. Work the insider risk loop - eight stages: Govern, Identify, Detect, Investigate, Respond, Protect, Educate, and…
Security Automation Engineering — The Automation Pipeline
A hands-on mid-level course that automates repetitive security work safely. Work the automation pipeline - eight stages: Identify, Design, Script, Integrate, Test, Guardrail, Deploy, and Maintain…
PCI DSS Compliance — The Compliance Staircase
A hands-on mid-level course that takes a business through PCI DSS v4.0 as real operations. Climb the compliance staircase - eight steps: Scope, Segment, Protect Data, Control Access, Secure Systems…
Active Directory Security — The AD Defense Board
A hands-on mid-level course that hardens Active Directory - the keys to the kingdom. Work the AD defense board - eight domains: Accounts, Privilege Tiering, Kerberos, Delegation, GPO & Config…
Threat Hunting — The Hunt Staircase
A hands-on mid-level course that proactively hunts adversaries who slipped past detections. Climb the hunt staircase - eight steps: Hypothesize, Scope, Collect, Baseline, Hunt, Analyze, Respond, and…
Cloud Incident Response — The Cloud IR Stack
A hands-on mid-level course that responds to incidents in AWS, Azure, and GCP. Work the cloud IR stack - eight layers: Readiness, Detect, Scope, Preserve, Contain, Eradicate, Recover, and Learn…
Cyber Risk Management — The Risk Loop
A hands-on mid-level course that runs cyber risk as a disciplined, repeatable cycle. Work the risk loop - eight stages: Context, Identify, Analyze, Evaluate, Treat, Monitor, Report, and Improve…
Software Supply Chain Security — The Supply Chain Pipeline
A hands-on mid-level course that secures everything your build trusts. Work the supply chain pipeline - eight stages: Source, Dependencies, Build, Sign, SBOM, Verify, Deploy, and Respond - defending…
Fraud Detection & Prevention — The Fraud Defense Stack
A hands-on mid-level course that stops account and payment fraud without blocking real users. Work the fraud defense stack - eight layers: Signals, Identity, Device, Behaviour, Rules, Models, Review…
Cloud IAM — The Cloud Access Rail
A hands-on mid-level course that gets cloud identity and access right across AWS, Azure, and GCP. Work the cloud access rail - eight stations: Identities, Authenticate, Authorize, Federate, Least…
Security Architecture & Design — The Architecture Board
A hands-on mid-level course that builds security into systems by design. Work the architecture board - eight domains: Requirements, Trust Boundaries, Identity, Data, Network, Resilience, Secure…
Web Application Firewall Operations — The WAF Defense Stack
A hands-on mid-level course that runs a WAF that blocks attacks without blocking customers. Work the WAF defense stack - eight layers: Deployment, Signatures, Rules, Rate Limiting, Bot Defense…
OAuth 2.0 & OIDC Security — The Authorization Staircase
A hands-on mid-level course that implements OAuth 2.0 and OpenID Connect securely. Climb the authorization staircase - eight steps: Flows, Clients, Tokens, Scopes, Validate, Sessions, Federate, and…
Identity Governance & Administration — The Governance Rail
A hands-on mid-level course that governs who has access to what, and proves it. Work the governance rail - eight stations: Sources, Provision, Roles, Request, Approve, Certify, Separate Duties, and…
Serverless Security — The Serverless Security Board
A hands-on mid-level course that secures serverless functions and event-driven apps. Work the serverless security board - eight domains: Identity, Permissions, Code, Dependencies, Secrets, Events…
Password & Authentication Security — The Authentication Pipeline
A hands-on mid-level course that builds authentication attackers can't walk through. Work the authentication pipeline - eight stages: Policy, Storage, Login, MFA, Recovery, Sessions, Passwordless…
Cyber Deception & Honeypots — The Deception Loop
A hands-on mid-level course that catches intruders with deception that produces high-signal alerts. Work the deception loop - eight stages: Strategy, Honeytokens, Honeypots, Placement, Alerting…
Data Governance & Classification — The Data Governance Staircase
A hands-on mid-level course that knows what data you hold, how sensitive it is, and who may touch it. Climb the data governance staircase - eight steps: Inventory, Classify, Label, Own, Control…
Purple Teaming & Detection Validation — The Validation Rail
A hands-on mid-level course that proves your detections work by testing them safely. Work the validation rail - eight stations: Plan, Emulate, Detect, Measure, Gap, Improve, Automate, and Report…
Intrusion Detection & Prevention — The Network Defense Stack
A hands-on mid-level course that detects and blocks attacks in network traffic. Work the network defense stack - eight layers: Sensors, Signatures, Anomaly, Tuning, Prevention, Encrypted Traffic…
Secure Code Review — The Review Staircase
A hands-on mid-level course that finds security bugs in code before they ship. Climb the review staircase - eight steps: Scope, Threats, Inputs, Auth, Data, Crypto, Errors, and Verify - reviewing…
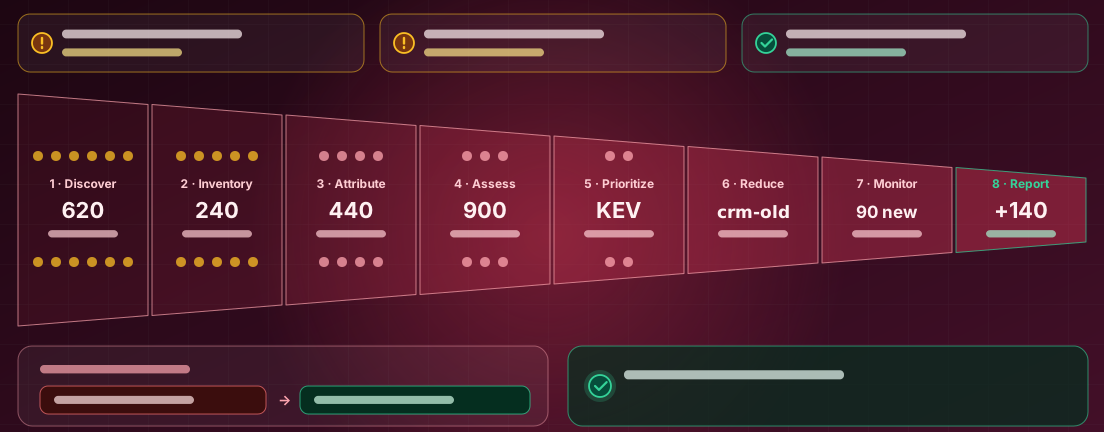
Attack Surface Management — The Attack Surface Funnel
A hands-on mid-level course that finds and shrinks everything an attacker could reach. Work the attack surface funnel - eight stages: Discover, Inventory, Attribute, Assess, Prioritize, Reduce…
ISO 27001 ISMS Implementation — The ISMS Staircase
A hands-on mid-level course that stands up an ISO 27001 information security management system. Climb the ISMS staircase - eight steps: Scope, Leadership, Risk, Controls, Documents, Operate, Audit…
Security Chaos Engineering — The Resilience Rail
A hands-on mid-level course that proves security controls work by safely breaking things on purpose. Work the resilience rail - eight stations: Hypothesize, Scope, Safeguard, Inject, Observe, Learn…
Mobile Device Management — The Device Management Board
A hands-on mid-level course that secures the phones, tablets, and laptops accessing company data. Work the device management board - eight domains: Enrollment, Policy, Encryption, Apps, Separation…
Bug Bounty & Vulnerability Disclosure — The Disclosure Loop
A hands-on mid-level course that runs a vulnerability disclosure and bug-bounty program that researchers respect and the business trusts. Work the disclosure loop - eight stages: Policy, Scope…
Physical Security & Access Control — The Physical Security Board
A hands-on mid-level course that protects the buildings, rooms, and hardware behind the network. Work the physical security board - eight domains: Perimeter, Entry, Access Control, Surveillance, Data…
Network Access Control — The NAC Defense Stack
A hands-on mid-level course that decides what may connect to the network and on what terms. Work the NAC defense stack - eight layers: Discovery, Authentication, Posture, Authorization, Segmentation…
AI & Machine Learning Security — The ML Security Board
A hands-on mid-level course that secures machine-learning systems across their lifecycle. Work the ML security board - eight domains: Data, Training, Model, Supply Chain, Deployment, Inference…
SOC Operations & Alert Triage — The Triage Staircase
A hands-on mid-level course that runs the SOC workflow from alert to closed case. Climb the triage staircase - eight steps: Intake, Enrich, Validate, Scope, Prioritize, Investigate, Escalate, and…
macOS Endpoint Security — The macOS Security Board
A hands-on mid-level course that hardens and manages a fleet of Macs. Work the macOS security board - eight domains: Identity, System Integrity, Gatekeeper, FileVault, Firewall, MDM, Logging, and…
Secure Cloud Migration — The Migration Pipeline
A hands-on mid-level course that moves workloads to the cloud without moving the risk. Work the migration pipeline - eight stages: Assess, Design, Landing Zone, Data, Migrate, Validate, Cutover, and…
Browser & Web Client Security — The Client Defense Stack
A hands-on mid-level course that protects users at the browser, the last mile of most attacks. Work the client defense stack - eight layers: Policy, Extensions, Isolation, Downloads, Credentials, Web…
Post-Quantum Cryptography Readiness — The Migration Rail
A hands-on mid-level course that gets an organisation ready for the quantum threat to today's cryptography. Work the migration rail - eight stations: Threat, Inventory, Prioritize, Standards, Test…
Breach Communication & Crisis Management — The Crisis Loop
A hands-on mid-level course that manages the human, legal, and communication side of a major security incident. Work the crisis loop - eight stages: Prepare, Activate, Assess, Legal, Notify…
Firmware & Hardware Security — The Hardware Trust Board
A hands-on mid-level course that secures the layer below the operating system. Work the hardware trust board - eight domains: Boot, Firmware, Root of Trust, Supply Chain, Interfaces, Storage…
Blockchain & Smart Contract Security — The Contract Staircase
A hands-on mid-level course that secures smart contracts and the applications built on them. Climb the contract staircase - eight steps: Model, Access, Arithmetic, Reentrancy, Oracles, Keys, Test…
HIPAA Security & Privacy Compliance — The Compliance Staircase
A hands-on mid-level course that makes a healthcare organisation genuinely HIPAA-compliant. Climb the compliance staircase - eight steps: Scope, Risk, Administrative, Physical, Technical, Privacy…
Secure Collaboration & Messaging — The Collaboration Defense Stack
A hands-on mid-level course that secures the chat, file-sharing, and meeting tools work now runs on. Work the collaboration defense stack - eight layers: Identity, Access, Sharing, Apps, Data…
OT & ICS Incident Response — The OT Response Funnel
A hands-on mid-level course that responds to incidents in operational technology without endangering the process. Work the OT response funnel - eight stages: Prepare, Detect, Triage, Isolate…
Deepfake & Media Authenticity Defense — The Authenticity Board
A hands-on mid-level course that defends against deepfakes and synthetic-media fraud. Work the authenticity board - eight domains: Awareness, Voice, Video, Identity, Verification, Provenance…
Vendor Security Assessment — The Assessment Rail
A hands-on mid-level course that assesses and manages the security of the vendors you depend on. Work the assessment rail - eight stations: Intake, Tier, Assess, Evidence, Score, Contract, Monitor…
Security Champions Program — The Champions Loop
A hands-on mid-level course that scales security into engineering through a champions program. Work the champions loop - eight stages: Case, Recruit, Enable, Empower, Engage, Measure, Sustain, and…
Infrastructure as Code Security — The IaC Pipeline
A hands-on mid-level course that ships cloud infrastructure that is secure by default. Work the IaC pipeline - eight stages: Author, Modules, Secrets, Scan, Policy, Review, Deploy, and Drift…
Service Mesh Security — The Mesh Security Board
A hands-on mid-level course that secures service-to-service traffic with a service mesh. Work the mesh security board - eight domains: Identity, mTLS, Authorization, Traffic, Ingress, Secrets…
Payment Systems Security — The Payment Defense Stack
A hands-on mid-level course that secures how money moves through an application. Work the payment defense stack - eight layers: Data, Tokenization, Encryption, 3-D Secure, Fraud, APIs…
NIST Cybersecurity Framework — The CSF Loop
A hands-on mid-level course that uses the NIST Cybersecurity Framework 2.0 to run a real security program. Work the CSF loop - eight stages built on the six functions: Govern, Identify, Protect…
Digital Identity & KYC Security — The Identity Assurance Rail
A hands-on mid-level course that verifies people online without being fooled by fraud. Work the identity assurance rail - eight stations: Enrol, Verify, Document, Biometric, Liveness, Risk, Reverify…
SOC 2 Compliance — The SOC 2 Staircase
A hands-on mid-level course that earns and keeps a clean SOC 2 report. Climb the SOC 2 staircase - eight steps: Scope, Criteria, Controls, Evidence, Readiness, Audit, Report, and Sustain…
Event Streaming & Message Queue Security — The Streaming Pipeline
A hands-on mid-level course that secures Kafka and the message queues at the heart of modern systems. Work the streaming pipeline - eight stages: Authenticate, Authorize, Encrypt, Topics, Schema…
Bluetooth, NFC & Wireless Protocol Security — The Wireless Protocol Board
A hands-on mid-level course that secures the short-range wireless protocols on the devices around us. Work the wireless protocol board - eight domains: Bluetooth, BLE, Pairing, NFC, RFID, Zigbee…
Cloud Detection Engineering — The Cloud Detection Stack
A hands-on mid-level course that builds detections specifically for cloud control planes and cloud-native services - not a generic detection pipeline, not incident response. Work the cloud detection…
Cloud Network Security — The Cloud Network Board
A hands-on mid-level course that builds cloud-native network controls from the ground up. Work the cloud network board - eight controls an engineer must make secure by default: VPC Design, Security…
Windows Endpoint Hardening — The Workstation Board
A hands-on mid-level course that hardens the Windows 11 laptop fleet a real organization issues to its people, working the eight domains of the workstation board - Baseline, Local Admin, Attack…
Virtualization & Hypervisor Security — The Hypervisor Rail
A hands-on mid-level course that hardens and operates the hypervisor layer underneath every VM and clinical system. Work the hypervisor rail - eight stations: Host Hardening, Management Plane, VM…
SIEM Operations — The SIEM Funnel
A hands-on mid-level course that runs the daily operation of a SIEM - onboarding sources, keeping parsing and normalization correct, enriching events with context, correlating signal into meaningful…
Secure File Transfer & B2B Integration — The Transfer Staircase
A hands-on mid-level course securing machine-to-machine and partner file transfer across the eight-step Transfer Staircase - Inventory, Protocols, Authentication, Encryption, Integrity, Automation…
Medical Device & IoMT Security — The Clinical Device Board
A hands-on mid-level course that secures the connected medical devices and IoMT clinicians use to treat patients, where a compromise can put a life at risk. Work the clinical device board - eight…
Zero-Day & Critical Vulnerability Response — The Emergency Funnel
A hands-on mid-level course that runs the emergency playbook for the day a critical, often actively-exploited vulnerability drops in software you already run. Work the emergency funnel across eight…
Application Control & Allowlisting — The Allowlist Rail
A hands-on mid-level course that controls what is allowed to run on a fleet you own. Work the allowlist rail across eight stations - Inventory, Policy Design, Audit Mode, Publisher Rules, Path & Hash…
Source Control Platform Security — The Repository Loop
A hands-on mid-level course that hardens the source control platform itself - org and repo access, branch rules, secret scanning, commit signing, tokens, apps, and audit - through the repository…
Security Baseline Audit — The Audit Loop
A hands-on mid-level course that runs a security baseline audit end to end, proving whether an organization is actually at the security baseline it chose. Work the audit loop - eight stages an audit…
Use of AI — Prompt Engineering to Agentic AI: The Masterclass (English + বাংলা)
An eighteen-hour, hands-on course that takes you from writing your first good prompt to shipping a governed, evaluated AI agent — structured outputs, retrieval, tool use, agent loops, multi-agent…
PHP2Shell — Defending Against Critical PHP RCE (CVE-2026-109618 & CVE-2026-109619) (English + বাংলা)
A ten-hour, hands-on defender's course on the two critical PHP engine vulnerabilities disclosed in October 2026: understand how they work, find every affected PHP in your estate, patch and restart…
Senior Level · 110 courses
Purple Team Range — Adversary Emulation and Detection, Side by Side
A seventeen-hour senior course where red and blue work side by side on an authorized range, walking the attack lifecycle technique by technique — emulating each move safely, verifying whether…
OT & ICS Security Field Assessment — Securing the Plant Floor
A twenty-six-hour senior field-operations course where you are the lead OT/ICS security assessor at a water utility, working the plant on a live Purdue-model zone map — reframing IT instincts around…
Cybersecurity Audit — The Workpaper
A twenty-six-hour senior evidence-room course where you are a cybersecurity auditor at a bank, working every control on a live audit workpaper — testing assertions against evidence, sampling…
Penetration Testing — The Authorized Engagement
A twenty-two-hour senior course where you conduct a fully authorized penetration test along an engagement kill chain — scoping and rules of engagement, careful reconnaissance and access, proving…
Threat Modeling — The Design-Time Studio
A twenty-hour, highly interactive senior-level course where you are a security architect finding design flaws before they are built — modeling systems as data-flow diagrams with trust boundaries…
Incident Response — The Response Lifecycle
A thorough, highly interactive senior course where you lead incident response at the Ridgeline CSIRT with method over panic. Run the full lifecycle as a loop — Prepare, Detect, Triage, Contain…
Third-Party Risk Management — The Vendor Risk Desk
A strategic, decision-focused senior course on managing the risk of the vendors you rely on. Run the vendor risk desk at Harborline — moving each third party through Identify, Tier, Assess, Decide…
Web Application Security — The Test Bench
A hands-on, senior-level course that tests and fixes web application vulnerabilities the professional way: probe a surface safely, read the response, then fix the code and re-test until the flaw is…
SaaS Security — Posture Command
A deeply technical senior course on securing the SaaS estate an organization uses — not the infrastructure it builds. Work the SaaS posture board across eight control surfaces — estate, identity, app…
Cyber Law & Ethics — Where the Line Is
A strategic, decision-driven senior course on the legal and ethical boundaries of security work — the 'can we / should we' questions a professional must answer defensibly. Work every dilemma on the…
Model Risk Management — Governing the Models
A senior, decision-driven course on governing the risk that an organization's models — credit, fraud, pricing, and now AI/LLM models — are wrong, misused, or quietly decaying, across eight dimensions…
Security Leadership & CISO Foundations — The Leadership Loop
A senior-level course that steps up from running security work to leading a security function. Work the leadership loop - eight arenas: Strategy, Team, Budget, Board, Risk, Culture, Crisis, and…
Cloud Security Architecture — The Architecture Board
A senior-level course that designs secure, scalable architecture across a multi-account, multi-cloud estate. Work the architecture board - eight domains: Landing Zone, Identity, Network, Data…
Security Operations Center Management — The SOC Management Rail
A senior-level course that runs a SOC as a high-performing function, not just an alert queue. Work the SOC management rail - eight stations: Mission, People, Process, Detection, Automation, Metrics…
Detection Engineering at Scale — The Detection Program Staircase
A senior-level course that runs detection engineering as a disciplined program across a large estate. Climb the program staircase - eight steps: Strategy, Coverage, Pipeline, Detection-as-Code…
Security Governance & Board Reporting — The Governance Loop
A senior-level course that governs a security program and reports it honestly to leadership and the board. Work the governance loop - eight arenas: Charter, Policy, Risk, Committees, Metrics…
Enterprise Identity Architecture — The Identity Fabric Board
A senior-level course that designs the identity fabric a whole enterprise runs on. Work the identity fabric board - eight domains: Directory, Authentication, Federation, Authorization, Lifecycle…
Application Security Program Leadership — The AppSec Program Pipeline
A senior-level course that builds an application security program that scales with engineering. Work the program pipeline - eight stages: Strategy, SSDLC, Tooling, Triage, Champions, Training…
Major Incident Command — The Incident Command Funnel
A senior-level course that commands a major security incident - the kind that pulls in executives, legal, and the whole company. Work the incident command funnel - eight stages: Declare, Command…
Threat-Informed Defense — The Defense Program Staircase
A senior-level course that aligns defense to the adversaries who actually target you. Climb the defense program staircase - eight steps: Threats, Map, Prioritize, Assess, Emulate, Close, Measure, and…
Enterprise Data Protection Strategy — The Data Protection Board
A senior-level course that protects data across a whole enterprise, from creation to deletion. Work the data protection board - eight domains: Discovery, Classification, Encryption, Access, DLP…
Cyber Resilience & Business Continuity — The Resilience Loop
A senior-level course that keeps the business running through disruption and cyber crisis. Work the resilience loop - eight stages: Analyze, Prioritize, Plan, Backup, Rehearse, Respond, Recover, and…
Zero Trust Program Strategy — The Zero Trust Roadmap Rail
A senior-level course that leads an organisation-wide zero trust transformation, not just a product rollout. Work the roadmap rail - eight stations: Vision, Assess, Prioritize, Identity, Network…
Human Risk Management — The Human Risk Loop
A senior-level course that runs a human-risk program that measurably changes behaviour. Work the human risk loop - eight stages: Measure, Segment, Target, Intervene, Nudge, Phish, Culture, and…
M&A Cybersecurity Due Diligence — The Deal Rail
A senior-level course that assesses and integrates cyber risk through mergers and acquisitions. Work the deal rail - eight stations: Scope, Discover, Assess, Quantify, Report, Negotiate, Integrate…
Product Security & PSIRT Leadership — The Product Security Pipeline
A senior-level course that secures the products a company ships and handles their vulnerabilities responsibly. Work the product security pipeline - eight stages: Design, Build, Ship, SBOM, Disclose…
Regulatory Compliance Strategy — The Compliance Program Staircase
A senior-level course that runs compliance across many overlapping regulations without duplicating work. Climb the compliance program staircase - eight steps: Landscape, Map, Harmonize, Controls…
Platform Security Engineering — The Paved Road Board
A senior-level course that makes the secure way the easy way for hundreds of engineers. Work the paved road board - eight domains: Baselines, Pipelines, Templates, Guardrails, Secrets, Identity…
Security Data Engineering — The Security Data Rail
A senior-level course that builds the data backbone detection and response run on. Work the security data rail - eight stations: Sources, Ingest, Normalize, Enrich, Store, Model, Serve, and Cost…
Cyber Risk Quantification — The Quantification Staircase
A senior-level course that puts credible numbers on cyber risk so leaders can decide. Climb the quantification staircase - eight steps: Scope, Model, Frequency, Magnitude, Data, Simulate…
OT Security Program Leadership — The OT Program Board
A senior-level course that leads a security program for operational technology where safety comes first. Work the OT program board - eight domains: Governance, Inventory, Zones, Access, Monitoring…
Vulnerability Management Program Leadership — The VM Program Funnel
A senior-level course that runs vulnerability management as a measurable, enterprise-wide program. Work the VM program funnel - eight stages: Strategy, Coverage, Prioritize, Orchestrate, Remediate…
Cyber Threat Intelligence Program — The CTI Program Staircase
A senior-level course that builds a threat-intelligence program that actually changes decisions. Climb the CTI program staircase - eight steps: Mission, Requirements, Collection, Analysis…
Privacy Program Leadership — The Privacy Program Loop
A senior-level course that runs an enterprise privacy program a DPO can stand behind. Work the privacy program loop - eight stages: Govern, Map, Lawful Basis, Rights, Assess, Vendors, Breach, and…
Security Culture & Change Management — The Culture Loop
A senior-level course that changes how an organisation thinks and acts about security. Work the culture loop - eight stages: Assess, Vision, Sponsor, Message, Enable, Embed, Measure, and Sustain…
Enterprise Cryptography & Key Management Program — The Crypto Program Board
A hands-on senior-level course that runs the enterprise program making every team's use of cryptography governed, inventoried, keyed, certificated, vaulted, and quantum-ready. Work the crypto program…
Enterprise Network Security Architecture — The Network Rail
A senior-level architecture course that designs the enterprise network security architecture itself, not a single firewall or a single segment. Work the network security rail - eight layers a…
Security Automation & SOAR Program Leadership — The Automation Staircase
A senior-level program-leadership course that leads a SOC automation program end to end. Climb the automation staircase - eight steps from Case to Scale: Case, Use-Cases, Platform, Playbooks…
Insider Risk Program Leadership — The Insider Risk Funnel
A senior-level program-leadership course that runs an insider risk program which protects the organisation while respecting the people in it. Work the insider risk funnel - eight stages a responsible…
Kubernetes & Container Security Architecture — The Container Defense Stack
A hands-on senior-level architecture course that designs container and Kubernetes security as a defense-in-depth stack across a large multi-cluster estate. Work the container defense stack - eight…
API Security Program Leadership — The API Security Loop
A senior-level course that runs an organization-wide API security program, not a single API review, by working the API Security Loop - eight arcs from Inventory through Monitor - to find every API…
Security Operating Model & Organisation Design — The Operating Model Loop
A senior-level course that designs the security organisation itself. Work the operating model loop - eight arcs a head of security must get right: Mandate, Structure, Roles, Sourcing, Interfaces…
Security Investment Strategy & Business Case — The Investment Staircase
A senior-level course that builds the discipline of deciding, justifying, funding, delivering, and proving the value of security investment. Climb the investment staircase - eight steps: Baseline…
MSSP & MDR Oversight — The Outsourcing Funnel
A senior oversight course that governs and gets real value from outsourced security services - never runs them. Work the outsourcing funnel - eight stages an outsourcing relationship passes through…
Multi-Cloud Security Governance — The Cloud Governance Board
A senior-level course that governs cloud security across hundreds of AWS accounts, dozens of Azure subscriptions, and a growing GCP footprint. Work the cloud governance board - eight tiles: Landing…
Software Supply Chain Security Program — The Provenance Funnel
A senior-level, program-scale course that runs software supply chain security as an org-wide program, not a single pipeline. Work the provenance funnel - eight stages: Scope, Inventory, Standards…
Customer Identity & Access Management Architecture — The Customer Identity Rail
A senior architecture course that builds and defends the identity system tens of millions of customers sign in through. Work the customer identity rail - eight stations: Registration, Authentication…
Security Architecture Governance & Design Authority — The Design Authority Loop
A senior-level course that builds the design authority function governing security architecture across a whole enterprise. Work the design authority loop - eight arcs: Principles, Reference…
Enterprise Endpoint Security Architecture — The Endpoint Defense Stack
A senior-level architecture course that designs the target-state endpoint security architecture for a global fleet of tens of thousands of Windows, macOS, Linux, and mobile devices - the tooling…
Cyber Exercise & Tabletop Program — The Exercise Staircase
A senior-level course that builds a cyber exercise program end to end. Climb the exercise staircase - eight steps: Objectives, Audience, Scenario Design, Injects, Facilitation, Evaluation, Findings…
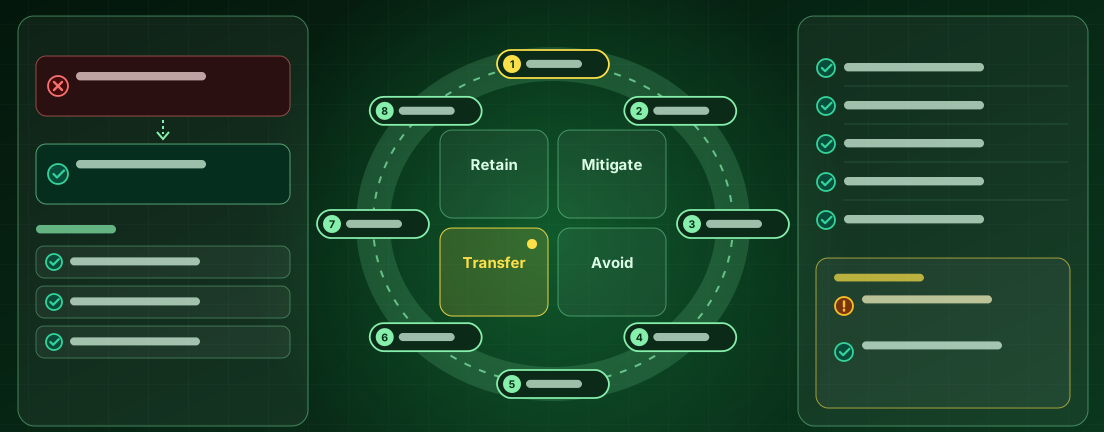
Cyber Insurance & Risk Transfer Strategy — The Risk Transfer Loop
A senior-level course that builds the discipline of deciding what cyber risk to retain, mitigate, transfer, or avoid, and buys and uses cyber insurance well when transfer is the right tool. Work the…
Cross-Border Data & Sovereignty Strategy — The Sovereignty Board
A senior-level course that builds the strategy deciding where regulated data may live, how it may move, and how to architect and govern for it. Work the sovereignty board - eight tiles: Data Map…
Fraud & Financial Crime Risk Program — The Fraud Risk Funnel
A senior-level program-leadership course that runs the enterprise fraud and financial-crime risk program at a digital bank and payments company. Work the fraud risk funnel - eight stages: Threat…
Converged Physical & Cyber Security Program — The Convergence Board
A strategic senior-level course that builds one converged security program out of two teams that used to run apart. Work the convergence board - eight tiles: Shared Risk Picture, Governance, Access…
Threat Hunting Program Leadership — The Hunt Program Staircase
A senior-level course that builds and leads a threat hunting program, not a single hunt. Climb the hunt program staircase - eight steps: Charter, Hypotheses, Data Readiness, Hunt Cadence, Tradecraft…
Enterprise Forensic Readiness Program — The Evidence Rail
A senior-level program course that builds the enterprise capability to investigate your own incidents before one ever happens. Work the evidence rail - eight stations: Scenarios, Evidence Sources…
Security Assurance & Testing Strategy — The Assurance Funnel
A strategic senior-level course that builds the org-wide assurance strategy deciding what gets tested, how often, by whom, and how the results are governed - not how to run any single engagement.…
Secure-by-Design Product Strategy — The Secure-by-Design Loop
A senior-level strategy course that shifts the burden of security from customers to the product itself, at the company level. Work the secure-by-design loop across eight arcs - Principles, Secure…
Security Tooling Strategy & Rationalization — The Tooling Board
A senior-level course that rationalizes a security stack grown by accretion into a portfolio someone actually runs on purpose. Work the tooling board - eight tiles: Capability Map, Coverage Gaps…
Identity Threat Detection & Response — The Identity Defense Stack
A senior-level program course that builds identity-centric detection and response across an organization's entire identity fabric - Entra ID, on-prem AD, and Okta. Work the identity defense stack…
Digital Operational Resilience — DORA & NIS2 Program — The Resilience Staircase
A senior program-level course that builds the digital operational resilience program a supervisor can actually test. Climb the resilience staircase - eight steps: Scope & Applicability, ICT Risk…
Legacy Systems & Modernization Security — The Modernization Rail
A senior-level architecture course that secures a legacy estate - mainframe, unsupported middleware, end-of-life Windows Server - while it is modernized out from under itself. Work the modernization…
Continuous Controls Monitoring & Compliance Automation — The Controls Funnel
A senior-level GRC engineering course that turns controls into automated, evidence-producing tests so compliance is continuous rather than an annual scramble. Work the controls funnel - eight stages…
Data Center & Hosting Security Architecture — The Data Center Stack
A senior-level architecture course that designs and defends the end-to-end security of owned and colocated data centres - physical through platform through operations and exit - for a…
Cybersecurity Workforce & Talent Strategy — The Talent Loop
A senior-level course that builds the security team's own workforce and talent strategy. Work the talent loop - eight arcs: Workforce Plan, Role Design, Hiring, Onboarding, Skills Development, Career…
Enterprise Messaging & Collaboration Security Architecture — The Collaboration Defense Stack
A senior-level architecture course that designs and defends the whole collaboration estate of a global law firm. Work the collaboration defense stack - eight layers: Identity & Tenant Trust, Email…
Edge & CDN Security Architecture — The Edge Security Board
A senior-level architecture course that builds the end-to-end security of the internet edge across one or more CDNs. Work the edge security board - eight tiles: DNS & Anycast, TLS & Certificates, WAF…
Database & Data Platform Security Architecture — The Data Platform Rail
A senior architecture course that designs and hardens security across an entire enterprise data platform - hundreds of relational and NoSQL databases, a cloud data warehouse, and a data lake - not…
AI Governance & Risk Management Program — The AI Governance Loop
A senior-level course that builds the enterprise program governing every AI/ML system an organization runs or buys. Work the AI governance loop - eight arcs: AI Inventory, Risk Classification, Policy…
Generative AI & LLM Security Program — The GenAI Security Funnel
A senior-level engineering program that secures generative-AI and LLM systems across an enterprise, end to end - from a proposed use case through a safely-monitored production system. Work the GenAI…
PCI DSS Compliance Program Leadership — The Compliance Staircase
A senior-level strategic course that leads the enterprise PCI DSS program at a multi-brand retailer. Climb the compliance staircase - eight steps: Scope Definition, Segmentation & Scope Reduction…
FedRAMP & Government Cloud Authorization Program — The Authorization Staircase
A senior GRC program course that runs a FedRAMP Moderate authorization end to end. Climb the authorization staircase - eight steps: Strategy & Sponsor, Boundary & Inventory, Control Implementation…
CMMC & NIST SP 800-171 Compliance Program — The Defense Compliance Staircase
A strategic senior-level course that builds a defense industrial base compliance program from a live DoD contract through a passed C3PAO assessment and beyond. Climb the defense compliance staircase…
SOX IT General Controls Program — The ITGC Funnel
A strategic senior-level course that runs the company-side SOX IT general controls program end to end. Work the ITGC funnel - eight stages: Financial Scoping, System Inventory, Control Design, Access…
ISO/IEC 27001 Certification Program Leadership — The Certification Staircase
A senior-level program-leadership course that leads an ISO/IEC 27001:2022 certification program end to end. Climb the certification staircase - eight steps: Business Case & Scope, Context &…
HIPAA Security & Privacy Compliance Program Leadership — The HIPAA Program Loop
A senior-level HIPAA compliance program leadership course built on the HIPAA program loop - eight arcs: Covered Scope & PHI Map, Risk Analysis, Safeguards Program, Policies & Workforce, Business…
Enterprise Data Loss Prevention Program — The DLP Program Funnel
A senior-level program-leadership course that builds and runs an enterprise DLP program end to end. Work the DLP program funnel - eight stages: Data Discovery, Classification Scheme, Policy Design…
Enterprise Wireless & Mobility Security Architecture — The Mobility Rail
A senior-level architecture course that designs and governs the wireless and mobile estate of a large, distributed retail and logistics enterprise. Work the mobility rail - eight stations: RF & Site…
Enterprise PKI & Certificate Lifecycle Program — The PKI Staircase
A senior-level program course that builds and runs an enterprise public-key infrastructure as a whole system. Climb the PKI staircase - eight steps: Trust Architecture, CA Hierarchy & Ceremony…
Mainframe & Midrange Security Program — The Mainframe Rail
A senior-level program course that runs the security program for a bank's mainframe and midrange estate. Work the mainframe rail - eight stations: Estate & Risk Picture, ESM & Access Control…
Network Detection & Response Program — The Network Visibility Stack
A senior-level program-building course that takes a network from EDR-only and blind to actually watched, detected, and defended. Work the network visibility stack - eight layers: Sensor Placement…
Cyber Deception & Threat Engagement Program — The Deception Loop
A senior-level program-build course that catches intruders early, with high fidelity, inside your own environment. Work the deception loop across eight arcs - Objectives & Threat Model, Deception…
Malware Defense & Sandboxing Program — The Malware Defense Funnel
A senior-level operations course that builds and runs an enterprise malware defense program end to end. Work the malware defense funnel - eight stages: Threat Picture, Prevention Layers, Sandbox…
Ransomware Resilience Program — The Resilience Staircase
A senior-level, board-answerable program that climbs eight steps from an honest exposure baseline to proven assurance: Threat & Exposure Baseline, Initial-Access Hardening, Privilege & Lateral…
Cyber Crisis Management & Communications Program — The Crisis Funnel
A strategic senior-level course that builds the enterprise cyber crisis management program sitting above any single incident. Work the crisis funnel - eight stages: Crisis Framework, Activation &…
Post-Merger Security Integration Program — The Integration Rail
A senior-level program course that runs the security work of integrating an acquired company after the deal closes - the part due diligence never reaches. Work the integration rail - eight stations…
Virtual CISO & Security Advisory Practice — The Advisory Board
A senior-level course that builds a fractional CISO advisory practice across the eight tiles of the advisory board - Engagement Scoping, Rapid Assessment, Risk-Led Roadmap, Governance Setup, Board &…
Security Policy & Standards Management Program — The Policy Staircase
A senior-level program course that turns a decade of accumulated, contradictory policy into a living document hierarchy people actually read, follow, and can be audited against. Climb the policy…
Critical Infrastructure Protection Program — The CIP Board
A senior-level program-management course that runs the regulated compliance-and-resilience program keeping a bulk electric system operator both audit-ready and genuinely resilient. Work the CIP board…
Enterprise IoT Security Program — The IoT Program Board
A senior-level program course that builds and runs the enterprise IoT security program for a global hospitality and real-estate portfolio - tens of thousands of smart locks, cameras, HVAC/BMS…
Telecom & 5G Network Security Architecture — The Telecom Rail
A senior-level architecture course that secures a national mobile network operator's own 5G standalone network end to end. Work the telecom rail - eight stations: Threat Landscape & Regulation, RAN &…
Connected Vehicle & Automotive Security Program — The Vehicle Security Funnel
A senior-level, standards-driven course that builds and runs a vehicle manufacturer's cybersecurity program end to end. Work the vehicle security funnel - eight stages: Regulatory & Standards…
Healthcare Delivery Security Program — The Clinical Security Loop
A senior-level program course that runs a healthcare delivery organisation's security program through the lens that makes healthcare different: patient safety, not just data. Work the clinical…
Financial Services Security Program — The Financial Security Board
A senior-level course that runs the whole security program for a regulated bank rather than one piece of it. Work the financial security board - eight tiles: Regulatory Landscape, Core Banking &…
Records & Information Lifecycle Governance — The Lifecycle Staircase
A strategic senior-level course that builds the program keeping only what a firm must keep, and proving it. Climb the lifecycle staircase - eight steps: Information Inventory, Classification &…
Post-Quantum Cryptography Migration Program — The Migration Funnel
A senior-level, program-strategic course that runs the enterprise migration to post-quantum cryptography before harvest-now-decrypt-later attacks and a future cryptographically relevant quantum…
Blockchain & Digital Asset Security Program — The Digital Asset Rail
A senior-level, program-wide course that builds and runs a defensible digital-asset security program for a regulated custodian and exchange. Work the digital asset rail - eight stations from threat…
DevSecOps Transformation Program — The Transformation Staircase
A senior-level program-leadership course that leads an organisation-wide DevSecOps transformation, not a single pipeline. Climb the transformation staircase - eight steps from an honest current-state…
Phishing & Social Engineering Defense Program — The Anti-Phishing Stack
A senior-level program course that builds and runs a dedicated, cross-channel anti-phishing program for a global professional-services firm. Work the anti-phishing stack - eight layers from threat…
Attack Surface Management Program — The Exposure Funnel
A senior-level operations and program course that builds and runs a defensive attack surface management program - discovering, validating, and reducing an organization's own exposure, never anyone…
Cloud Workload Protection Program — The Workload Board
A senior-level program course that builds a cloud workload protection program spanning every workload type a fast-growing fintech actually runs, closing coverage gaps across inventory, image…
Privileged Access Management Program — The Privilege Rail
A senior architecture-studio course that builds and runs a program governing the organization's own privileged access. Work the privilege rail - eight stations from Privilege Discovery & Risk Case…
Identity Governance & Administration Program — The Governance Staircase
A senior-level program course that builds and runs identity governance for an organization's own workforce, contractor, partner, and non-human identities across eight steps: Identity Landscape &…
Cyber Range & Defender Training Program — The Readiness Staircase
A senior-level program course that builds and runs a defensive cyber range for a national retail bank, climbing eight steps from a funded business case through isolated architecture, realistic…
Open Source Security Program — The Dependency Funnel
A senior-level program course that secures an organization's own use of open source, deliberately and continuously, from charter through governance, across eight stages of the dependency funnel…
Mobile Application Security Program — The Mobile Defense Stack
A senior-level program course that builds and runs a mobile application security program defending an organization's own iOS and Android apps and the customers who use them, working the mobile…
Retail & Payment Security Program — The Storefront Board
A senior-level program course that runs the security program protecting an omnichannel retailer's stores, e-commerce site, and payment flows across the eight-tile storefront board — threats and…
Energy & Utility Security Program — The Grid Rail
A senior-level program course that builds and runs the security program protecting a regional electric and gas utility's own grid, working the eight-station grid rail from sector threat and…
SaaS Vendor Assurance Program — The Assurance Funnel
A senior-level GRC program course that builds and runs the assurance program covering your own SaaS vendors - discover the full portfolio, tier by inherent risk, actually read due-diligence evidence…
Security Operations Strategy — The Operations Strategy Loop
A hands-on senior-level course that builds the multi-year strategy turning a fragmented, acquisition-built SOC into a deliberate function - name the mission and outcomes, assess maturity honestly…
Expert Level · 105 courses
DFIR Evidence Room — Reconstructing the Breach from the Artifacts
An eighteen-hour expert investigation where you lead a breach case end to end — preserving evidence, reconstructing the forensic timeline across endpoint, memory, log, network, cloud, and identity…
AI Security Assurance — Securing and Assuring AI Systems
A twenty-two-hour expert course where you assure an enterprise's AI systems across every layer — data, model, supply chain, inference, tools and agents, and the surrounding application — treating…
Cloud Security Architecture — Identity, Blast Radius, and the Attack Path
A twenty-four-hour expert course where you are a cloud security architect hardening a large multi-account estate along a live attack-path graph — treating identity as the perimeter, misconfiguration…
Malware Analysis — Decode the Threat
A twenty-hour, highly interactive expert-level course where you are a malware analyst working an escalation ladder inside an isolated lab — triage, static, unpacking, dynamic, network, and code-level…
Supply Chain Security — The Chain of Verified Trust
A twenty-hour, highly interactive expert-level course where you secure the software supply chain link by link — source, dependencies, build, artifacts, distribution, and deployment — knowing what is…
Container & Kubernetes Security — The Stack
A twenty-hour, highly interactive expert-level course where you secure a Kubernetes platform layer by layer — image, registry, cluster, workload, network, runtime. Containers share the host kernel so…
SIEM Engineering — The Detection Pipeline
A deeply technical expert course that builds and assures the detection pipeline itself — the eight-stage machine that turns raw events into trustworthy alerts. Engineer sources, collection, parsing…
SOAR Automation — Building the Machine That Responds
An expert, build-it-yourself course on security orchestration and automated response: construct a SOAR practice playbook by playbook — hardened triggers, enrichment engines, versioned decision…
OT & ICS Security Engineering — Building the Defended Plant
A twenty-three-hour expert engineering course where you architect the defended plant end to end on a live zone-and-conduit floor plan — partitioning zones and conduits to target security levels…
Exploit Development — The Exploitability Verdict
The defender's mastery of exploitation: understanding how a bug becomes an exploit well enough to render a verdict on whether it can, defeat it barrier by barrier, and fix the class at the root…
PHI Safeguards Defensibility — The Defensibility Funnel
An expert GRC course that builds regulatory defensibility on top of an already-running HIPAA program - designing risk analysis, safeguards, evidence, breach determinations, and business-associate…
Threat Modeling at Scale — The Trust Boundary Loop
An expert-level, program-optimisation course in threat modeling at scale, centred on trust boundaries: inventorying every boundary across hundreds of services from the real service catalogue and…
Security Decision Rights — The Decision Rights Board
An expert-level course in architecture assurance for decision rights: designing, evidencing, and assuring who may decide what about security - policy, architecture, risk acceptance, and exceptions…
Audit Finding Closure — The Closure Rail
An expert-level course in engineering audit finding closures that hold - under re-test, regulator scrutiny, resource constraints, and a systemic root cause. Work the closure rail across eight…
DLP Adversary-Aware Review — The Leakage Defense Stack
An expert-level course in reviewing your own data-loss-prevention program the way a motivated insider or intruder would look for gaps, then closing them with evidence, using written-authorised…
Security Architecture Assurance Review — The Assurance Staircase
An expert-level course that runs the review PROGRAM assuring an entire architecture portfolio - tier and intake every design, assure the pattern catalogue, apply a threat-informed review method with…
Email Authentication Assurance — The Sender Trust Stack
An expert-level architecture-assurance course proving SPF, DKIM, and DMARC at enterprise scale across a 140-domain, 30-brand, 60-third-party-sender estate — discovering the sending estate…
Security Standards Drafting — The Drafting Staircase
An expert-level course in complex scenario design for standard drafting. Climb the drafting staircase - eight steps from a raw requirement to a retired document - writing standards that are testable…
Blue Team Incident Drills — The Drill Loop
An expert-level course in control-challenge drilling: designing and running live, authorised technical drills in your own environment that test specific detection and response controls, score them…
Authorized Use of Data — The Authorized Use Board
An expert-level course that goes beyond stewardship and catalogues to govern WHO may use WHICH data for WHAT purpose, enforce that technically, and review the organisation's OWN data flows the way a…
Prompt Injection Defensibility — The Guardrail Stack
An expert-level course that builds and proves the case that an organization's own large-language-model systems cannot be made to take unauthorised actions or disclose data through prompt injection…
Telemetry Time Integrity — The Clock Rail
An expert-level course in programme optimisation for time synchronisation itself: making every timestamp in a global exchange operator's telemetry estate trustworthy, traceable, verifiable, and…
Security Monitoring Dashboard Assurance — The Signal Board
An expert-level architecture-assurance course that engineers security monitoring dashboards whose panels are provably backed by complete, timely, correct data, tuned to drive the right decisions, and…
IS Audit Reporting — The Reporting Staircase
An expert-level course in producing IS audit reports whose conclusions are defensible, whose ratings are consistent, that survive dispute, and that drive the right action at board and regulator…
Endpoint Hardening Baseline Challenge — The Hardening Funnel
An expert-level course that goes beyond applying a hardening baseline on one platform or architecting endpoint security, to proving - per setting, per fleet - that a hardening baseline is actually…
SAST Adversary-Aware Review — The Analysis Staircase
An expert-level course that reviews an organisation's own static-analysis control the way someone trying to slip a vulnerability past it would look for gaps. Climb the analysis staircase across eight…
Third-Party Contract Controls Defensibility — The Contract Rail
An expert-level course that engineers vendor contracts so their security provisions actually flow down regulatory obligations, are testable and enforceable, are monitored against real controls, are…
IoT Device Lifecycle Optimisation — The Lifecycle Loop
An expert-level course engineering the whole lifecycle of a multi-million-device IoT fleet — procurement through erasure — for security, cost, and resilience, working the eight-segment lifecycle loop…
Workload Identity Architecture Assurance — The Identity Board
An expert-level course that architects and proves strong workload identity across clouds, clusters, and CI — replacing static credentials with short-lived, attested identity bound to least-privilege…
Social Engineering Defense Training Loop — The Training Loop
An expert-level hands-on course that builds and challenges the human-risk training loop - model the risk by role, govern simulations ethically, engineer scenarios across channels, measure what…
Operational Resilience Adversary-Aware Review — The Resilience Board
An expert-level assurance course that reviews a bank's own operational-resilience claims the way a sceptical supervisor, a determined attacker or a cascading failure would probe them. Work the…
Entitlement Inventory Defensibility — The Entitlement Rail
An expert-level course on proving to auditors and regulators that the inventory of who-has-what is complete, accurate, meaningful, owned, reviewed and revoked with an evidence chain. Work the…
Cyber Risk Appetite Optimisation — The Appetite Loop
An expert-level program-optimisation course that turns a one-line cyber risk appetite into a working decision instrument: inventory the decisions appetite must change, architect and cascade…
ISMS Internal Audit Assurance — The Audit Programme Staircase
An expert-level course that designs and proves an ISO/IEC 27001 internal audit programme a certification body will accept. Climb the Audit Programme Staircase - eight steps from Programme Design…
Impact Scoring Scenario Design — The Impact Funnel
An expert-level course that engineers impact scales, scenarios, and scoring practice so cyber risk scores are calibrated, comparable, defensible, and decision-useful - diagnose why scores fail, build…
Privacy-by-Design Control Challenge — The Privacy Control Stack
An expert-level course that turns the sentence 'privacy by design applied' into controls that can fail, then challenges them in the real product. Work the privacy control stack - eight layers a…
Least-Privilege Defensibility — The Privilege Board
An expert-level course on proving, to regulators, auditors and courts, that access in an estate you own is necessary and proportionate. Work the privilege board - eight tiles that must all be…
Content Security Policy Program Optimisation — The Policy Staircase
An expert-level course that runs Content Security Policy as a portfolio-wide program rather than a per-app header. Climb the policy staircase - eight steps from a flawed baseline to measured…
Security Metric Design Assurance — The Metric Loop
An expert-level course in making security metrics defensible and decision-useful: trace each figure to the decision it must change, specify and version it, record and reconcile its lineage, validate…
eDiscovery Search Protocol Challenge — The Discovery Rail
An expert-level control challenge that designs, validates, negotiates and defends the search and review protocol for one litigation matter so it withstands a motion to compel or a regulator's…
Model Approval Governance Adversary-Aware Review — The Approval Loop
An expert-level course that reviews an organisation's own model approval path the way a supervisor, an auditor, or someone trying to slip an unvalidated model into production would - and hardens it…
Backup Scope Defensibility — The Scope Funnel
An expert-level course that proves, to a regulator and an insurer, that everything an organisation must be able to recover is in backup scope, actually captured, actually restorable, retained and…
Incident Severity Model Scenario Design — The Severity Board
An expert-level course that engineers the severity model itself - the dimensions and numbered anchors, the decision rules that work with half the facts, the regulatory clocks wired to them, a library…
Control Testing Architecture Assurance — The Testing Staircase
An expert-level course in designing the control-testing system itself so that tests are valid, populations complete, samples defensible, automation trustworthy, evidence re-performable, deviations…
Access Certification Scenario Design — The Certification Rail
An expert-level course on designing access certification campaigns that produce real decisions for the hard cases - movers, contractors, privileged, machine and toxic-combination access - with…
Intelligence Requirements Control Challenge — The Requirements Loop
An expert-level control challenge that treats intelligence requirements as the control governing everything a cyber threat intelligence function does: map stakeholders, decisions, and gaps; write…
App Permissions Defensibility — The Permission Stack
An expert-level course that turns 'the app only asks for what it needs' into something a store reviewer or regulator can check. Work the permission stack - eight layers a permission passes from…
SaaS Data Exposure Program Optimisation — The Exposure Board
An expert-level course on measuring, prioritising and reducing the exposure of your own data across SaaS tenants at scale - without breaking the business - and keeping it reduced. Work the exposure…
Detection Hypothesis Architecture Assurance — The Hypothesis Staircase
An expert-level course that treats every production detection as an explicit, testable hypothesis and assures it with evidence. Climb the hypothesis staircase - eight steps from a rule nobody can…
Backup Isolation Scenario Design — The Isolation Funnel
An expert-level course in designing backup isolation that still holds when the adversary already has admin, and proving it with authorised scenario tests. Work the isolation funnel - eight narrowing…
CSF Target Profile Control Challenge — The Profile Loop
An expert-level control-challenge course that turns an unevidenced CSF grid and an uncosted 'tier 4 everywhere' resolution into a defensible CSF 2.0 target profile: scope the profile to the mission…
Change Evidence Adversary-Aware Review — The Evidence Rail
An expert-level course on reviewing your own change-management evidence the way an auditor, a regulator or someone trying to push an unapproved change into production would - and closing every gap…
Obligation Register Defensibility — The Obligation Staircase
An expert-level course that builds and evidences an obligation register a supervisor will accept. Climb the Obligation Staircase - eight steps from Regulatory Source Inventory & Horizon through…
AI Risk Assessment Program Optimisation — The AI Risk Funnel
An expert-level course that optimises an ISO/IEC 42001 AI risk assessment programme so assessments are consistent, evidence-based, proportionate and efficient across a whole portfolio - reconcile the…
Cloud Posture Architecture Assurance — The Posture Board
An expert-level course on proving that the cloud posture-management system itself is complete, accurate and effective across an estate you own. Work the posture board - eight tiles that must all be…
Application Testing Scenario Design — The Testing Staircase
An expert-level course in designing application security test scenarios as control-verification records - requirement or abuse case, the control that must hold, the test, the expected safe result…
Business Impact Analysis Control Challenge — The BIA Funnel
An expert-level course that builds a business impact analysis whose numbers survive challenge, then challenges it - fix scope, method, and governance, write impact criteria with time-based…
Badge Control Adversary-Aware Review — The Access Control Stack
An expert-level course in reviewing your own badge and physical access control system the way an auditor, an insider or an intruder would look for gaps, then closing each gap with evidence. Work the…
API Rate Limiting Defensibility — The Throttle Stack
An expert-level course that turns 'our APIs are protected by rate limiting' into something a regulator, a customer or a third-party provider can check. Work the throttle stack - eight layers a rate…
GRC Issue Tracking Program Optimisation — The Issue Board
Engineer the issue management system itself: one definition, one record, one severity scale, owned workflow, guarded automation, evidence-based closure and one overdue number the audit committee can…
Penetration Test Finding Narrative
An expert-level course on the receiving side of a penetration test: how a security programme takes delivery of findings from an authorised test of its own environment and turns them into narrative…
PCI DSS Scope Reduction Scenarios
An expert-level course on how a security programme defensibly shrinks its own cardholder data environment and proves the reduction holds. Work down the scope funnel - eight bands through which a…
Procurement Clause Challenge
An expert-level course on how a security function gets enforceable security terms into supplier agreements and then actually holds suppliers to them. Travel the contract rail - eight stations along…
Defence in Depth Review
An expert-level course on how an architect or assurance lead establishes whether layered controls genuinely provide depth, rather than a stack of controls that all fail the same way at the same time.…
Change Risk Scoring and Defensibility
An expert-level course on how a change management function scores the security risk of a change so that the score is consistent, evidenced, and still defensible a year later in front of an auditor, a…
TLS Validation Assurance
An expert-level course on proving that TLS in an estate is actually doing what everybody assumes it is. Climb the defence stack - eight layers carrying the trust of a single connection from the…
Vulnerability Exception Scenarios
An expert-level course on the discipline of deciding, recording and governing the cases where a known vulnerability will not be remediated within the standard SLA. Work down the funnel - eight…
The Asset Inventory Challenge
An expert-level course on building an asset inventory that is true rather than tidy, and on the uncomfortable fact that almost every other security control silently depends on it. Travel the asset…
Legal Boundaries in Security Assurance
An expert-level governance course on making sure the testing and monitoring a security function performs is authorised, lawful and evidenced, so that the people doing the work are protected and the…
The Patch Testing Window Challenge
An expert-level security operations course on getting security patches into production quickly without breaking the business, and on defending the timetable when speed and stability are demanded at…
Incident Response Playbook Review
An expert-level security operations course on keeping a response library honest, so that the document somebody opens at three in the morning actually carries them to a decision. Work round the loop…
PIMS and Privacy Defensibility
An expert-level privacy governance course on turning asserted privacy controls into evidence that stands up to a regulator, an assessor or a data subject complaint. Climb the staircase - eight treads…
Firewall Policy Optimisation
An expert-level course on taking a rule base that has grown for a decade and making it small, justified, owned and evidenced without breaking the business. Work the policy funnel - eight narrowing…
Release Gate Architecture Assurance
An expert-level secure development course on designing the security gates in a delivery pipeline so that they genuinely hold, without becoming the reason teams route around the pipeline. Travel the…
Failover Testing Scenarios
An expert-level resilience course on designing failover tests that prove recovery genuinely works, rather than tests designed to pass. Work down the Failover Depth Board - eight rows, one per…
OT Safety Control Challenge
An expert-level OT and ICS security course on how a security function challenges its own controls against the constraint that dominates the plant floor: safety and continuous operation come first.…
Runtime Policy Review
An expert-level course on adversary-aware, strictly read-only review of container and Kubernetes runtime policy - testing whether your own controls would hold, never how to defeat them. Climb the…
Correlation Rule Defensibility
An expert-level course on strictly read-only review of your own SIEM's correlation rules, asking whether each one could be defended to an auditor, a regulator or a post-incident review. Ride the…
PHI Safeguard Architecture Assurance
An expert-level healthcare GRC and architecture course on proving that the administrative, physical and technical safeguards around protected health information hold in the real architecture, not…
Trust Boundary Scenarios
An expert-level threat modelling course on designing scenarios that find the trust boundary problems which matter, rather than a long generic threat list. Work down the Trust Boundary Crossing Board…
Governance Decision Rights Challenge
An expert-level governance course on testing whether security decision rights actually work - whether the people who accept risk, approve exceptions, stop releases, spend on remediation, declare…
Audit Finding Closure Review
An expert-level audit course on adversary-aware review of finding closure - assuming closure evidence may be optimistic, incomplete or prepared for the audit, and testing whether the fix genuinely…
DLP Programme Optimisation
An expert-level course on taking a data loss prevention programme that raises tens of thousands of alerts nobody reads and making it precise, owned and evidenced. Work the alert funnel - eight bands…
Assurance Review Scenarios
An expert-level security architecture course on designing the scenarios an assurance review walks a design through, so the review finds the problems that matter instead of ticking a checklist. Ride…
Email Authentication Control Challenge
An expert-level course on testing whether an organisation's SPF, DKIM and DMARC controls actually protect its domains, and driving the programme from monitoring to enforcement without breaking…
Standard Drafting Review
An expert-level governance course on adversary-aware review of security standard drafting: reading a draft standard the way a hurried engineer, a creative auditee and a literal-minded auditor will…
Incident Drill Defensibility
An expert-level blue-team operations course on designing, running and evidencing incident drills so that they genuinely improve response and let the organisation answer a regulator's question, 'prove…
Authorised Use Optimisation
An expert-level data governance course on making sure an organisation's data is used only for purposes that are authorised - and being able to prove it. Work down the Authorised Use Funnel, eight…
Prompt Injection Architecture Assurance
An expert-level architecture assurance course on making an organisation's LLM applications resilient to prompt injection - on the premise that injection cannot be reliably filtered away at the model…
Time Synchronisation Scenarios
An expert-level course on treating trustworthy time as a security control, and on designing the scenarios that prove an estate's clocks and timestamps can be relied on for detection, investigation…
Dashboard Tuning Control Challenge
An expert-level course on challenging whether an organisation's security dashboards tell the truth and drive action, panel by panel, with evidence. Climb the dashboard staircase - eight treads from a…
Adversary-Aware Review of IS Audit Reporting
An expert-level course on reviewing IS audit reports the way a motivated auditee, a sceptical audit committee member and a regulator will read them - looking for findings that can be disputed…
Hardening Baseline Defensibility
An expert-level course on making an endpoint hardening baseline something an organisation can defend to a regulator or auditor: grounded in a recognised benchmark, tailored with recorded reasons…
SAST Programme Optimisation
An expert-level course on taking a static analysis programme with a huge backlog that developers ignore and making it precise, fast, owned and trusted. Build the triage funnel - eight bands narrowing…
Architecture Assurance for Third-Party Contract Controls
An expert-level course on assuring that the security controls written into supplier contracts are actually designed into the relationship end to end - mapped to the data flows, integrations and…
IoT Lifecycle Security Scenario Design
An expert-level course on designing the controls, evidence and scenarios that prove an organisation's connected-device fleets stay secure from purchase to disposal - bought with a support commitment…
Workload Identity Control Challenge
An expert-level course on testing whether an organisation's containers, functions, pipelines and servers authenticate with identities that are unique, short-lived, least-privileged and owned - and on…
Rules of Engagement Control Challenge
Governing authorised security testing so that every engagement is authorised, scoped, constrained, deconflicted, stoppable and closed out - and proving it to the Risk Committee
Threat Intelligence Indicator Handling Scenario Design
An expert-level course on designing how an organisation handles indicators of compromise so that they improve detection instead of flooding it - requirements first, sources graded, indicators…
Vulnerability Prioritisation Programme Optimisation
An expert-level course on replacing 'fix all criticals in 30 days' with risk-based prioritisation an organisation can defend. Work down the priority funnel - eight bands from every scanner finding…
Adversary-Aware MDM Policy Review
An expert-level course on reviewing an organisation's mobile device management policy and configuration the way a hurried employee, a lost phone or a non-compliant personal device will actually meet…
Post-Incident Review Optimisation
An expert-level course on turning post-incident reviews from blame-heavy meetings with forgotten actions into a learning system that measurably reduces recurrence - triggers by severity, repeat…
Secure Delivery Programme Optimisation
An expert-level course on making the path from source code to production trustworthy and provable. Follow software along the delivery rail - eight stations from reviewed source, through pinned and…
Transaction Integrity Defensibility
An expert-level course on making the controls that protect payment and transaction integrity defensible to a supervisor and an auditor - transaction integrity defined as authorised, accurate…
Forensic Timeline Analysis Assurance
An expert-level course on designing and assuring a forensic lab's timeline-analysis capability so that its timelines are accurate, reproducible and able to withstand challenge. Build up the defence…
Pro Level · 106 courses
Enterprise Security Architecture Studio — Design, Assure, and Transform at Scale
A forty-hour Pro-level architecture studio where you lead a regulated multinational's three-year security-architecture transformation — from mandate and method through every domain to Zero Trust…
CISO Program Command — Lead, Govern, and Defend the Security Program
A thirty-hour Pro-level board simulation where you take the CISO's seat at a financial group after a damaging breach, and lead the whole security program — mandate, strategy, risk, governance…
Ransomware Crisis Command — Enterprise Resilience Under Fire
A forty-hour Pro-level crisis simulation run on a live war-room situation board, where you command a regional hospital group through a destructive ransomware event — from readiness and detonation…
Cyber Risk Management — The Risk Command
A twenty-hour, highly interactive pro-level course where you are the head of cyber risk, working the risk lifecycle on the enterprise risk heat map — identifying, assessing, evaluating against…
Security Metrics, KRIs & KPIs — Numbers the Board Can Govern By
A strategic, decision-driven pro-level course on measurement as an instrument of governance. Build and run the Atlas Group's one-page board pack — deriving metrics from decisions, engineering…
Disaster Recovery — Commanding the Worst Week
A pro-level, decision-driven course on commanding recovery while the clock runs: impact maps and funded RTO/RPO promises, strategies that survive the shared-fate hunt, declaration and command under…
Crypto Agility Command — Trust, Keys and the Post-Quantum Roadmap
A forty-hour Pro-level programme-command simulation run on a live crypto agility command board, where you lead a large financial group through a public-CA distrust, a regulator's post-quantum roadmap…
SOC Operating Model Command — Demand, People, Process, Technology, Sourcing and the Investment Case
A forty-hour Pro-level operations-command simulation run on a live SOC operations command board, where you lead a multinational's security operations through a missed incident the regulator is asking…
AI Logging Governance Command
Run the live governance board for a multi-region insurer's AI estate — traceability, residency, retention, sensitive data, access and integrity, pipeline reliability and regulator readiness — and…
GRC Transformation and Continuous Monitoring
A forty-hour Pro-level transformation-command simulation run on a live GRC transformation command board, where you lead a multinational insurer's GRC function through an assurance report qualified on…
Multi-Region PCI DSS Program Strategy
A forty-hour Pro-level command simulation run on a live PCI multi-region command board. You lead a global hotel and retail group's payment security through a failed EU ROC and an acquirer's fees…
Security Foundations Investment Case
A forty-hour Pro-level investment-command simulation run on a live security investment command board, where you are the newly appointed CISO of a UK manufacturer whose board has never funded security…
Emergency Change Control Governance
A forty-hour Pro-level control-command simulation run on a live emergency change command board, where you are Head of Service Governance at a UK retail bank whose emergency route has become the…
Vulnerability Coverage Governance
A forty-hour Pro-level coverage-command simulation run on a live vulnerability coverage command board, where you are Group Head of Vulnerability Management at a multinational energy-infrastructure…
Asset Ownership Crisis Response
A forty-hour Pro-level ownership-crisis simulation run on a live asset ownership crisis command board, where you are Head of IT Asset Governance at a regulated water utility after a major incident…
Security Culture Metrics That Matter
A forty-hour Pro-level security-culture measurement simulation run on a live security culture command board, where you are Head of Security Culture at a banking and insurance group whose awareness…
Consent Management Decision Scenarios
A forty-hour Pro-level consent and data-ethics decisioning simulation run on a live consent decisioning command board, where you are Chief Privacy Officer and Data Ethics Lead at a consumer…
Patch Evidence Crisis Leadership
A forty-hour Pro-level emergency patch assurance simulation run on a live patch evidence crisis command board, where you are Head of Infrastructure Operations at a hospital group when an actively…
Data Processor Contract Obligations
A forty-hour Pro-level processor-assurance simulation run on a live processor obligations command board, where you are Head of Privacy Assurance at a B2B SaaS provider acting as processor for 1,200…
NAC Enforcement Transformation Program
A forty-hour Pro-level network access control transformation simulation run on a live NAC transformation command board, where you are Head of Network Security at a global manufacturer with 240 sites…
Security Backlog Prioritization Decisions
Turn an ungoverned security backlog into a Board-level capacity decision — priced, ranked, funded and governed — on a live decision board, from the incident that exposed it to the resolution that…
Kubernetes Secrets Management Investment Case
A forty-hour Pro-level secrets-handling investment simulation run on a live secrets investment command board, where you are Head of Platform Security at a payments company running 40 Kubernetes…
SIEM Cost and Retention Strategy
A forty-hour Pro-level log retention simulation run on a live SIEM retention command board, where you are Head of Security Engineering at a UK bank; an investigation needs fourteen months of…
PHI Minimum Necessary Access Governance
A forty-hour Pro-level health-system privacy governance simulation run on a live minimum necessary command board, where you are Chief Privacy and Information Security Officer of a US regional health…
Abuse Case Threat Modeling at Scale
A forty-hour Pro-level design-governance simulation run on a live abuse case governance command board, where you are Head of Security Architecture at a fintech serving 9.6 million customers in four…
Internal Audit Universe and Coverage Planning
A forty-hour Pro-level internal audit strategy simulation run on a live audit universe investment board, where you are Chief Audit Executive of a UK insurer whose broker platform is breached after…
Encryption at Rest Program Strategy
A forty-hour Pro-level encryption-at-rest transformation simulation run on a live encryption at rest command board, where you are Head of Data Protection Engineering at a health and life insurer; an…
DKIM Signing Key Compromise Response
A forty-hour Pro-level email-authentication crisis simulation run on a live DKIM crisis command board, where you are Head of Messaging Security at a UK bank with 6.8 million customers; a former…
Security Exception Governance
A forty-hour Pro-level policy-exception governance simulation run on a live exception governance investment board, where you are Head of Security Policy and Standards at a retail, commercial and…
Control Effectiveness Improvement Program
A forty-hour Pro-level control-improvement simulation run on a live control improvement command board, where you are Head of Defensive Operations at a regulated water utility; three incidents in a…
Data Ownership and Stewardship Transformation
A forty-hour Pro-level data governance transformation simulation run on a live data ownership transformation board, where you are Chief Data Officer of a bank whose regulator could not trace 13 of 48…
LLM Tool Use Governance
Govern what AI agents can do — tools, credentials, approvals, policy, trust boundaries, monitoring, assurance and incident response — and defend it to a Board.
Evidence-Grade Log Integrity Governance
A forty-hour Pro-level log integrity governance simulation run on a live log integrity governance board, where you are Head of Security Telemetry at a multinational bank; opposing counsel's expert…
Alert Fatigue and Monitoring Noise Reduction
A forty-hour Pro-level security monitoring crisis simulation run on a live monitoring noise crisis board, where you are Head of Security Monitoring at an insurer whose SOC receives 71,000 alerts a…
Audit Criteria and Framework Mapping
A forty-hour Pro-level IS audit methodology simulation run on a live audit criteria investment board, where you are Head of IT Audit at a composite insurer; management successfully disputes three…
EDR Alert Triage Operations
A forty-hour Pro-level endpoint detection and response triage simulation run on a live EDR triage command board, where you are Head of Endpoint Defence at a retailer with 640 stores and 54,530…
DAST Pipeline Transformation
A forty-hour Pro-level application-security transformation simulation run on a live DAST transformation command board, where you are Head of Application Security at an online retail and…
Third-Party Risk Monitoring Decisions
A forty-hour Pro-level third-party risk simulation run on a live monitoring decision board, where you are Head of Third-Party Risk at a retail bank that read about its payroll provider's breach in…
IoT Device Identity and PKI Governance
A forty-hour Pro-level device identity governance simulation run on a live IoT device identity governance board, where you are Head of Device Security at an energy-services and e-mobility company…
Policy-as-Code Guardrail Governance
A forty-hour Pro-level policy-as-code crisis simulation run on a live crisis board, where you are Head of Cloud Platform Security at a UK omnichannel retailer; a provenance rule published straight to…
SOAR Enrichment and Automation Investment Case
A forty-hour Pro-level SOC automation investment simulation run on a live SOAR enrichment investment board, where you are Head of SOC Engineering at a UK insurer; an identity alert on the…
Social Engineering Incident Response
A forty-hour Pro-level social-engineering defence simulation run on a live social engineering response board, where you are Head of Fraud and Social Engineering Defence at a UK bank with 14,200…
Transaction Integrity Control Transformation
Lead a bank from a duplicated weekend to a Board-approved blueprint that proves every payment moves exactly once, complete and unaltered.
Access Review Certification Decisions
Turn a certification campaign that approves everything into review decisions an auditor can test, a Board can fund and an organisation can sustain
ISMS Management Review Recovery
A forty-hour Pro-level ISMS governance crisis simulation run on a live management review crisis board, where you are Head of Information Security Governance at a certified SaaS provider whose…
Asset Context and Criticality Mapping
A forty-hour Pro-level risk-assessment governance simulation run on a live asset context investment board, where you are Head of Technology Risk at a UK bank whose Low-rated file-transfer server has…
DPIA and Privacy-by-Design Assurance
A forty-hour Pro-level data protection impact assessment simulation run on a live DPIA command board, where you are Head of Privacy Engineering at a digital-health provider whose launch-gate review…
Forensic Timeline Readiness Program
A forty-hour Pro-level digital forensics capability simulation run on a live forensic timeline transformation board, where you are Head of Digital Forensics and Incident Investigation at a logistics…
Zero Trust Continuous Verification Decisions
A forty-hour Pro-level zero trust architecture governance simulation run on a live continuous verification decision board, where you are Chief Security Architect at a regional bank eighteen months…
Enterprise Browser Security Governance
A forty-hour Pro-level multi-region browser and web-platform governance simulation run on a live browser security governance board, where you are Global Head of Endpoint and Web Platform Security at…
Defensible Data Deletion and Legal Holds
A forty-hour Pro-level records-governance simulation run on a live defensible deletion command board, where you are Head of Records and Information Governance at a UK and EU financial-services group…
AI Model Inventory and Model Risk Governance
A forty-hour Pro-level model-risk governance simulation run on a live model inventory transformation board, where you are Head of Model Risk Management at a UK bank with a US subsidiary whose…
Immutable Backup Strategy Decisions
A forty-hour Pro-level backup resilience governance simulation run on a live backup immutability decision board, where you are Head of Technology Resilience at a building society with 1.12 million…
Multi-Region Incident Containment Governance
Stop a multi-region incident spreading — without stopping the business.
Audit Remediation Delivery and Evidence
Drive audit remediation to done — on time, with evidence.
Joiner-Mover-Leaver Identity Lifecycle
Make the case for an identity lifecycle that removes leavers in hours, not weeks.
Actionable Threat Intelligence Decisions
Turn threat indicators into decisions — not alert floods.
Software and Hardware Supply Chain Integrity
Prove nothing in your software and hardware supply chain was tampered with.
Lost Device Incident Decisions
Decide fast and defensibly when a device holding company data goes missing.
SaaS Discovery and Governance at Scale
Find, govern and secure every SaaS app your people signed up for — in every region.
Detection Rule Validation and Coverage
Prove your detections fire — before the next incident proves they don't.
NIST CSF Maturity Measurement for Boards
Show the board real control maturity — measured, not self-scored.
Secure Baseline Reset at Enterprise Scale
Rebuild secure configuration baselines across a whole enterprise — and keep them.
Unified Control Framework Mapping
Map one set of controls to every rulebook — and let the board decide on facts.
ISO 42001 AI Management System Rollout
Govern every AI model across every region under one ISO/IEC 42001 system.
Cloud Security Incident Leadership
Lead a cloud security incident from first alert to a board-ready account.
AppSec Investment Case for OWASP Risks
Make the investment case that turns OWASP risks into fewer, cheaper flaws.
Business Continuity Strategy and Impact Tolerances
Defend a continuity strategy that keeps critical services running through any disruption.
Visitor Access Control Transformation
Transform how a whole estate knows who is inside — and why.
API Input Validation Strategy
Decide how strictly every API must validate what it accepts — and fund it.
GRC Workflow Automation Across Regions
Design GRC workflows that run themselves across every region — with humans where it counts.
PCI DSS Scope Reduction Investment Case
Make the investment case that shrinks PCI scope, cost and risk at once.
Confidentiality, Integrity and Availability in Practice
Transform how a whole organisation lives confidentiality, integrity and availability.
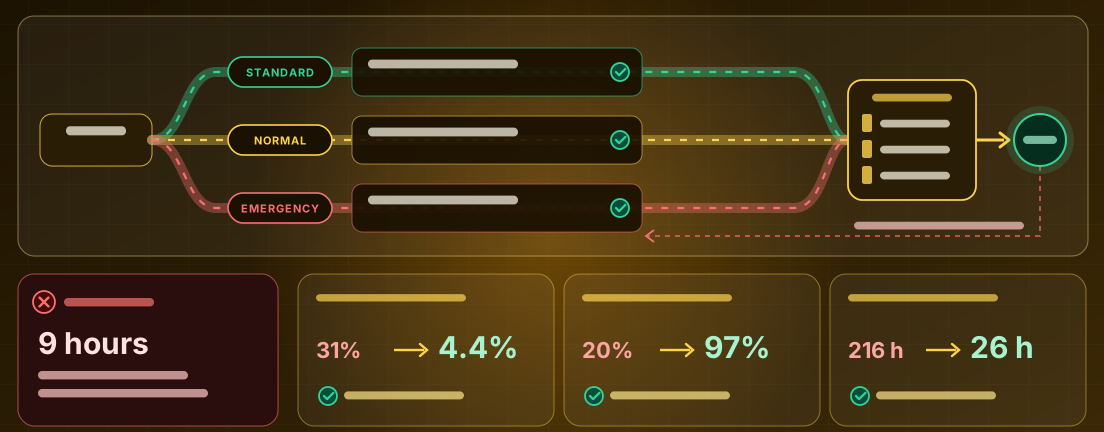
Emergency Change at Pipeline Speed
Decide how emergency changes move fast without breaking control.
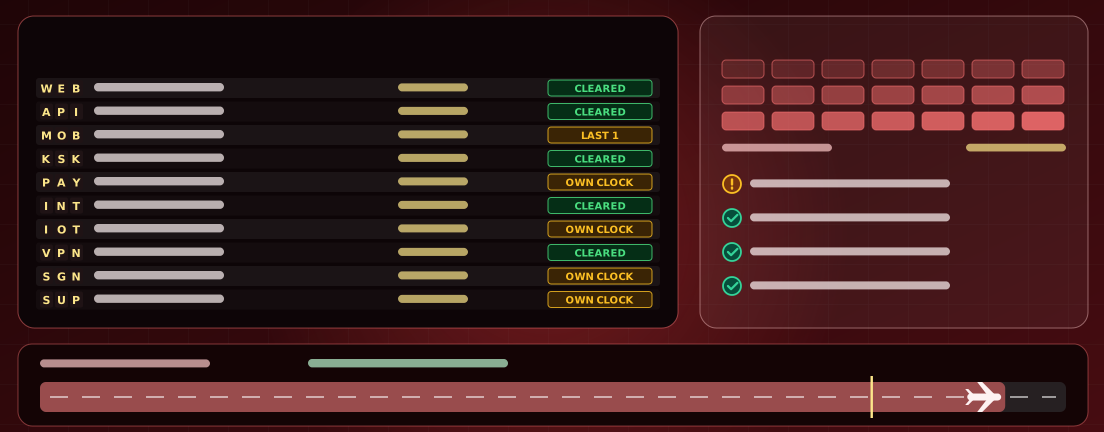
Certificate Authority Distrust Crisis Response
Lead the crisis when thousands of certificates must be replaced — now.
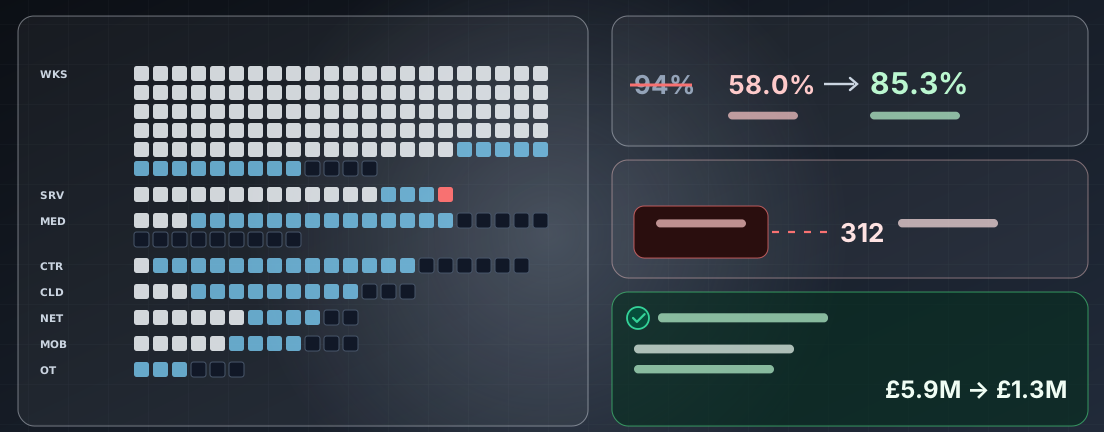
Vulnerability Scan Coverage Investment Case
Make the investment case that finally scans every asset you own.
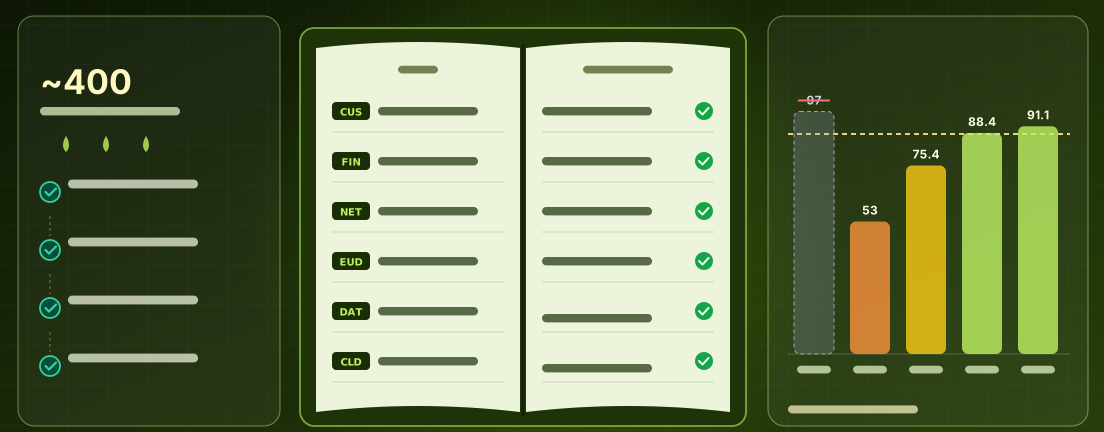
Sustainable IT Asset Ownership Model
Defend an asset-ownership model where every system has a name next to it.
Evidence-Based Security Culture Investment
Help the board choose which security-culture programme to fund — on evidence.
Regulator Consent Investigation Response
Lead the organisation through a regulator's investigation into how it collected consent.
AI System Logging Investment Case
Make the investment case for logging every AI system you run.
Verified Patching Evidence Model
Defend a patching model that proves every fix landed — with evidence.
SOC Transformation Delivery
Run the transformation that rebuilds a SOC's operating model — and keeps the lights on.
ISO 27701 Certification Strategy for Processors
Help the board decide how the organisation meets its duties as a data processor.
Global Network Access Control Governance
Govern network access control across every region and every site.
Security Debt Launch Crisis Leadership
Lead the crisis when the security backlog stops a product launch.
Disaster Recovery Time Investment Case
Make the investment case that cuts recovery time where it matters most.
Kubernetes Secrets Vaulting Transformation
Transform how every cluster handles secrets — from hard-coded to vaulted.
Log Retention Value and Cost Decisions
Help the board decide how long security logs are kept — and what that buys.
Insider Risk Program Leadership
Run an insider-risk programme that is effective, fair and lawful.
Cyber Crisis Communications Playbook
Lead cyber crisis communications — to staff, customers, media and regulators.
Cyber Insurance and Claims Readiness
Buy the right cyber cover, prove your controls, and make a claim that pays.
Deepfake and CEO Fraud Defense
Stop deepfake and executive-impersonation fraud before the money moves.
Cryptographic Inventory and Quantum Readiness
Inventory every use of cryptography and plan the move to post-quantum.
Board-Level Cyber Risk Reporting
Report cyber risk to the board in a way that drives decisions.
Security Budget Prioritization Strategy
Build, prioritise and defend a security budget that buys down real risk.
Cyber Due Diligence for Mergers and Acquisitions
Assess cyber risk in an acquisition — and integrate the target safely.
Third-Party Breach Response Scenarios
Respond when a critical supplier is breached and your data is in their hands.
Data Leak Prevention Without Friction
Build a data-loss-prevention programme that stops leaks without stopping work.
Security Architecture Review at Scale
Run security architecture reviews at scale — fast, consistent and useful.
Security Champions Network Program
Build a security-champions network that changes how teams work.
Identity Threat Detection and Response
Detect and stop account takeover across your whole identity estate.
Brand Impersonation and Phishing Takedown
Take down phishing sites, fake apps and impersonators before customers are hurt.
72-Hour Breach Notification Decisions
Decide, notify and document a personal-data breach — on time, everywhere.
Hybrid and Remote Work Security
Secure hybrid and remote work without making people's jobs harder.
Cyber Exercise Program Design
Run cyber exercises that make the organisation measurably better at responding.
Certified Information Systems Auditor (CISA)
Master all five CISA domains inside one real IS audit — then drill 996 practice questions by domain, section and topic and sit a 150-question, four-hour mock exam.