App Permissions Defensibility — The Permission Stack
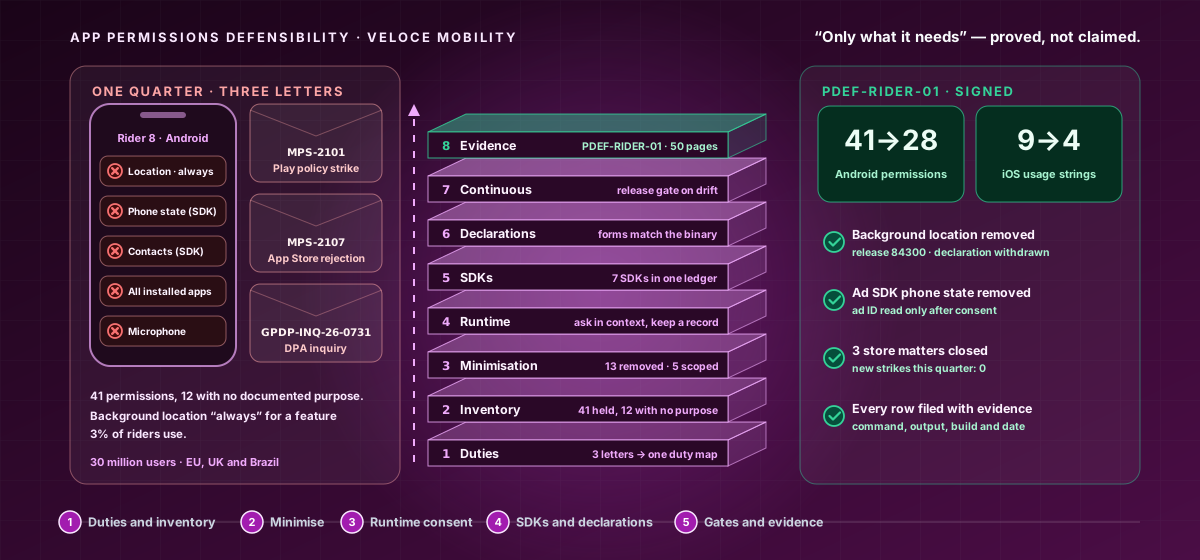
An expert-level course that turns 'the app only asks for what it needs' into something a store reviewer or regulator can check. Work the permission stack - eight layers a permission passes from manifest line to evidence: Regulatory & Store Duties on Permissions; Permission Inventory & Justification; Minimisation: Alternatives, Scoping & Degradation; Runtime Requests, Consent & Transparency; SDK & Library Permission Inheritance; Store Declarations vs Actual Behaviour; Continuous Checks: CI, Drift & Release Gates; and Evidence Packs & Regulator or Store Dialogue - as Thabo, mobile platform security lead at Veloce Mobility, a ride-hailing and delivery super-app facing a Play policy strike, an App Store rejection and a data protection authority inquiry in one quarter. Strictly defensive: Veloce's own apps, builds and test devices only, and every chapter's lab builds one component of the Rider Permissions Defensibility File.
What you'll learn
- Map each permission to its GDPR, ePrivacy, LGPD, Play and App Review duties, and inventory and justify every declared, requested and used permission from the shipped binary.
- Minimise permissions with pickers, intents, approximate and while-in-use scoping, platform flags and graceful degradation, and design in-context, honest requests backed by consent records.
- Control SDK permission inheritance with merger rules, behavioural audits, privacy manifests and contracts, and reconcile Data safety, privacy labels and declarations with observed behaviour.
- Hold the line with CI baselines, budgets, approval workflows, drift checks and device-farm gates, and answer stores and regulators from a verified, per-permission evidence file.
Sign in to enrol — you can pay by bKash or Nagad, or apply a promo code.