← Back to catalogue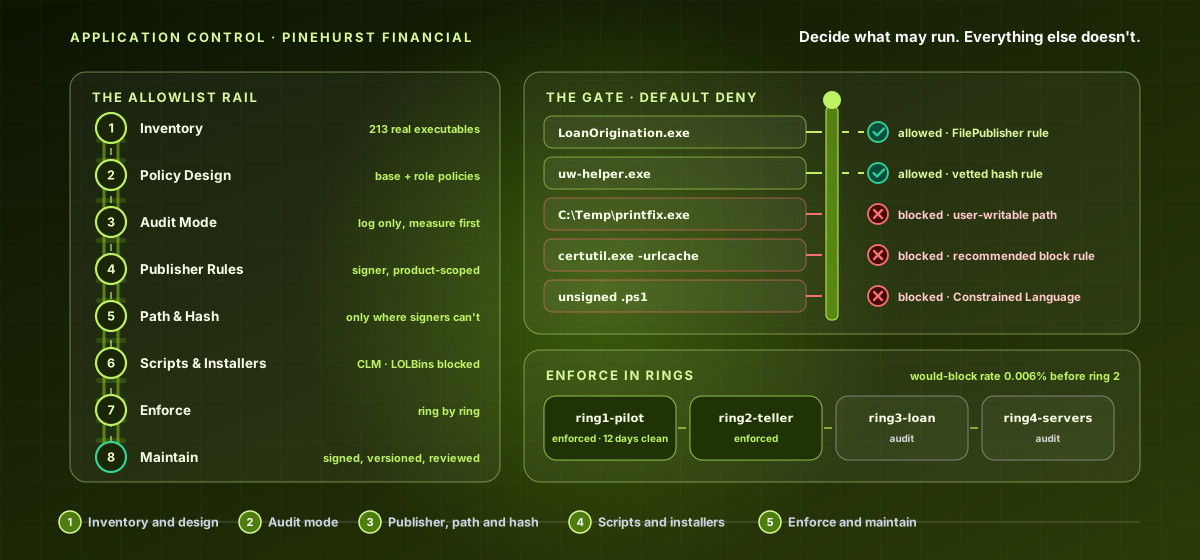
CY-MID-109Mid Level · Application Control
Application Control & Allowlisting — The Allowlist Rail
A hands-on mid-level course that controls what is allowed to run on a fleet you own. Work the allowlist rail across eight stations - Inventory, Policy Design, Audit Mode, Publisher Rules, Path & Hash Rules, Scripts & Installers, Enforce, and Maintain - building default-deny WDAC/AppLocker, Santa, and fapolicyd policies with real PowerShell, event-log, and console commands, from audit-mode discovery through ringed enforcement and ongoing maintenance. Four hands-on activities in every lesson.
15 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Build a real software inventory from execution telemetry across the fleet.
- Design a default-deny policy scoped by device role with a base and supplemental structure.
- Deploy and read audit mode to build the allowlist from real usage before enforcing.
- Enforce in rings with an exception workflow, rollback, and ongoing maintenance.
Price:৳8,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.