← Back to catalogue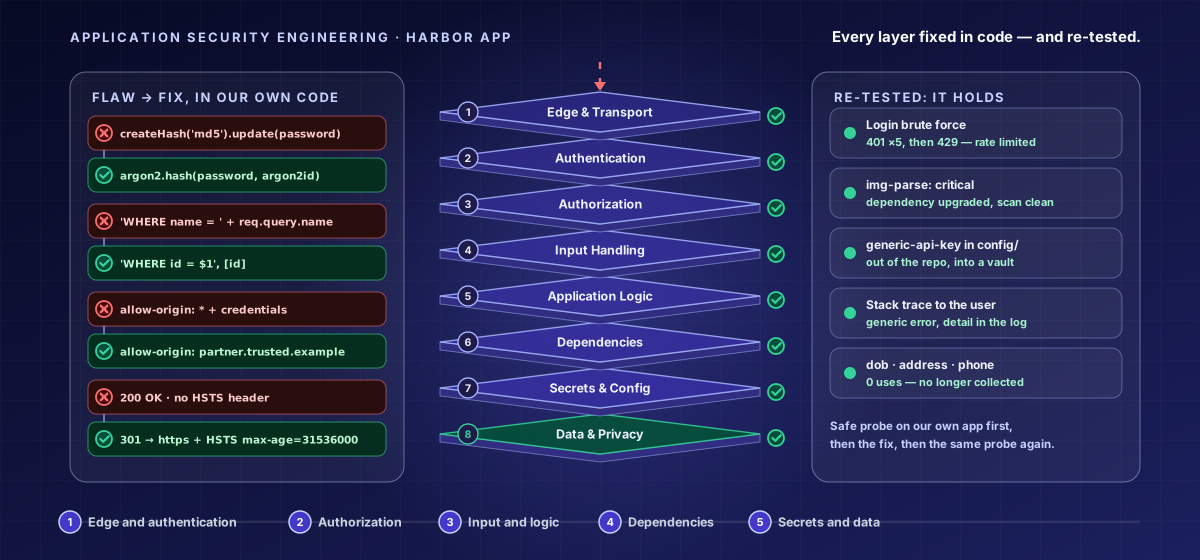
CY-MID-071Mid Level · Application Security
Application Security Engineering — The Defense Stack
A hands-on mid-level course that secures a web application layer by layer, as the engineer who builds and fixes it. Work the defense stack — Edge & Transport, Authentication, Authorization, Input Handling, Application Logic, Dependencies, Secrets & Config, and Data & Privacy — finding each vulnerability class with a safe probe against your own app and closing it in the server-side code, verified with a test. Strictly defensive, always paired with the fix. Four hands-on activities in every lesson.
15 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Harden the edge with enforced TLS, security headers, and safe CORS.
- Build robust authentication and enforce authorization server-side on every object and action.
- Close injection and XSS with parameterization, context-aware encoding, and allowlist validation.
- Secure the supply chain, manage secrets and config, and protect application data.
Price:৳8,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.