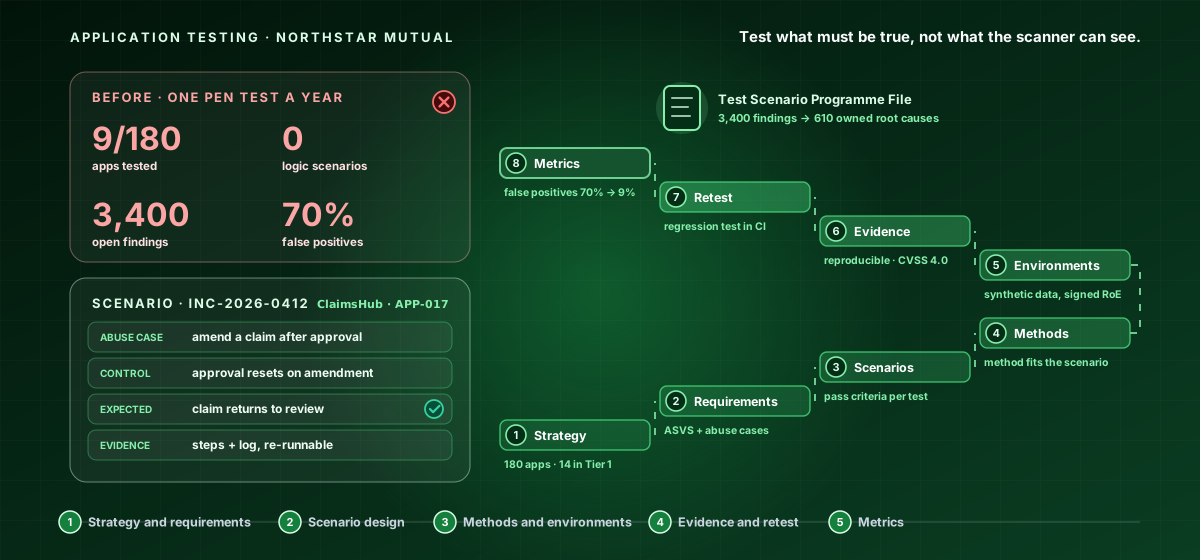
Application Testing Scenario Design — The Testing Staircase
An expert-level course in designing application security test scenarios as control-verification records - requirement or abuse case, the control that must hold, the test, the expected safe result, the pass criterion and the evidence. Climb the testing staircase - eight steps from an annual pen test treated as the whole programme to measured assurance: risk-based strategy and tiering; ASVS requirements and abuse-case catalogues; scenario design for technical controls, business logic and authorisation; method selection across SAST, DAST, IAST, SCA and manual review; owned environments, synthetic data and signed rules of engagement; reproducible, evidenced and properly rated findings; triage, retest and regression protection in CI; and coverage metrics, regulator evidence and optimisation - across 180 applications at Northstar Mutual, building one capstone Programme File component per chapter. Strictly defensive, on the organisation's own applications. Four hands-on activities in every lesson.
What you'll learn
- Build a risk-based test strategy that tiers applications, sets depth, cadence and change triggers, and maps DORA, the state model law, NIST SSDF, SA-11 and PCI DSS 4.0 to evidence.
- Derive testable requirements from ASVS and write abuse and misuse cases with process owners, checked against the OWASP Top 10 and API Top 10.
- Design control-verification scenarios - including state-transition, authorisation-matrix, boundary and chained scenarios - with expected safe results, pass criteria and evidence.
- Assign each scenario the method that can observe its control, with requirement-mapped SAST and SCA, authenticated coverage-gated DAST and IAST, and a scenario-based external test.
Sign in to enrol — you can pay by bKash or Nagad, or apply a promo code.