← Back to catalogue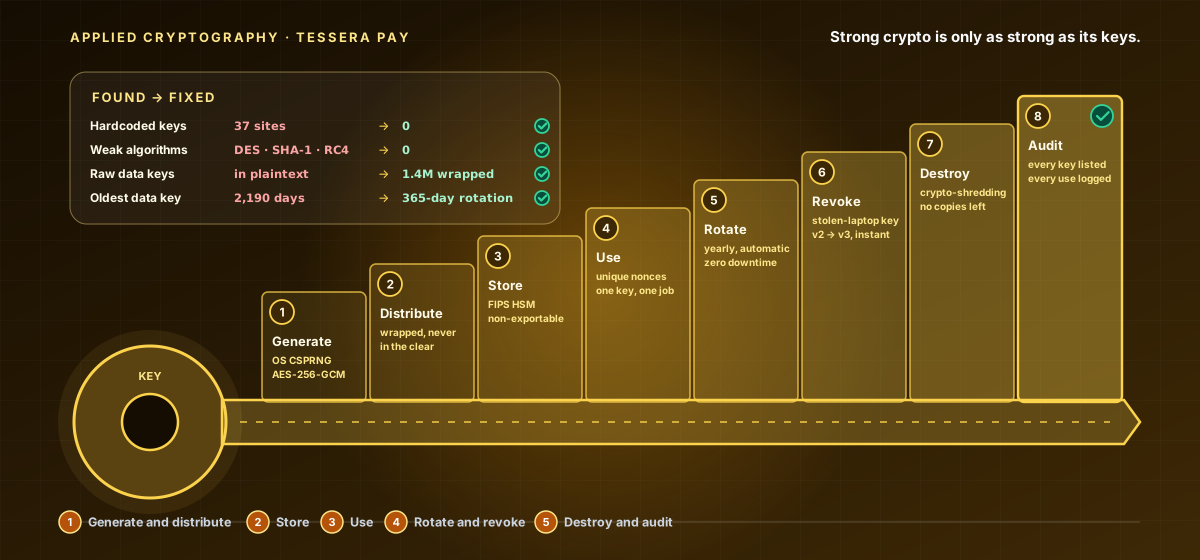
CY-MID-008Mid Level · Applied Cryptography & Key Management
Applied Cryptography & Key Management — The Key Lifecycle
A hands-on mid-level course that uses cryptography correctly and manages keys through their whole life. Work the key lifecycle - eight stages a key climbs from birth to retirement: Generate, Distribute, Store, Use, Rotate, Revoke, Destroy, and Audit - using vetted primitives, keeping keys secret and managed, and never reusing a key or a nonce, with real OpenSSL, KMS/HSM, envelope-encryption, authenticated-encryption, rotation, and crypto-inventory work. Four hands-on activities in every lesson.
15 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Generate keys from a CSPRNG with current algorithms, separated by purpose.
- Distribute and store keys without exposure, using wrapping, envelope encryption, and an HSM/KMS.
- Use keys correctly: authenticated encryption, unique nonces, one purpose per key, vetted libraries.
- Rotate, revoke, crypto-shred, and prove the lifecycle against FIPS/PCI/NIST.
Price:৳8,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.