Change Risk Scoring and Defensibility
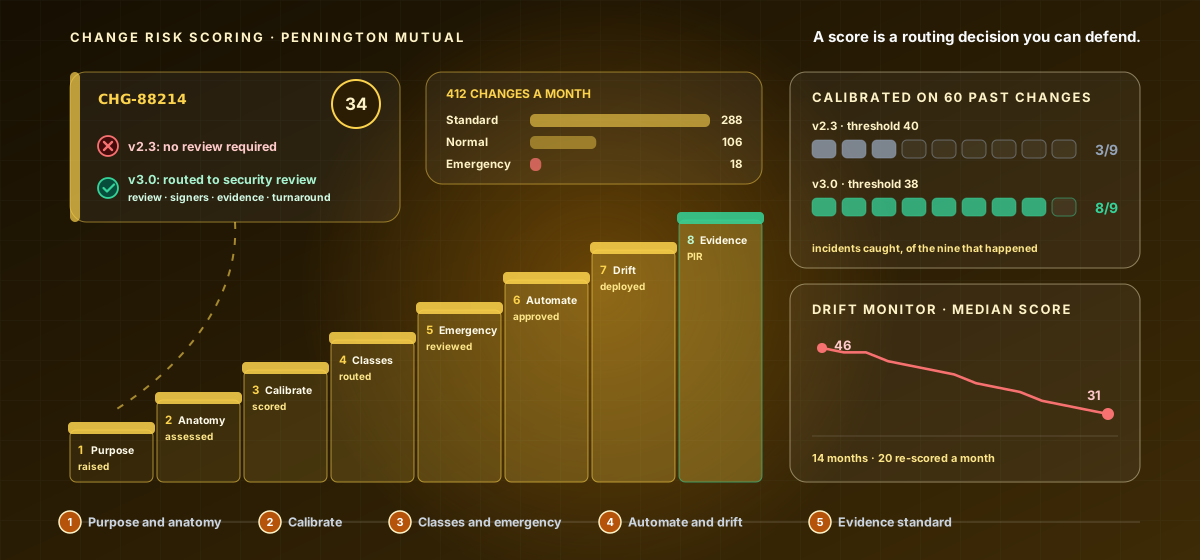
An expert-level course on how a change management function scores the security risk of a change so that the score is consistent, evidenced, and still defensible a year later in front of an auditor, a regulator or a post-incident review. Climb the staircase - eight treads carrying a change from raised to post-implementation review: establishing what a score is actually for; building factors, weights and thresholds that survive challenge; calibrating against changes that already happened; defining the standard, normal and emergency classes; scoring the emergency after the fact; deciding where automated scoring is defensible; detecting and correcting score drift; and writing an approval record somebody can reconstruct a year later.
What you'll learn
- Explain what a change risk score is for, and bind every band of a scale to the review, signatories, evidence and turnaround it obliges.
- Select scoring factors observable from the change record before deployment, derive weights from outcome frequency, external obligation or a recorded decision, and place thresholds with their boundary rules written in advance.
- Calibrate a model against the organisation's own history including every incident-causing change, using blinded retrospective scoring, and set thresholds from hit rate against review burden as a recorded appetite decision.
- Define standard, normal and emergency change classes by the decision each removes, give every standard-change catalogue entry a security position and an expiry, and place security review inside the flow as a blocking transition.
Sign in to enrol — you can pay by bKash or Nagad, or apply a promo code.