← Back to catalogue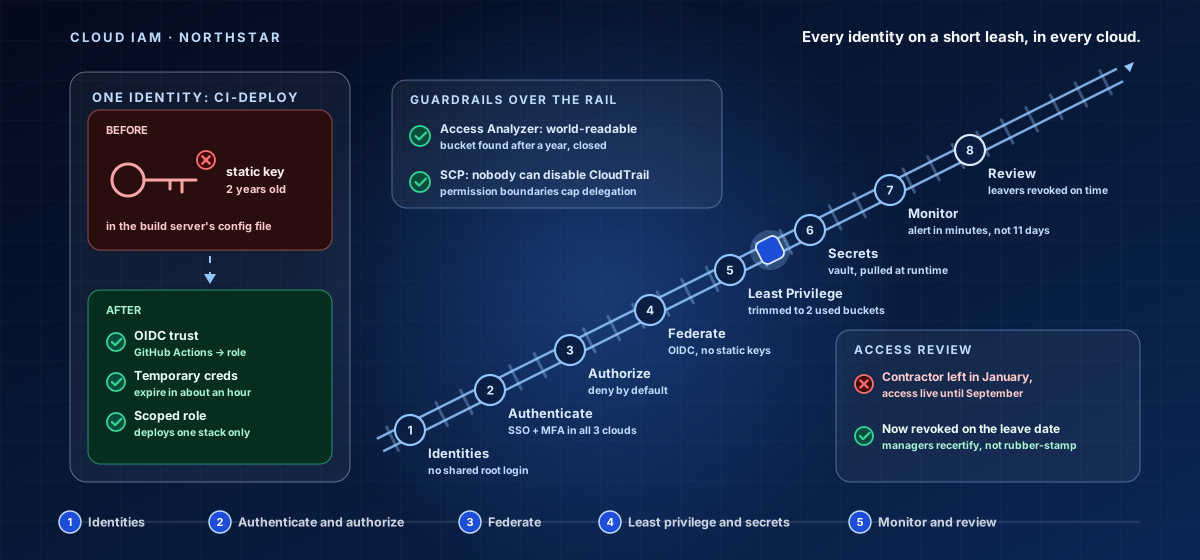
CY-MID-054Mid Level · Cloud IAM
Cloud IAM — The Cloud Access Rail
A hands-on mid-level course that gets cloud identity and access right across AWS, Azure, and GCP. Work the cloud access rail - eight stations: Identities, Authenticate, Authorize, Federate, Least Privilege, Secrets, Monitor, and Review - eliminating long-lived keys, right-sizing policies, and catching privilege drift. Strictly defensive. Four hands-on activities in every lesson.
15 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Model cloud identities and authenticate without long-lived keys.
- Write least-privilege policies and federate access safely.
- Manage cloud secrets and monitor for risky permissions.
- Review access and remediate privilege drift continuously.
Price:৳8,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.