← Back to catalogue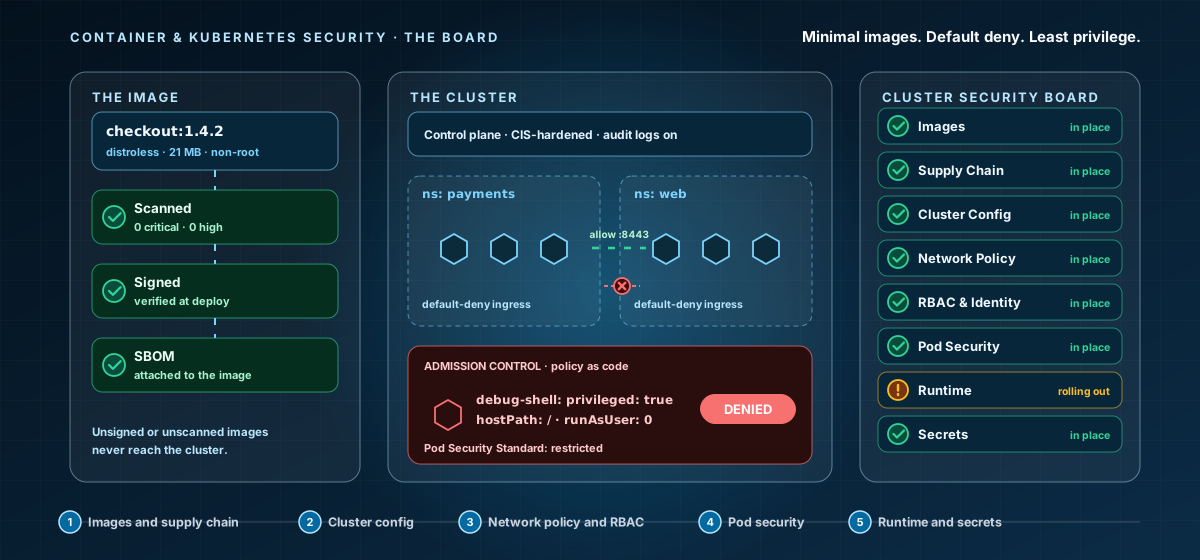
CY-MID-024Mid Level · Container Security
Container & Kubernetes Security — The Cluster Security Board
A hands-on mid-level course that hardens containers and the Kubernetes clusters that run them. Work the cluster security board - eight domains: Images, Supply Chain, Cluster Config, Network Policy, RBAC & Identity, Pod Security, Runtime, and Secrets - building minimal signed images, default-deny network policy, least-privilege RBAC, and policy-as-code admission control. Grounded in the CIS Kubernetes Benchmark and Pod Security Standards; defensive throughout. Four hands-on activities in every lesson.
15 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Build minimal, scanned, and signed images with a verifiable supply chain.
- Harden cluster configuration to the CIS Benchmark and Pod Security Standards.
- Enforce default-deny network policy and least-privilege RBAC.
- Add runtime protection and policy-as-code admission control for secrets and pods.
Price:৳8,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.