← Back to catalogue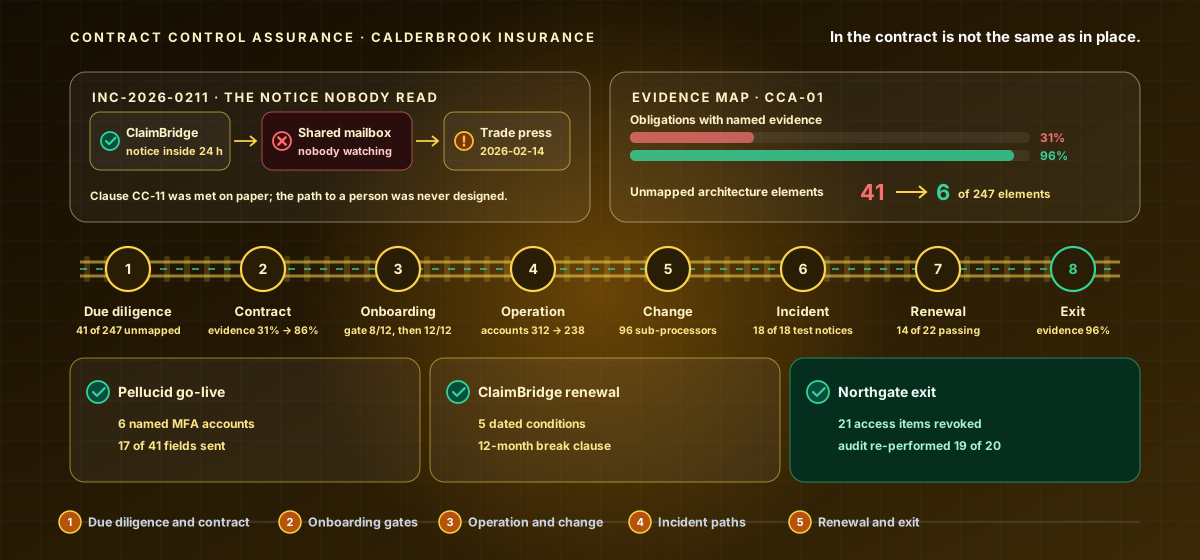
CY-EXPERT-103Expert Level · Third-Party Risk
Architecture Assurance for Third-Party Contract Controls
An expert-level course on assuring that the security controls written into supplier contracts are actually designed into the relationship end to end - mapped to the data flows, integrations and access paths of the real service, proved by named evidence, gated before go-live, operated and monitored, re-mapped when the supplier changes, tested against the real escalation path, weighed on evidence at renewal and proved at exit. Follow one supplier relationship along the Supplier Control Assurance Rail, eight stations from due diligence to exit, and build a single Contract Control Assurance Architecture and Supplier Evidence Map as you go.
18 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Reconstruct a supplier incident as a contract-control design failure, inventory each service's data flows, integrations and access paths from evidence, map controls to them and tier suppliers by exposure.
- Build a control-to-evidence map naming artefact, producer, frequency, reader and pass criterion for every obligation, route notices to watched roles, and specify evidence obligations for the legal team.
- Gate go-live on binary evidenced criteria, provision supplier access through the organisation's own identity platform, review and verify integrations, and minimise the data sent.
- Recertify and monitor supplier access, read assurance reports for scope, period, carve-outs and exceptions, bridge their gaps, own complementary user entity controls and run evidence to a calendar.
Price:৳12,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.