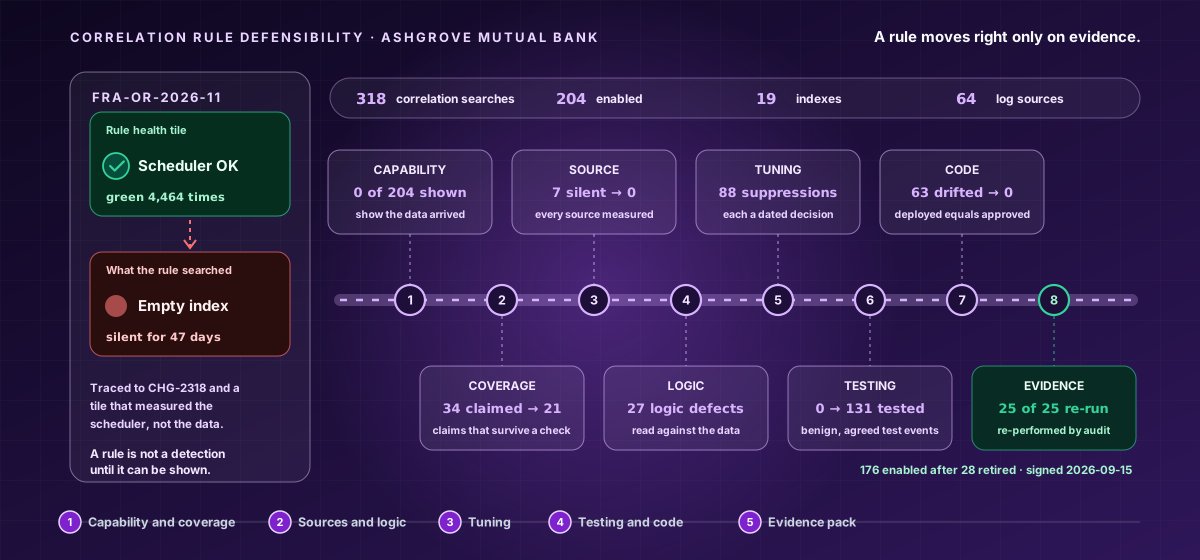
Correlation Rule Defensibility
An expert-level course on strictly read-only review of your own SIEM's correlation rules, asking whether each one could be defended to an auditor, a regulator or a post-incident review. Ride the detection rail - eight stations from a rule that was enabled but blind to an evidence pack an assessor can re-perform: what separates a rule from a detection capability; mapping rules to the risks and obligations they claim; the log sources every rule silently depends on; thresholds, windows, joins and lookups read against the data; every suppression a recorded decision; benign test events and a regression suite; version control, peer review, change records and ownership; and alert disposition data and a signed evidence pack with a figure date and a successor cycle.
What you'll learn
- Separate an enabled rule from a detection capability, trace a failed demonstration to the dependency that broke, prove the review role read-only under written authorisation, and fix a dated inventory as the denominator.
- Test every claim that a rule covers a risk or obligation against the behaviour, the source and the logic, and replace a coverage percentage with a coverage statement that survives checking.
- Measure last event seen for every source a rule consumes, map rules to sources through data models and lookups, and make a silent or partial source a detection in its own right.
- Read thresholds, time windows, joins and lookups against the data, and find the rules that are logically tidy and structurally unable to fire.
Sign in to enrol — you can pay by bKash or Nagad, or apply a promo code.