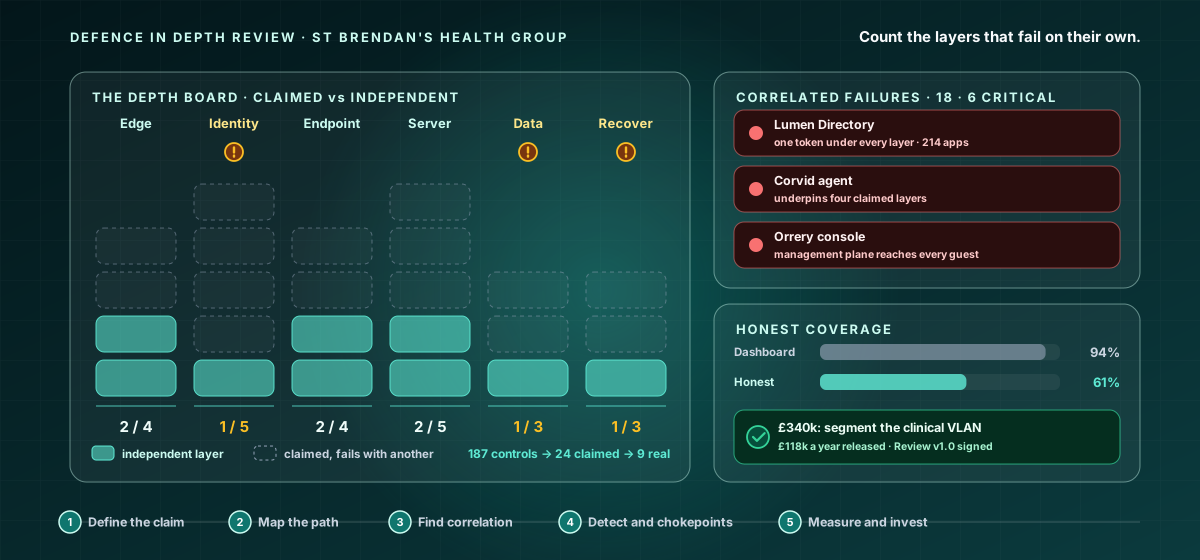
Defence in Depth Review
An expert-level course on how an architect or assurance lead establishes whether layered controls genuinely provide depth, rather than a stack of controls that all fail the same way at the same time. Work the depth board - eight review bands against six segments of the path an incident would have to cross: defining what a layer has to be before it counts; mapping the segments and the controls on each; finding the layers that fail together; testing whether a compensating control genuinely compensates; separating prevention depth from detection depth; registering the single points that layering hides; measuring coverage you could defend to an auditor; and deciding where to add a layer and where to remove one that costs more than it gives.
What you'll learn
- Define what a control has to be before it may be counted as a layer, and restate a control inventory as a depth claim an architecture board can challenge on evidence.
- Model the path an incident would traverse as segments a defender can place controls on, map every control to the segment its effect lands on, and count depth from realistic entry points rather than from outside the estate.
- Find the controls that fail together through a shared identity provider, agent, console, supplier, update channel or unexamined assumption, and record each as a treatable register entry with a named owner.
- Test compensating controls against outcome, independence, evidence and expiry, and stop accepted compensations from becoming permanent layers nobody decided on.
Sign in to enrol — you can pay by bKash or Nagad, or apply a promo code.