← Back to catalogue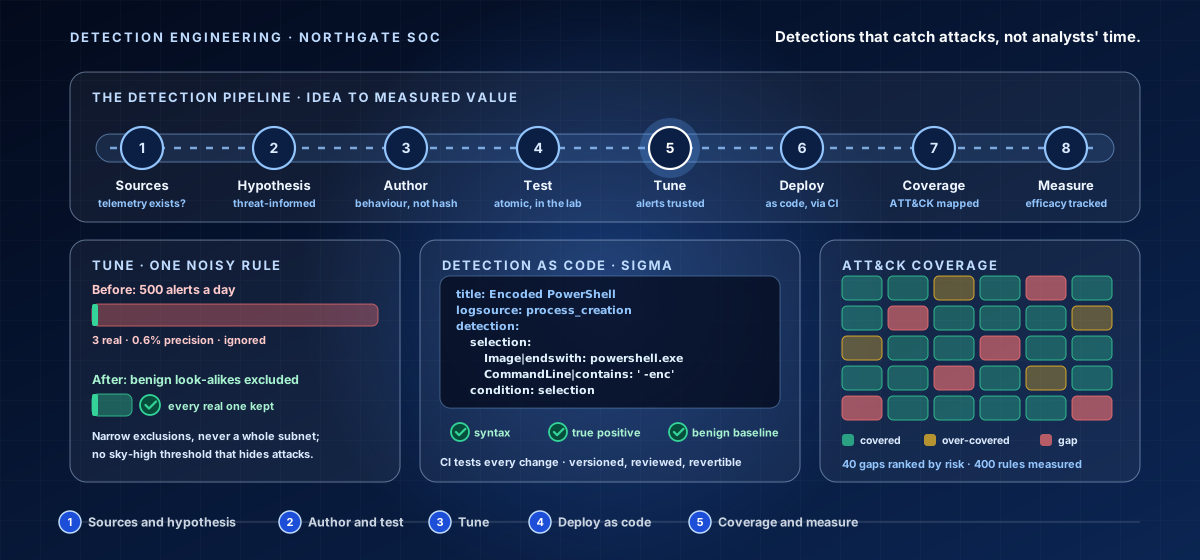
CY-MID-018Mid Level · Detection Engineering
Detection Engineering — The Detection Pipeline
A hands-on mid-level course that builds detections which catch real attacks without drowning the SOC in noise. Work the detection pipeline - eight stages from idea to measured value: Sources, Hypothesis, Author, Test, Tune, Deploy, Coverage, and Measure - writing threat-informed, robust, tested, tuned, and measured detections with real Sigma rules, SIEM queries, safe atomic tests, and ATT&CK coverage. Four hands-on activities in every lesson.
15 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Confirm the telemetry a detection needs exists, is complete, and is reliable.
- Write threat-informed hypotheses that target behaviours over indicators.
- Author evasion-resistant logic and test it safely to fire on the true positive.
- Tune for precision, ship detections as code, map ATT&CK coverage, and measure efficacy.
Price:৳8,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.