← Back to catalogue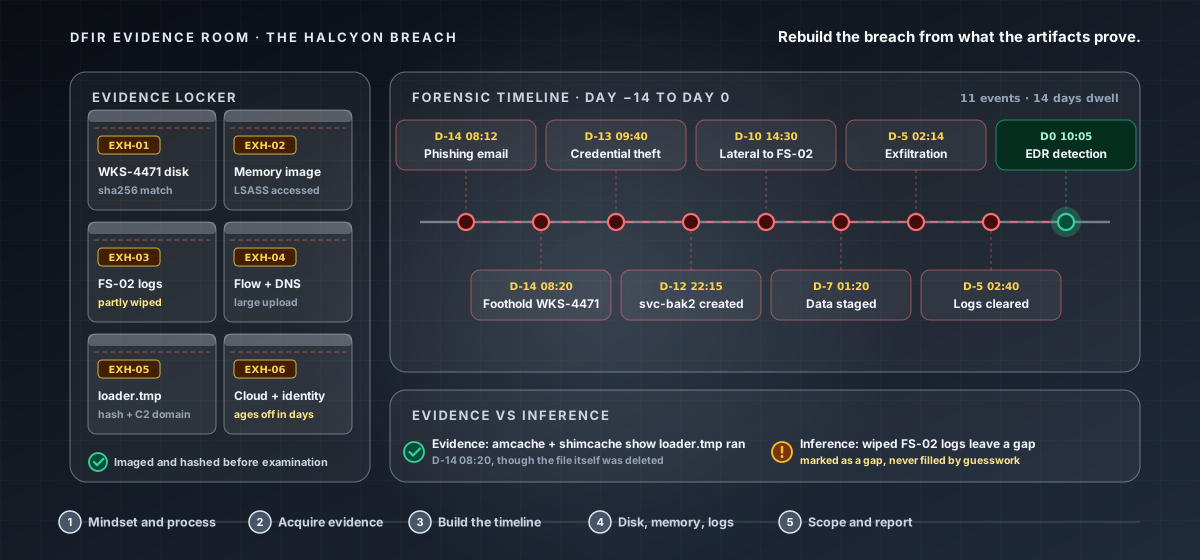
CY-EXPERT-034Expert Level · Digital Forensics
DFIR Evidence Room — Reconstructing the Breach from the Artifacts
An eighteen-hour expert investigation where you lead a breach case end to end — preserving evidence, reconstructing the forensic timeline across endpoint, memory, log, network, cloud, and identity, scoping and eradicating the intrusion, and reporting conclusions that hold.
18 hours12 chapters48 lessons236 activities12 labs
What you'll learn
- Run a defensible investigation that separates established evidence from inference.
- Acquire evidence soundly and reconstruct a forensic timeline across all sources.
- Analyze disk, memory, log, network, malware, cloud, and identity artifacts.
- Scope and eradicate an intrusion and report conclusions that hold under scrutiny.
Price:৳12,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.