← Back to catalogue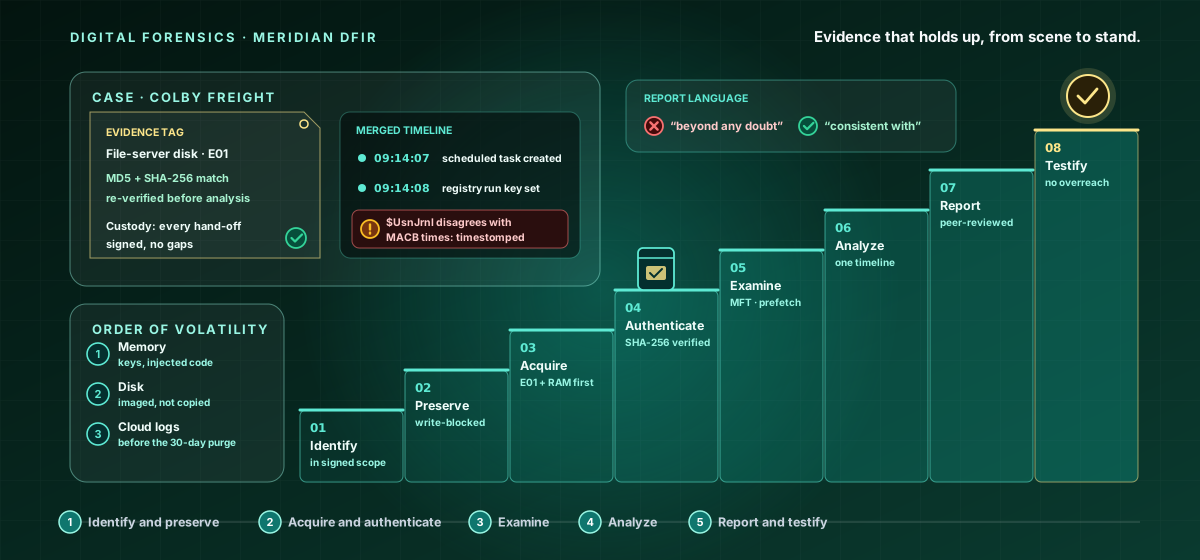
CY-MID-022Mid Level · Digital Forensics
Digital Forensics & Evidence Handling — The Evidence Staircase
A hands-on mid-level course that turns a suspect system into defensible evidence. Climb the evidence staircase - eight steps from scene to stand: Identify, Preserve, Acquire, Authenticate, Examine, Analyze, Report, and Testify - imaging with write-blockers, proving integrity with hashes, keeping chain of custody, and building a timeline that holds up. Grounded in NIST 800-86 and ISO 27037; lawful and authorized throughout. Four hands-on activities in every lesson.
15 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Preserve and acquire evidence in order of volatility without altering it.
- Prove image integrity with hashing and keep an unbroken chain of custody.
- Examine file-system, registry, and memory artifacts and build a sound timeline.
- Write a defensible report and present findings that withstand scrutiny.
Price:৳8,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.