← Back to catalogue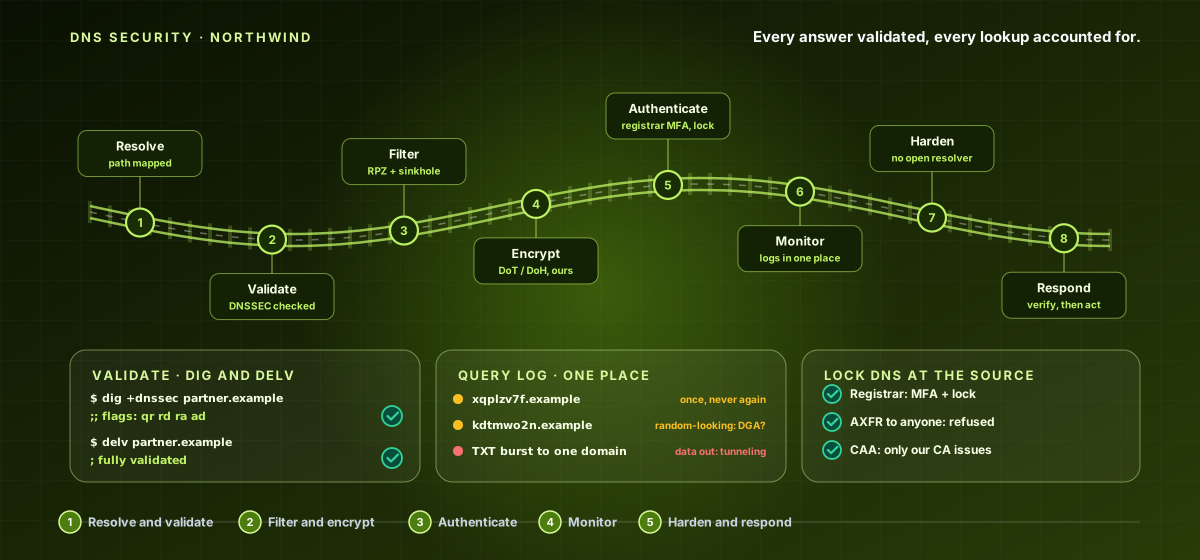
CY-MID-029Mid Level · DNS Security
DNS Security — The DNS Defense Rail
A hands-on mid-level course that secures resolvers, zones, and DNS traffic. Work the DNS defense rail - eight stations: Resolve, Validate, Filter, Encrypt, Authenticate, Monitor, Harden, and Respond - deploying DNSSEC, RPZ filtering, encrypted DNS, tunneling detection, and resolver hardening with real dig, BIND/Unbound, and log work. Strictly defensive. Four hands-on activities in every lesson.
15 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Explain DNS threats and validate answers with DNSSEC.
- Filter malicious domains with RPZ and sinkholing.
- Encrypt DNS and protect zone and registrar integrity.
- Detect tunneling, harden resolvers, and respond to DNS abuse.
Price:৳8,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.