← Back to catalogue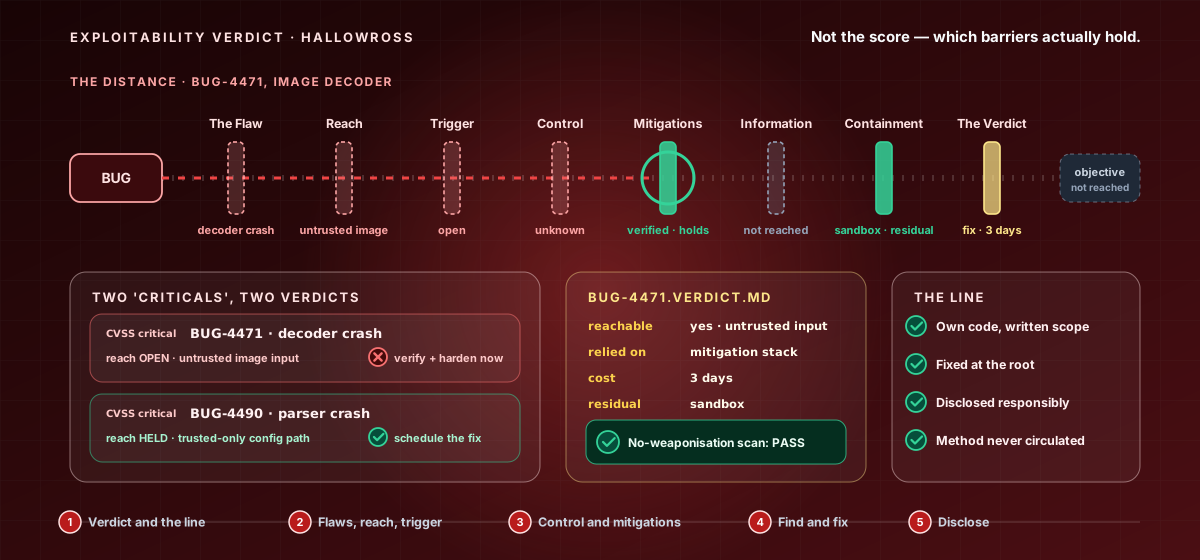
CY-EXPERT-004Expert Level · Exploit Development
Exploit Development — The Exploitability Verdict
The defender's mastery of exploitation: understanding how a bug becomes an exploit well enough to render a verdict on whether it can, defeat it barrier by barrier, and fix the class at the root — with no exploit construction, no weaponisation, and no deployable technique anywhere in the course.
21 hours9 chapters36 lessons259 activities9 labs
What you'll learn
- Render an exploitability verdict as which barriers hold, under what conditions — never as a proof-of-concept.
- Treat written authorisation as the absolute precondition, and make the reach, trigger and control barriers hold without ever building a primitive.
- Verify the mitigation stack present, correct and independent, and make information and containment hold by leak reduction and isolation.
- Find flaws safely on your own code, fix at the root, retire the class by variant analysis, and disclose responsibly without ever circulating a working exploit.
Price:৳12,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.