FedRAMP & Government Cloud Authorization Program — The Authorization Staircase
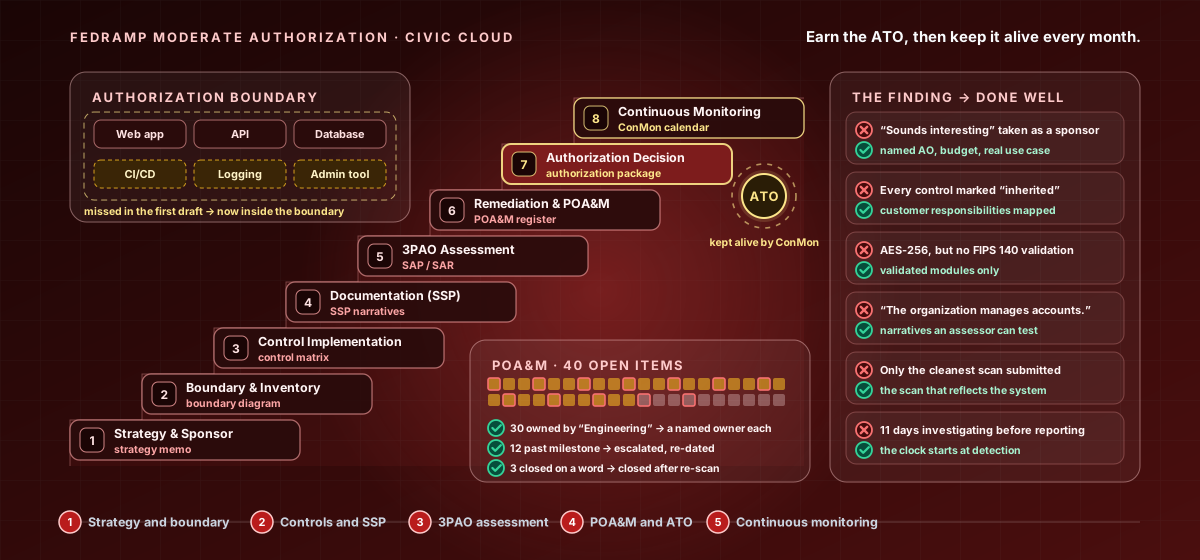
A senior GRC program course that runs a FedRAMP Moderate authorization end to end. Climb the authorization staircase - eight steps: Strategy & Sponsor, Boundary & Inventory, Control Implementation, Documentation (SSP), 3PAO Assessment, Remediation & POA&M, Authorization Decision, and Continuous Monitoring - building a strategy memo, a boundary diagram, a control implementation matrix, an SSP, a 3PAO-ready assessment package, a POA&M, an authorization decision brief, and a continuous-monitoring plan, grounded in NIST SP 800-53 Rev 5, NIST SP 800-37, FedRAMP program guidance, StateRAMP, and the DoD Cloud Computing SRG. Four hands-on activities in every lesson, built from real program artifacts, not shell commands.
What you'll learn
- Build a credible authorization strategy, categorize the system honestly, and secure a genuine sponsoring agency.
- Draw an accurate authorization boundary, map data flows, and control boundary creep over time.
- Implement the NIST 800-53 Rev 5 Moderate baseline with FedRAMP parameters, owned and evidenced control by control.
- Risk-rate findings honestly, run the POA&M to verified closure, and earn and sustain the ATO through continuous monitoring.
Sign in to enrol — you can pay by bKash or Nagad, or apply a promo code.