Firewall Policy Optimisation
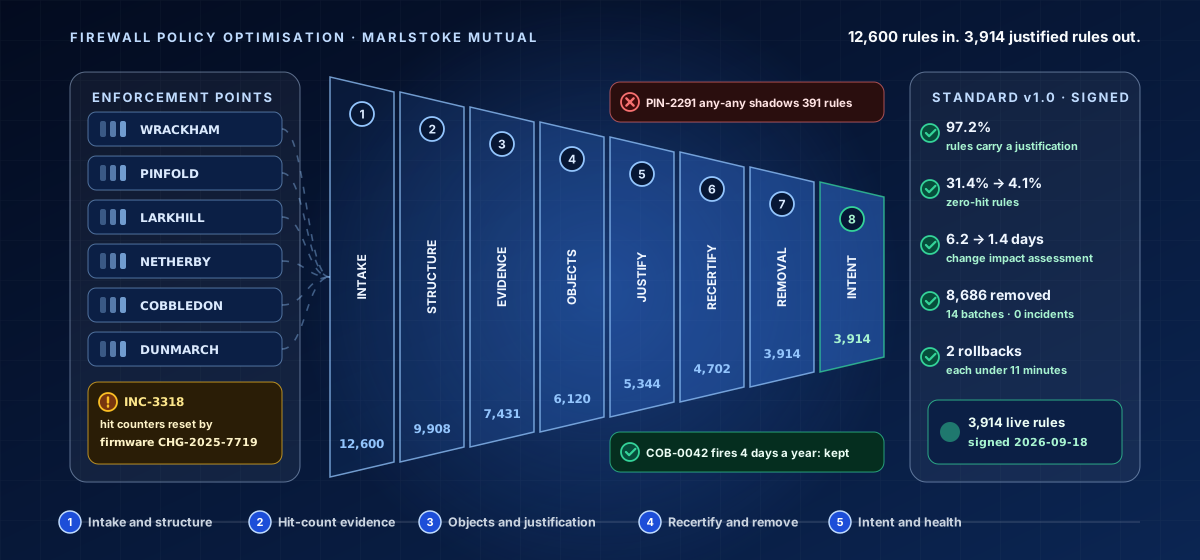
An expert-level course on taking a rule base that has grown for a decade and making it small, justified, owned and evidenced without breaking the business. Work the policy funnel - eight narrowing bands from 12,600 rules to 3,914: why rule bases rot and what an intake actually contains; reading the policy as a program rather than a list, and why shadowing is a correctness problem; hit counts and last-hit data as evidence, including the rule that only fires at quarter end; object and group hygiene and the sprawl that hides what a rule permits; justification records tying every rule to a reason, an owner and a review date; the recertification cycle that keeps the register honest; staged disablement, monitoring, rollback and the evidence that nothing broke; and segmentation intent against enforcement, reported as a governed trend.
What you'll learn
- Trace a removal incident to the evidence defect that permitted it, count the four mechanisms by which a rule base rots, and take a single dated policy intake with provenance sufficient for independent re-performance.
- Read a policy as a first-match program, build an evaluation model per device, and classify every rule as effective, shadowed, redundant or subsumed - including the counterfactual for every any-any rule.
- Publish hit counts with their counter start dates, derive an observation window from the business calendar, protect periodic rules by calendar, and corroborate every removal candidate against two independently failing sources.
- Expand every rule to the addresses and ports it permits, inventory and deduplicate the object model on resolved sets, derive object ownership from the systems behind the members, and prove a consolidation changes nothing using expansion hashes.
Sign in to enrol — you can pay by bKash or Nagad, or apply a promo code.