← Back to catalogue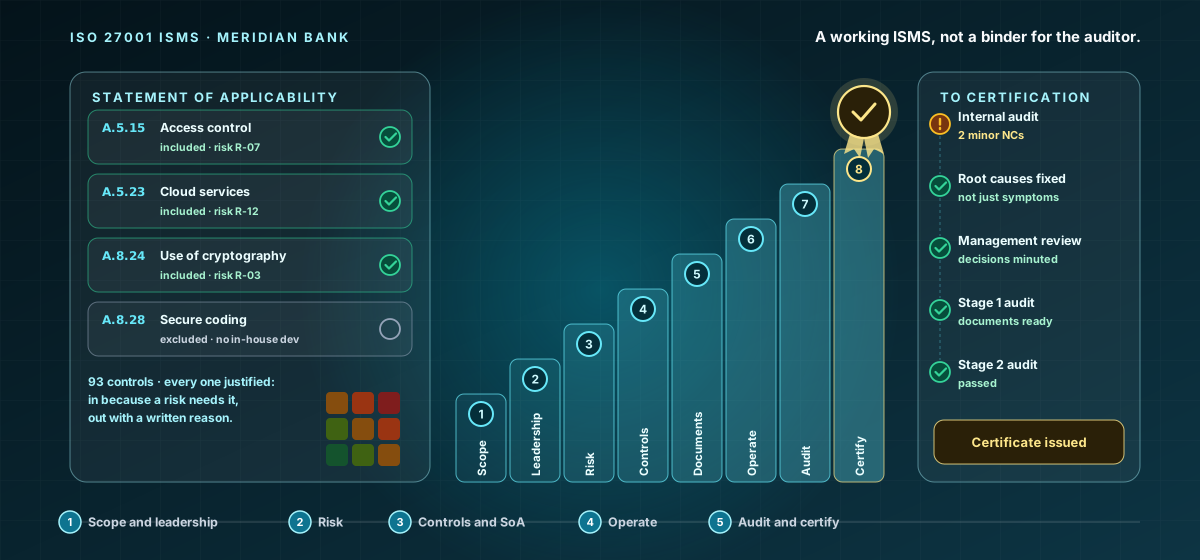
CY-MID-070Mid Level · ISO 27001
ISO 27001 ISMS Implementation — The ISMS Staircase
A hands-on mid-level course that stands up an ISO 27001 information security management system. Climb the ISMS staircase - eight steps: Scope, Leadership, Risk, Controls, Documents, Operate, Audit, and Certify - building a real, working ISMS rather than a binder for the auditor. Honest and audit-ready. Four hands-on activities in every lesson.
14 hours8 chapters32 lessons220 activities8 labs
What you'll learn
- Scope the ISMS and secure real leadership commitment.
- Run risk assessment and select Annex A controls with an SoA.
- Operate the ISMS with the documentation that matters.
- Pass internal audit, management review, and certification honestly.
Price:৳8,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.