← Back to catalogue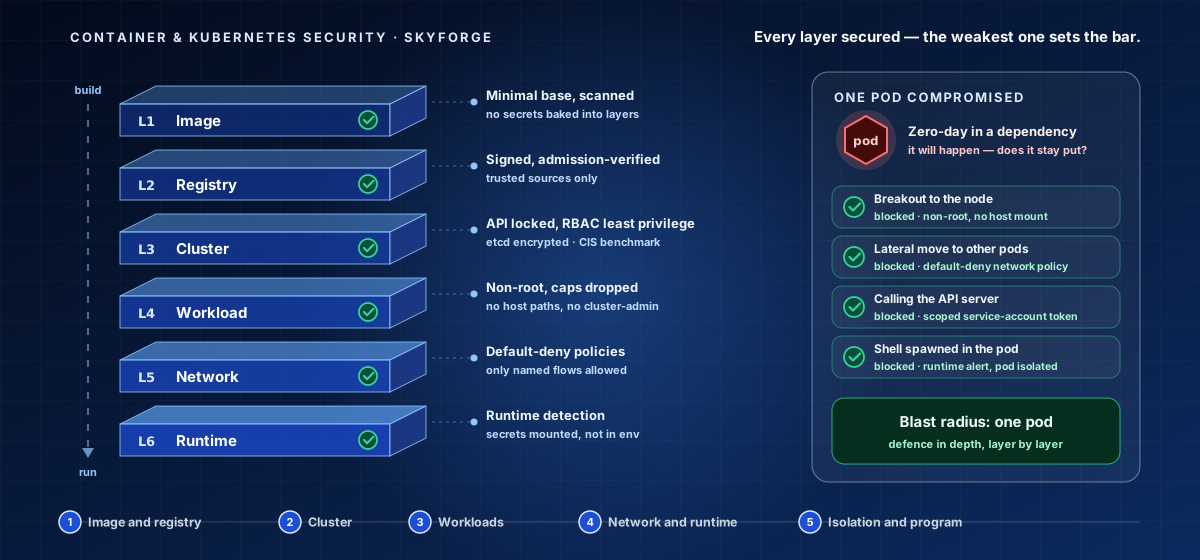
CY-EXPERT-002Expert Level · Container and Kubernetes Security
Container & Kubernetes Security — The Stack
A twenty-hour, highly interactive expert-level course where you secure a Kubernetes platform layer by layer — image, registry, cluster, workload, network, runtime. Containers share the host kernel so isolation is weaker than a VM's, and most risk is misconfiguration and excess privilege. Least privilege and isolation at every layer, so a compromise is contained. Four hands-on activities in every lesson.
20 hours9 chapters45 lessons295 activities9 labs
What you'll learn
- Build minimal, scanned, signed images and enforce admission so only verified images run.
- Harden the control plane and RBAC, and run least-privilege workloads.
- Segment the network default-deny, manage secrets, and detect runtime threats.
- Isolate tenants, limit blast radius, and run a container security program.
Price:৳12,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.