Legal Boundaries in Security Assurance
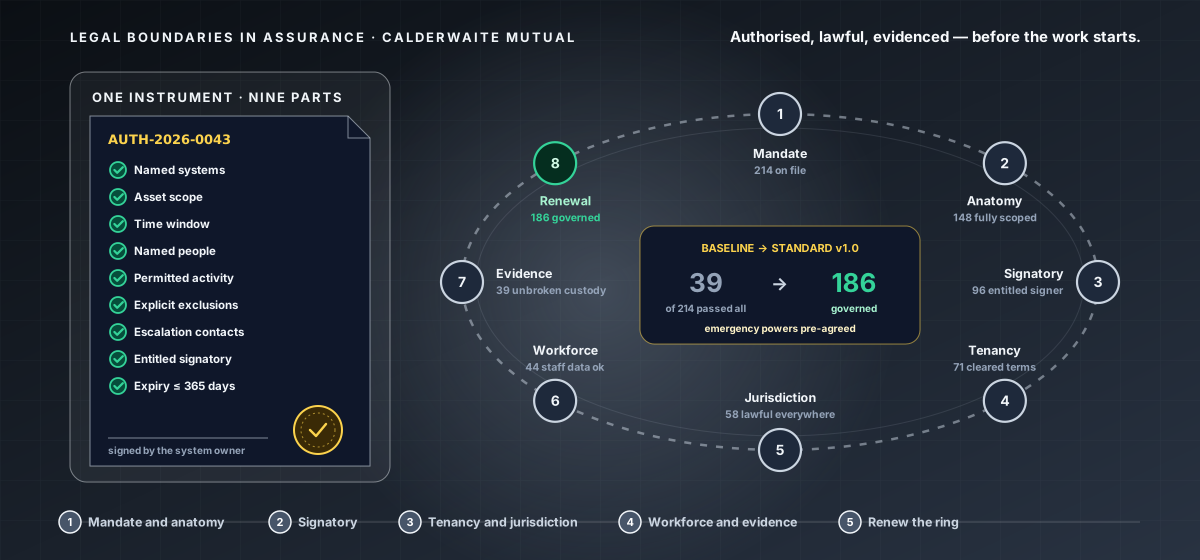
An expert-level governance course on making sure the testing and monitoring a security function performs is authorised, lawful and evidenced, so that the people doing the work are protected and the material it produces is usable. Work round the ring - eight segments of a closed loop: why written authorisation exists and whom it protects; the anatomy of an instrument a stranger can read; who is actually entitled to sign for a given system; shared platforms and supplier environments where somebody else's terms set the boundary; jurisdiction and data location in monitoring; employee monitoring, proportionality, notice and consultation; evidence handling and chain of custody; and the emergency powers and review cycle that close the loop and start it again.
What you'll learn
- Reconcile the assurance activities genuinely running against the authorisation records held, and publish covered, drifted and uncovered as separate counts with the uncovered set ranked by exposure.
- Write an authorisation instrument with nine mandatory parts - named systems, asset scope, time window, named people, permitted activity, exclusions, escalation, signatory and expiry - and prove it by reconstruction with an uninvolved reader.
- Determine who is entitled to authorise work on a given system on control, accountability or contractual grounds, and migrate a wrongly signed population in sequenced tranches with a lapse default that fires.
- Clear every enumerated action against the operating party's terms on shared infrastructure, assess multi-tenant impact through the operator, and apply a standing test that withdraws instruments for supplier environments and substitutes contractual assurance rights.
Sign in to enrol — you can pay by bKash or Nagad, or apply a promo code.