← Back to catalogue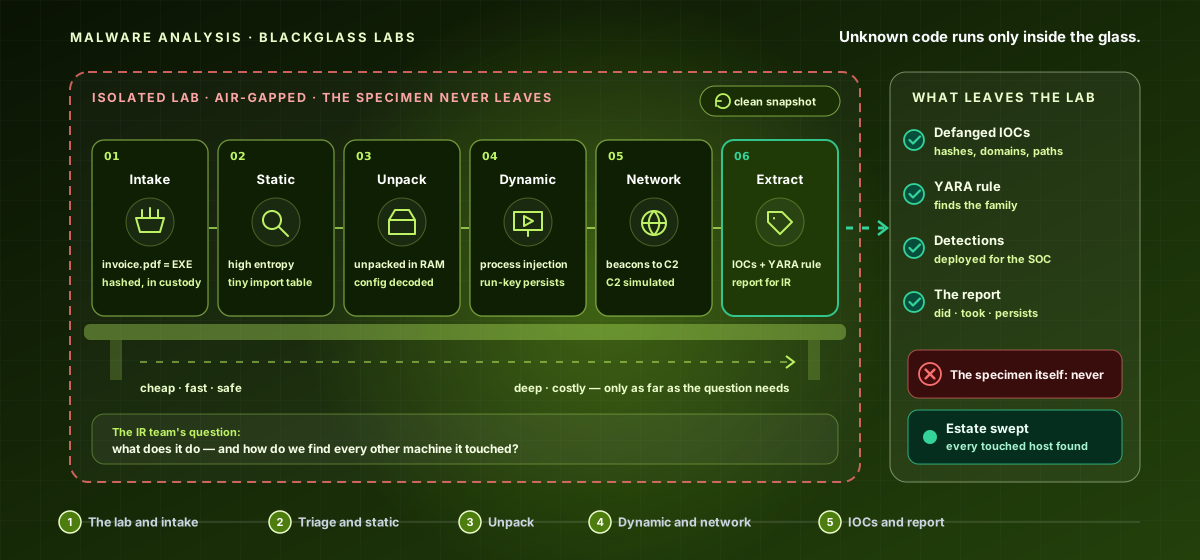
CY-EXPERT-011Expert Level · Malware Analysis
Malware Analysis — Decode the Threat
A twenty-hour, highly interactive expert-level course where you are a malware analyst working an escalation ladder inside an isolated lab — triage, static, unpacking, dynamic, network, and code-level analysis — turning unknown, hostile code into the capabilities, IOCs, and detections defenders need. Strictly defensive and contained. Four hands-on activities in every lesson.
20 hours9 chapters45 lessons295 activities9 labs
What you'll learn
- Handle and analyse specimens safely inside an isolated, instrumented, revertible lab.
- Triage, statically analyse, unpack, and deobfuscate specimens proportionately.
- Detonate specimens to observe behaviour, and analyse network and C2 communication.
- Extract IOCs, engineer layered detections, reverse-engineer where needed, and report clearly.
Price:৳12,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.