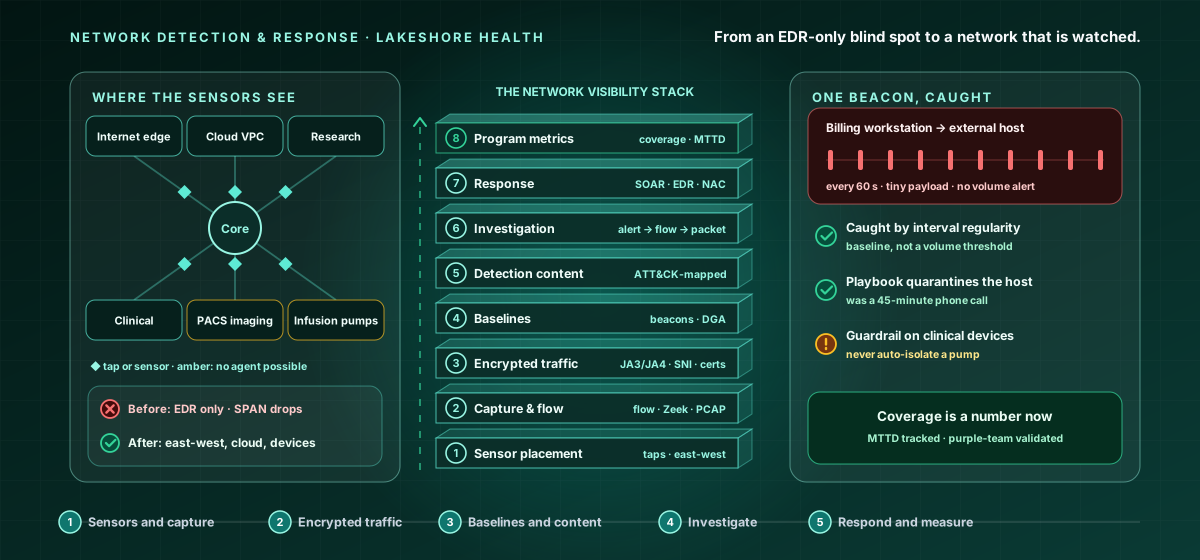
Network Detection & Response Program — The Network Visibility Stack
A senior-level program-building course that takes a network from EDR-only and blind to actually watched, detected, and defended. Work the network visibility stack - eight layers: Sensor Placement, Traffic Capture & Flow, Encrypted Traffic Strategy, Baselines & Behavioral Analytics, Detection Content, Investigation & Forensics, Response Integration, and Program Metrics - with real tap and sensor placement, NetFlow/Zeek/PCAP, JA3/JA4 and TLS analytics, beaconing detection, Suricata/Zeek content mapped to MITRE ATT&CK, session reconstruction, SOAR/EDR/NAC response integration, and coverage and MTTD metrics, on a hospital network with flat legacy segments and agentless medical devices. Four hands-on activities in every lesson.
What you'll learn
- Place sensors at real choke points - including east-west and agentless devices - and capture flow and packets deliberately against a retention budget.
- Apply encrypted-traffic analytics as the default approach to TLS, reserving selective, scoped decryption for cases that truly need it.
- Baseline assets and peer groups and build signature and behavioral detection content, mapped and tuned against MITRE ATT&CK, that analysts actually trust.
- Investigate by pivoting from alert to flow to packet with evidence intact, and wire validated findings to automated response and program metrics.
Sign in to enrol — you can pay by bKash or Nagad, or apply a promo code.