← Back to catalogue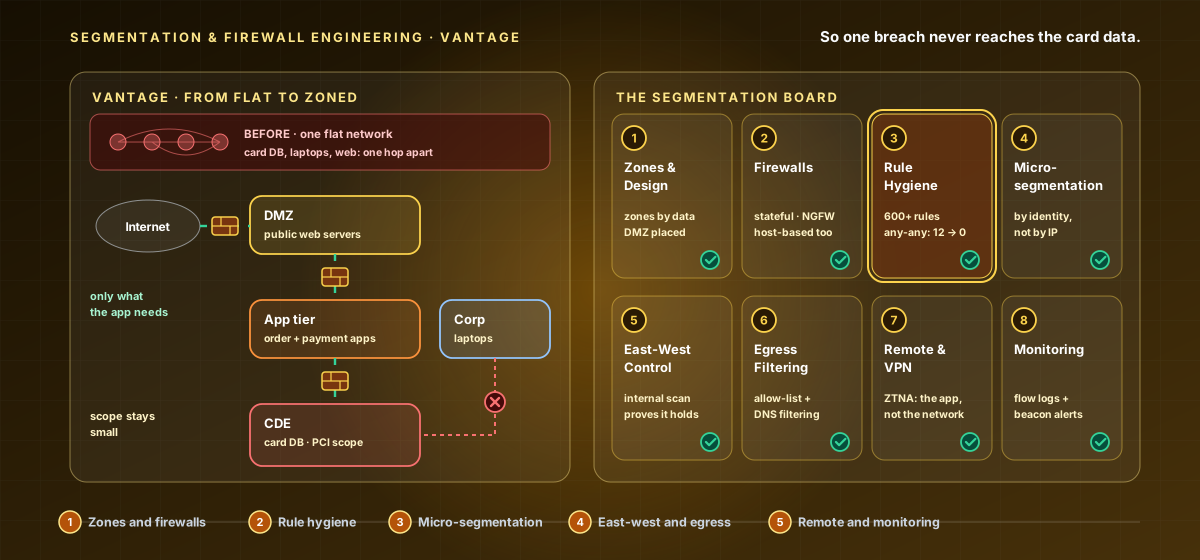
CY-MID-035Mid Level · Network Segmentation
Network Segmentation & Firewall Engineering — The Segmentation Board
A hands-on mid-level course that carves a flat network into defensible zones. Work the segmentation board - eight domains: Zones & Design, Firewalls, Rule Hygiene, Micro-segmentation, East-West Control, Egress Filtering, Remote & VPN, and Monitoring - designing trust zones, least-access firewall rules, and lateral-movement containment with real rule and flow work. Strictly defensive. Four hands-on activities in every lesson.
15 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Design trust zones and a segmentation strategy that fits the risk.
- Write least-access firewall rules and keep the rule base clean.
- Contain lateral movement with micro-segmentation and east-west control.
- Filter egress, secure remote access, and monitor the flows.
Price:৳8,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.