← Back to catalogue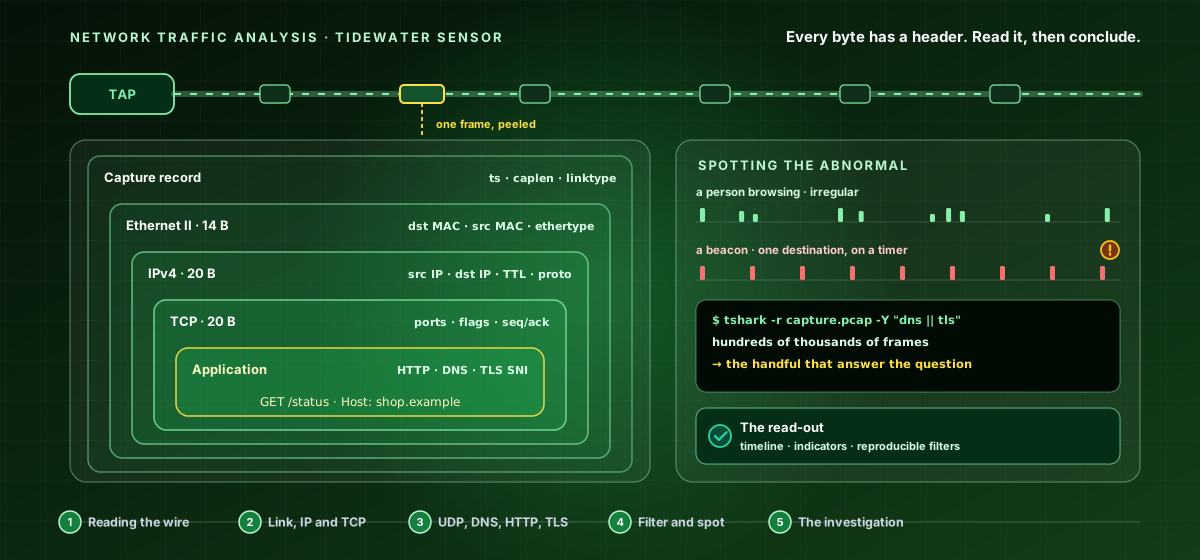
CY-MID-036Mid Level · Network Security
Network Traffic Analysis — Reading the Wire
A deeply technical, hands-on mid-level course that reads network traffic at the byte and protocol level. Peel each frame apart on the packet dissector — Ethernet, IP, TCP/UDP, and the application payload — and learn to find, follow, and interpret the packets that matter, from real capture files with real tcpdump and tshark syntax. Four hands-on activities in every lesson.
16 hours8 chapters40 lessons265 activities8 labs
What you'll learn
- Open a capture and peel a frame apart by encapsulation, reading each layer's fields from the bytes.
- Read Ethernet, IP, ARP, and a full TCP conversation by sequence and acknowledgment numbers.
- Read UDP services (DNS, DHCP), HTTP in the clear, and what TLS hides and reveals.
- Write precise tcpdump/tshark filters and recognise scan, beacon, exfiltration, and spoofing signatures.
Price:৳8,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.