← Back to catalogue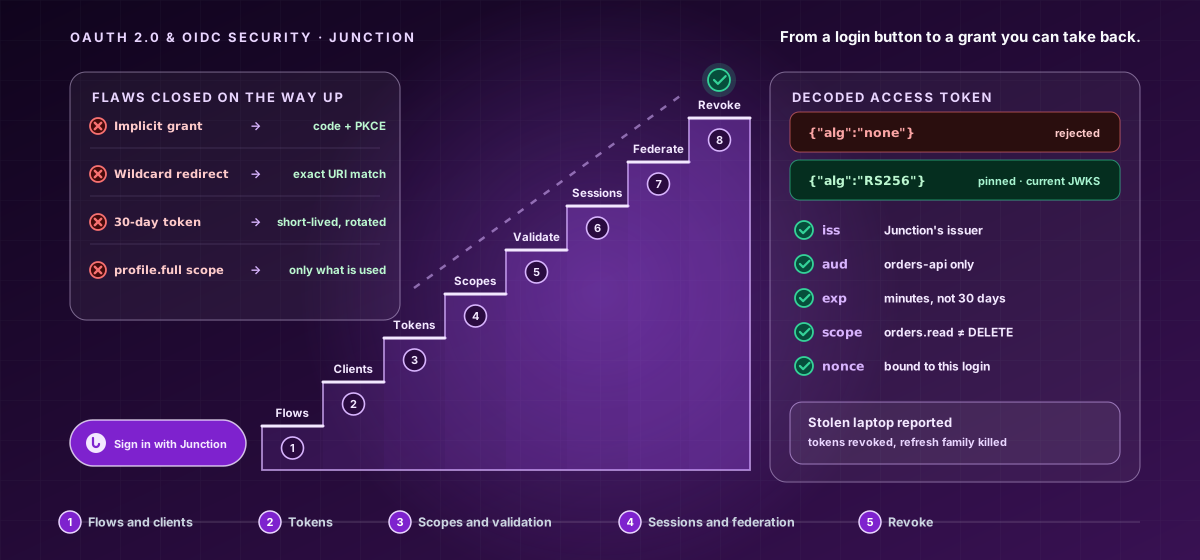
CY-MID-057Mid Level · OAuth & OIDC Security
OAuth 2.0 & OIDC Security — The Authorization Staircase
A hands-on mid-level course that implements OAuth 2.0 and OpenID Connect securely. Climb the authorization staircase - eight steps: Flows, Clients, Tokens, Scopes, Validate, Sessions, Federate, and Revoke - choosing the right flow with PKCE, validating JWTs correctly, and closing the misconfigurations that break auth. Strictly defensive. Four hands-on activities in every lesson.
15 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Choose the right OAuth flow and use PKCE correctly.
- Register clients safely and handle tokens without leaking them.
- Validate JWTs (signature, aud, iss, exp) and scope access least-privilege.
- Manage sessions, federation, and revocation securely.
Price:৳8,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.