← Back to catalogue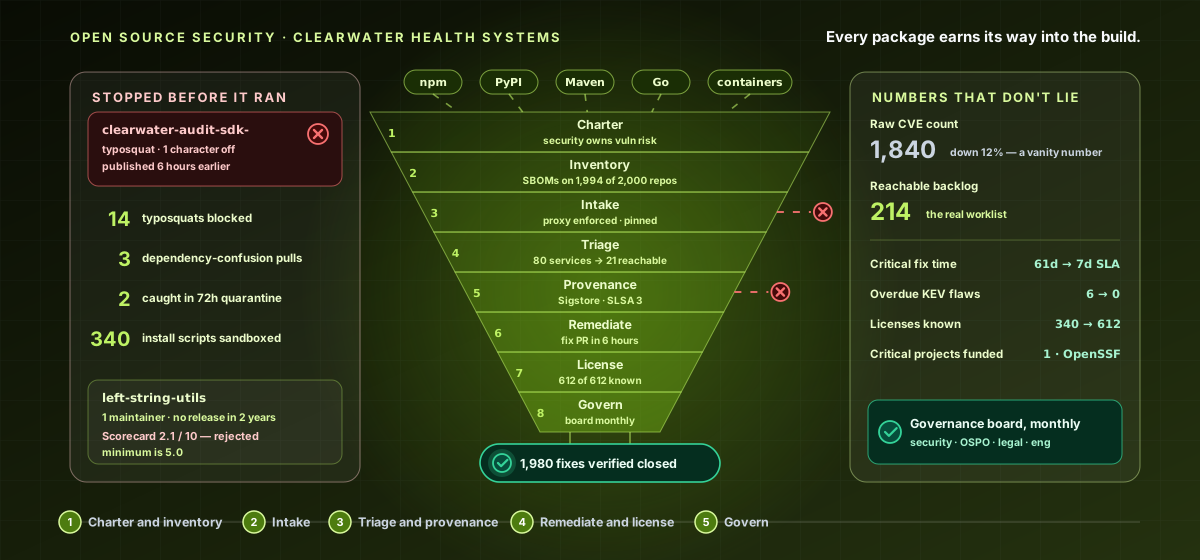
CY-SENIOR-105Senior Level · Open Source Security
Open Source Security Program — The Dependency Funnel
A senior-level program course that secures an organization's own use of open source, deliberately and continuously, from charter through governance, across eight stages of the dependency funnel — charter, inventory, intake, triage, provenance, remediation, license, and governance.
16 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Charter the program's ownership split with OSPO and scope it to direct and transitive dependencies, containers, and AI models.
- Build an automated, fleet-wide SBOM foundation with a central, queryable inventory, and gate intake with health scoring and provenance checks.
- Triage vulnerabilities with multi-source feeds, EPSS/KEV, and reachability analysis, defending against malicious and compromised packages.
- Track remediation to a verified close, clear license and export obligations, and govern the program with honest metrics and real continuity.
Price:৳10,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.