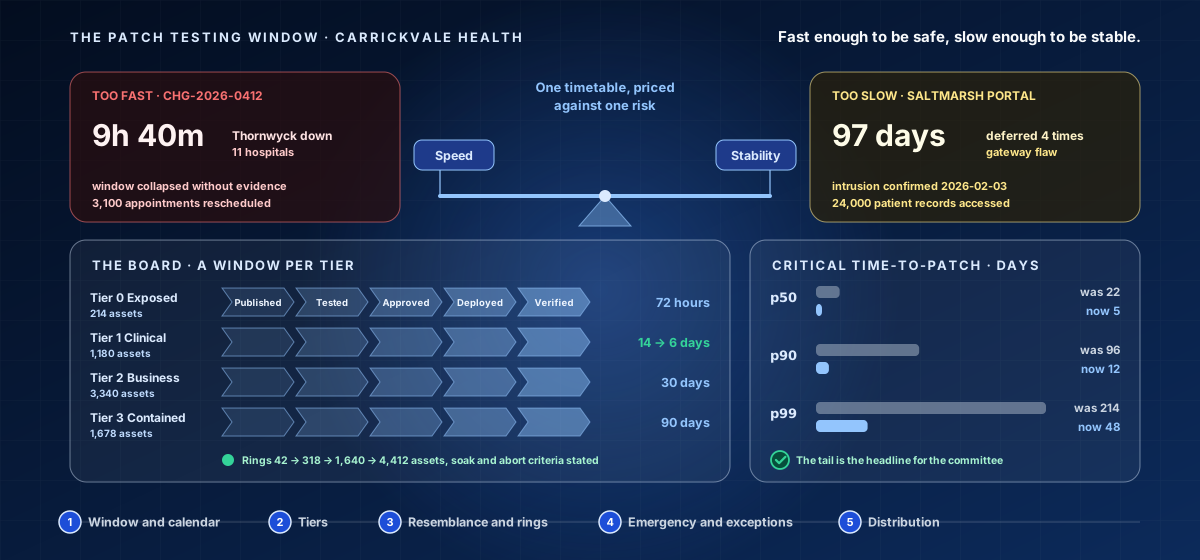
The Patch Testing Window Challenge
An expert-level security operations course on getting security patches into production quickly without breaking the business, and on defending the timetable when speed and stability are demanded at once. Work across the board - eight rows and five pipeline stages: what the window is actually buying, the calendar the estate really has, tiering and sizing windows from evidence, measuring how far pre-production resembles production, shortening the window honestly with automation and rings, collapsing it under written tests with the decision recorded at the time, governing the patches that cannot be applied at all, and reporting the distribution so that the tail, not the average, is the story the business owns.
What you'll learn
- Price both patch failure modes in the organisation's own figures and publish a dated, reproducible baseline in counts and days that every later component reconciles to.
- Count usable window-hours from operational records, classify the capacity gap by blocking cause and owner, and draw freezes, clinical hours, certification lead times and change cadence on one annual axis with exposure forecast in advance.
- Tier an estate by reachability, blast radius and rollback cost under a written rule, size each tier's window from observed decomposition and rollback detection history, and handle tier drift by event-driven and scheduled re-derivation.
- Score how far pre-production resembles production across named dimensions, allocate a fixed budget by defect attribution rather than by lowest score, and attach a generated fidelity statement to every test result.
Sign in to enrol — you can pay by bKash or Nagad, or apply a promo code.