← Back to catalogue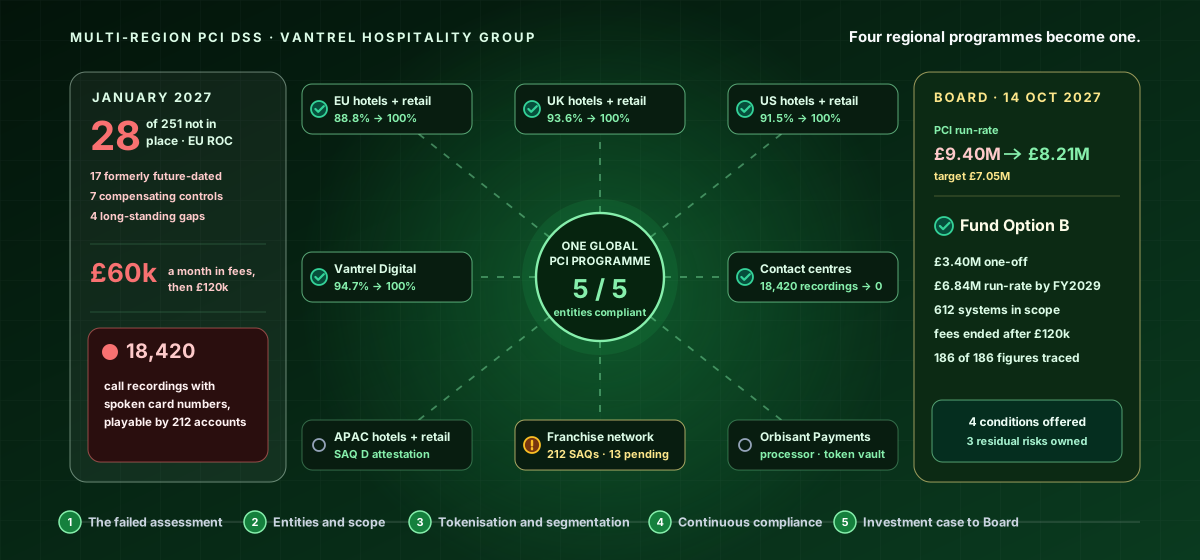
CY-PRO-003Pro Level · Payment Security and PCI DSS
Multi-Region PCI DSS Program Strategy
A forty-hour Pro-level command simulation run on a live PCI multi-region command board. You lead a global hotel and retail group's payment security through a failed EU ROC and an acquirer's fees, card numbers in contact-centre recordings, the formerly future-dated PCI DSS v4.x requirements landing on every region at once, and a Board demand for one global programme instead of four. The course runs from decomposing the failure, through entities, scope, devaluation, segmentation, providers, approaches, continuous compliance and incident response, to an investment case and a Board defence built entirely on evidence.
40 hours12 chapters60 lessons433 activities12 labs
What you'll learn
- Diagnose a failed assessment by cause across entities, answer acquirers through counsel, reconcile merchant IDs and attestations, and draw one honest scope that every entity inherits.
- Land the formerly future-dated requirements with targeted risk analyses, and reduce scope through tokenisation, validated P2PE, DTMF masking and hosted payment fields, proven by discovery and re-scan.
- Prove segmentation, govern internal and external service providers with responsibility matrices, and choose between defined, customised and compensating approaches with retirement triggers.
- Keep compliance continuous through calendars, owners and drift indicators, respond to incidents on evidence, and defend an optioned investment case with banked and dependent benefits and a combined worst case to a board.
Price:৳15,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.