PHI Minimum Necessary Access Governance
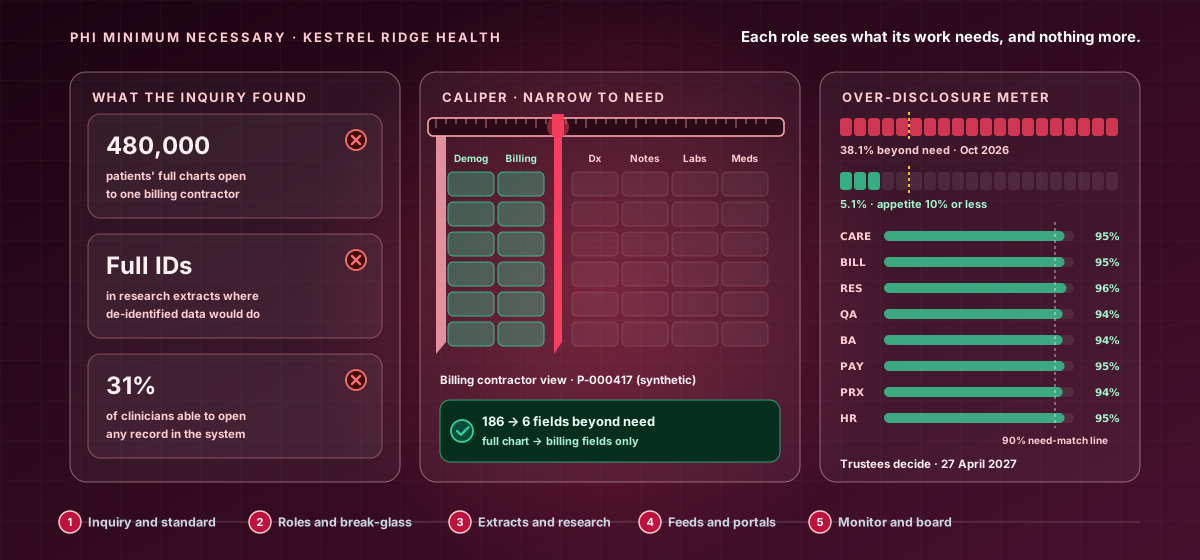
A forty-hour Pro-level health-system privacy governance simulation run on a live minimum necessary command board, where you are Chief Privacy and Information Security Officer of a US regional health system; a complaint about a billing contractor's collections call triggers a regulator inquiry and exposes a contractor with full-chart access to 480,000 patients, research extracts full of identifiers nobody needed and 31% of clinicians able to open any record — and you measure the truth, contain it, rebuild access around clinical work, govern every pathway PHI leaves by, weigh restriction against patient safety, price the programme at the margin and win the Board's resolution.
What you'll learn
- Measure minimum necessary honestly across every PHI pathway — need match, fields beyond need and a volume-weighted over-disclosure rate — and contain an exposure without disrupting care or revenue.
- Design clinical access around treatment relationships with justified broad-access roles, sensitive-class conditions and a reviewable break-glass, and govern extracts, analytics, research, business associates, payers and proxies field by field.
- Monitor and evidence access with complete audit logs, anomaly detection, proactive audit and chain of custody, and weigh restriction against patient safety with measured friction and a clinical safety case.
- Price the programme at the margin, set a measurable restriction appetite, present residual risk for acceptance by the right authority and win a Board resolution that can be held to account.
Sign in to enrol — you can pay by bKash or Nagad, or apply a promo code.