PHI Safeguard Architecture Assurance
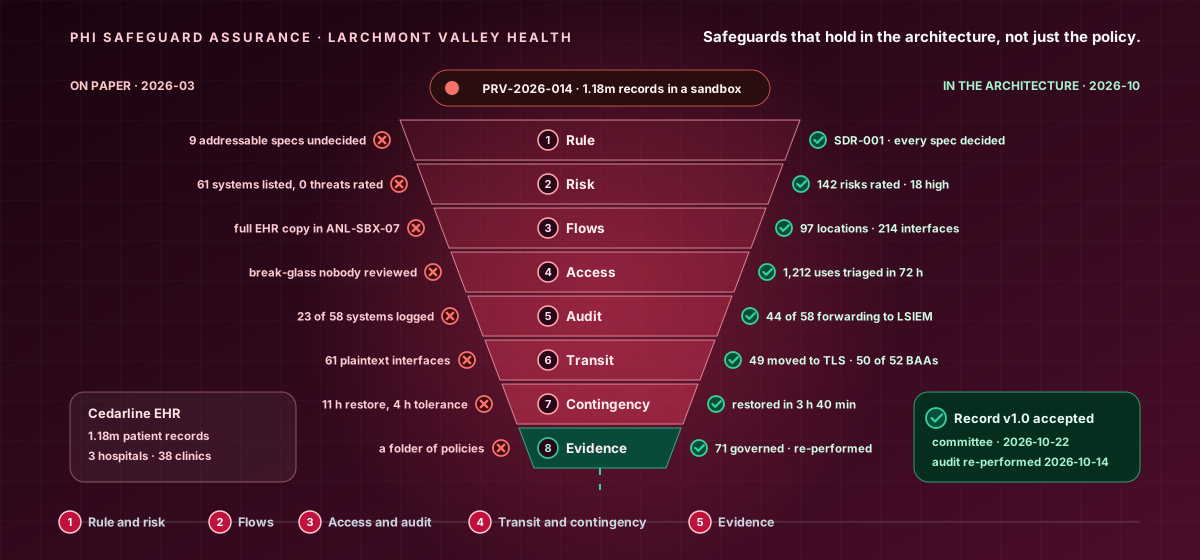
An expert-level healthcare GRC and architecture course on proving that the administrative, physical and technical safeguards around protected health information hold in the real architecture, not just in the policy set. Work down the Larchmont PHI Funnel - eight bands from everywhere ePHI is created and copied to a governed, evidenced footprint: reading the Security Rule's structure and deciding every addressable specification; replacing an asset list with a real risk analysis; mapping where ePHI actually flows, copies included; governing access, minimum necessary and break-glass; making audit logs something somebody reads; protecting interfaces and matching business associate agreements to the data shared; proving clinical systems recover inside clinicians' tolerance; and recording breach assessments at the time before assembling a Record internal audit can re-perform.
What you'll learn
- Read the Security Rule's administrative, physical and technical safeguards as layers across every ePHI location, and decide and document every addressable specification.
- Replace an asset list with a risk analysis of rated threat-vulnerability pairs, with owners, treatments, acceptance levels and update triggers.
- Build an ePHI flow register from system configurations, authorised discovery and catalogues that finds analytics copies, exports, test data and backups, and disposition each.
- Size access to purpose under minimum necessary, keep one identity per person, and design and review break-glass access so that it never delays care.
Sign in to enrol — you can pay by bKash or Nagad, or apply a promo code.