PIMS and Privacy Defensibility
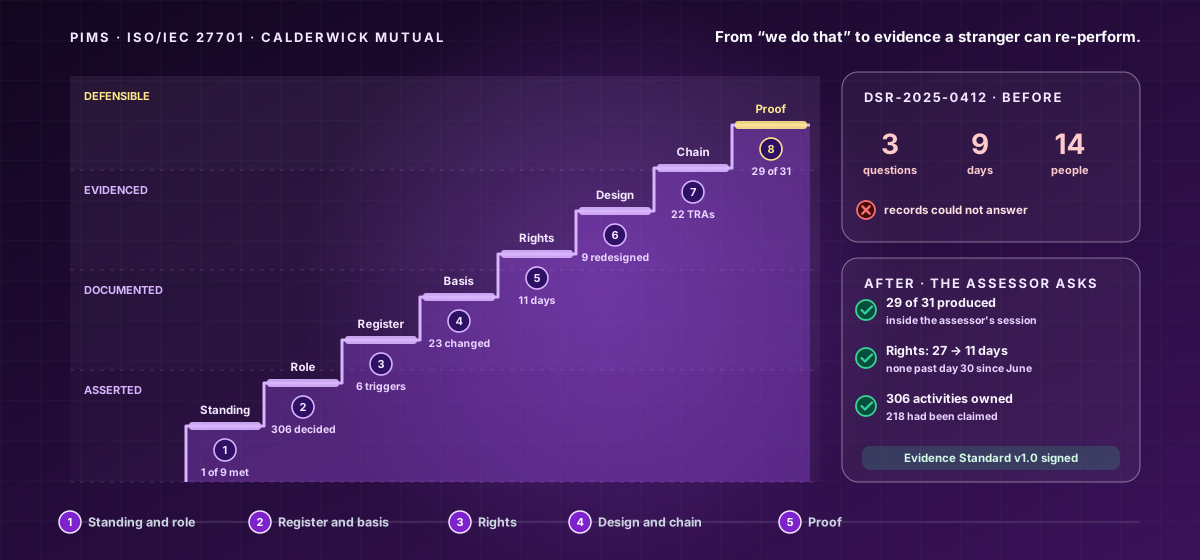
An expert-level privacy governance course on turning asserted privacy controls into evidence that stands up to a regulator, an assessor or a data subject complaint. Climb the staircase - eight treads from asserted to defensible: what a privacy information management system adds to an ISMS and why 27701 sits on top of 27001; controller and processor roles determined per activity rather than per contract; the record of processing as a live control; lawful basis recorded as a decision rather than a label; rights operations with a verified requester, an honest clock and a withholding somebody owns; assessments that change a design; processors, sub-processors and transfers assessed against the measure you would actually apply; and breach assessment, the notification decision and the evidence an assessor actually asks for. Illustrative throughout and not legal advice.
What you'll learn
- Publish an evidence standard requiring owner, dated artefact, verification date, refresh band and re-performer, and a privacy baseline measured by evidence age rather than by a maturity score.
- Build a three-column inheritance map that settles what a privacy programme inherits from an existing security management system, what it extends and what it must build from nothing.
- Determine controller, processor and joint controller roles per processing activity with the discretion test and its evidence, and publish an obligation map stating the act, the artefact and the owner for every role.
- Enumerate a processing register from system, integration, supplier, retention and client evidence, specify its fields from the queries it must answer, and keep it live with detectable triggers and rate-of-change verification bands.
Sign in to enrol — you can pay by bKash or Nagad, or apply a promo code.