Procurement Clause Challenge
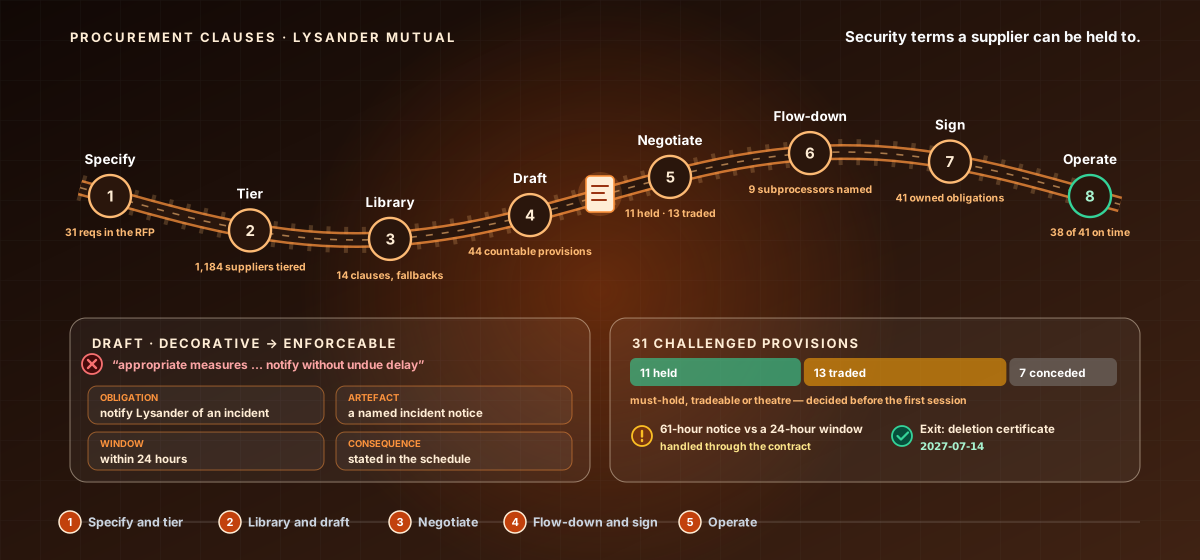
An expert-level course on how a security function gets enforceable security terms into supplier agreements and then actually holds suppliers to them. Travel the contract rail - eight stations along which one agreement moves: writing security requirements before the tender issues; tiering suppliers by the risk they actually carry; building a governed clause library with drafted fallbacks; testing every provision for measurable obligation, named artefact, defined window and stated consequence; negotiating what is worth a fight and what is theatre; making the obligations reach subprocessors; turning a signed schedule into an owned obligation register; and running evidence, remediation, renewal and exit for the life of the relationship.
What you'll learn
- Derive security requirements from what a service holds, touches and creates a dependency on, and get them scored inside the tender while they are still a condition of winning.
- Tier a supplier estate on data, access, dependency, concentration and recoverability, reconcile it across source systems, and define what each tier receives contractually and in assurance.
- Build and govern a clause library with tier applicability, drafted fallback ladders and intent notes, covering the data, assurance and operational clause families.
- Test every provision against measurable obligation, named artefact, defined window and stated consequence, and design consequences proportionate enough to be used.
Sign in to enrol — you can pay by bKash or Nagad, or apply a promo code.