Prompt Injection Architecture Assurance
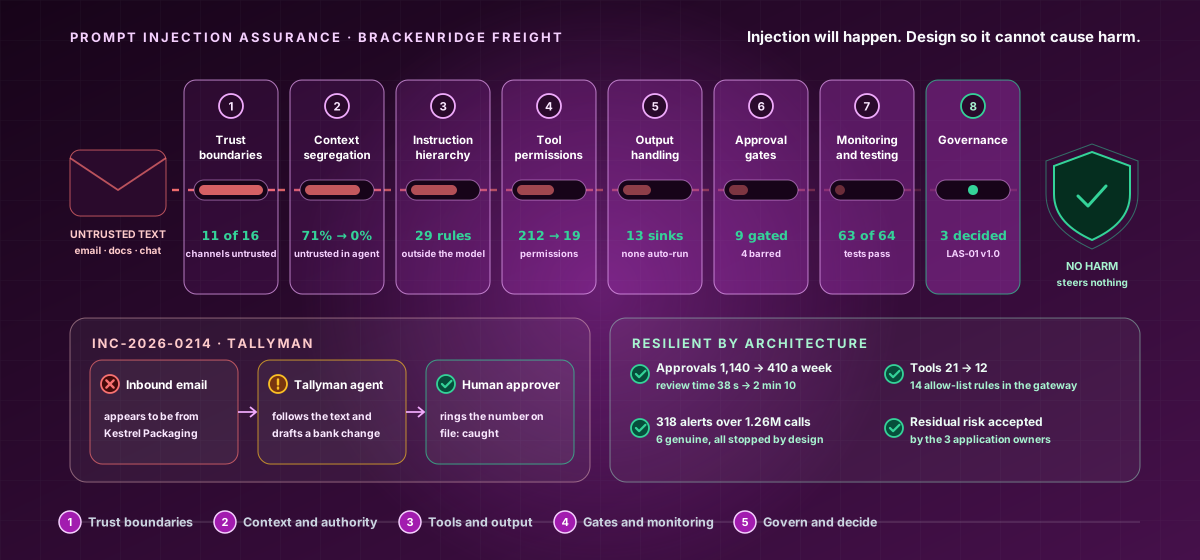
An expert-level architecture assurance course on making an organisation's LLM applications resilient to prompt injection - on the premise that injection cannot be reliably filtered away at the model, so what matters is what untrusted content can influence and what the application is permitted to do. Work down the Injection-Resilience Defence Stack, eight layers that must each hold: trust boundaries on inputs; context and retrieval segregation; the instruction hierarchy; least-privilege tools, scoped credentials and allow-listed actions; output handling; human approval gates; monitoring and assurance testing with a pre-agreed test library; and governance - the review decision, the residual-risk statement and the assembled standard.
What you'll learn
- Contain an injection incident, explain why injection cannot be reliably filtered at the model, model it by source and consequence, and map trust boundaries and the untrusted share of context.
- Measure context composition, segregate retrieval by trust tier and tenant, label provenance, and quarantine untrusted content from the component that holds tools.
- Move must-never rules out of system prompts into enforcing controls, keep secrets out of prompts, tie authority to the session, and specify the instruction hierarchy with its limits.
- Rank tools by blast radius, remove and narrow them, scope their credentials to the tool and the user, and validate every action in a gateway outside the model.
Sign in to enrol — you can pay by bKash or Nagad, or apply a promo code.