QA Pro AcademyCybersecurity A-Z
Join free
← Back to catalogue
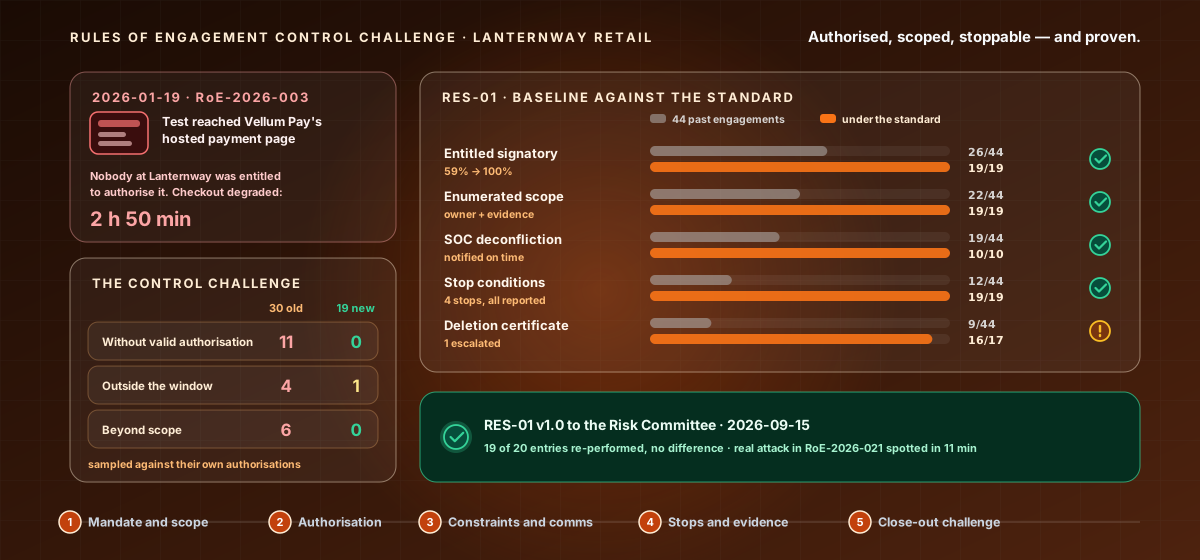
Proving Lanternway Retail Group's rules of engagement are controls that hold: the incident that started it, on 19 January 2026, when an external test under RoE-2026-003 reached supplier Vellum Pay's hosted payment page that nobody at Lanternway could authorise, and checkout degraded for 2 hours 50 minutes; the register comparing 44 past engagements with those under the new standard — entitled signatory 26 of 44 to 19 of 19, enumerated scope 22 of 44 to 19 of 19, SOC deconfliction 19 of 44 to 10 of 10 on time, stop conditions 12 of 44 to 19 of 19, and deletion certificates 9 of 44 to 16 of 17; the control challenge that sampled 30 historic engagements, finding 11 without valid authorisation, 4 outside their window and 6 beyond scope, against 0, 1 and 0 for the 19 under the standard; and RES-01 version 1.0 going to the Risk Committee on 15 September 2026 with 19 of 20 entries re-performed without difference.
CY-EXPERT-009Expert Level · Ethical Hacking

Rules of Engagement Control Challenge

Governing authorised security testing so that every engagement is authorised, scoped, constrained, deconflicted, stoppable and closed out - and proving it to the Risk Committee

18 hours8 chapters32 lessons225 activities8 labs

What you'll learn

  • Write a testing mandate that makes one route the only way to commission testing and states the limits of the programme's authority
  • Require scope as an enumerated list of owned assets with exclusions and a fixed window, changed only by signed amendment
  • Decide who is entitled to authorise testing of which assets, obtain supplier authorisation where required, and gate every start on a verified record
  • Set safety, prohibition, data, timing and load constraints as the organisation's own governance requirements

Price:৳12,000
Sign in to get access

Sign in to enrol — you can pay by bKash or Nagad, or apply a promo code.