Runtime Policy Review
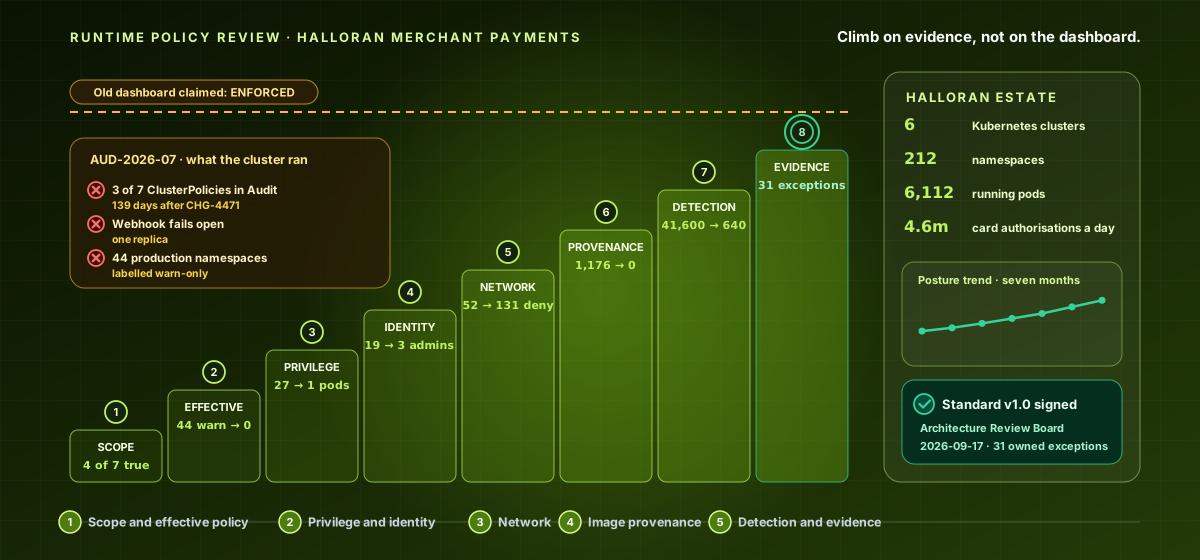
An expert-level course on adversary-aware, strictly read-only review of container and Kubernetes runtime policy - testing whether your own controls would hold, never how to defeat them. Climb the policy staircase - eight treads from a dashboard that claimed everything was enforced to a standard that is enforced, monitored and evidenced: what runtime policy covers and how its six layers depend on each other; reading the effective policy, including audit-only modes, exempted namespaces and webhooks that fail open; privileged workloads, host mounts and host networking, and the legitimate exceptions that need owners rather than removal; RBAC review of cluster-admin, wildcards and unused tokens; network policy as default-deny versus decoration; signed-only image admission; runtime detection tuned to the cluster; and governed exceptions evidenced to an architecture board as a trend.
What you'll learn
- Trace a posture misstatement to the field a dashboard computed from, map the six layers of runtime policy and their dependencies, prove the review identity read-only under written authorisation, and fix a dated inventory as the denominator.
- Read the effective policy from each cluster - modes, exclusions, webhook failure behaviour and Pod Security labels - use Audit reports to forecast enforcement, and sequence fail-closed changes safely.
- Enumerate host-access workloads from pod specifications, reason about node-boundary exposure as a defender, remediate workloads that merely had access, remove standing debug tools, and record owned exceptions for those that need the node.
- Reduce cluster-admin and wildcard roles on audit-log evidence of use, replace a cluster-wide pipeline identity with namespace-scoped short-lived credentials, and make not mounting service account tokens the default.
Sign in to enrol — you can pay by bKash or Nagad, or apply a promo code.