← Back to catalogue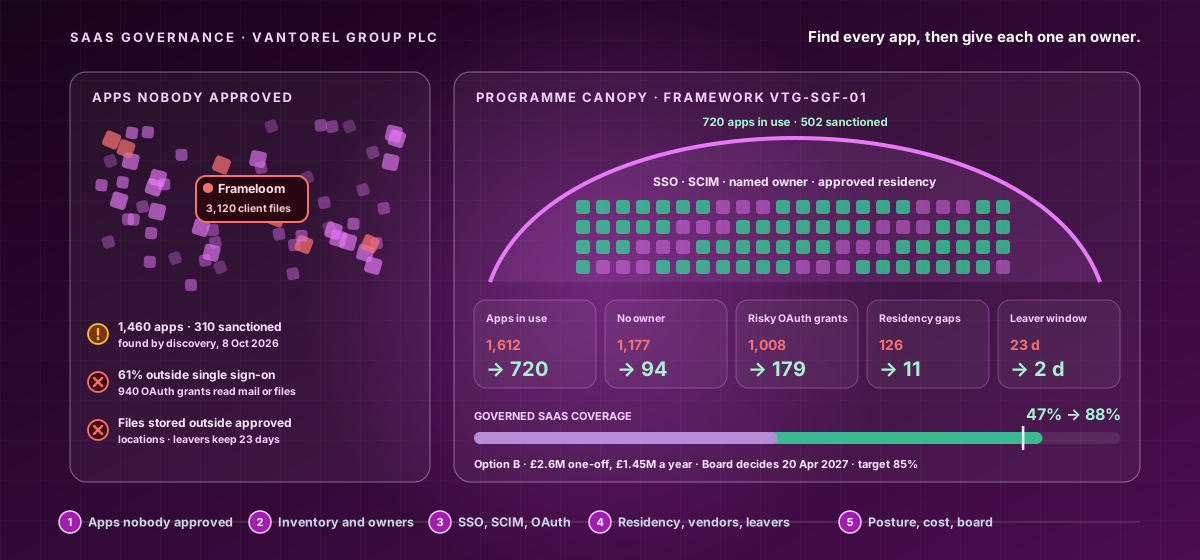
CY-PRO-069Pro Level · SaaS Security
SaaS Discovery and Governance at Scale
Find, govern and secure every SaaS app your people signed up for — in every region.
40 hours12 chapters60 lessons433 activities12 labs
What you'll learn
- Measure SaaS governance honestly — discovery from several sources, seat-weighted coverage, grants, residency and leaver windows — and contain a live client exposure without stopping the business.
- Build the governance foundation — ownership, data classification, tiering, SSO and SCIM, OAuth consent control, residency and transfer, and proportionate vendor assessment — across eight regions.
- Run SaaS governance as a service — offboarding for employees, freelancers and movers, licence reclamation and consolidation, posture monitoring, audit logs, KRIs and continuous discovery.
- Price the operating model at the margin, set appetite and accept residuals explicitly, align what clients and regulators are told, and win a resolution the Board can be held to.
Price:৳15,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.