← Back to catalogue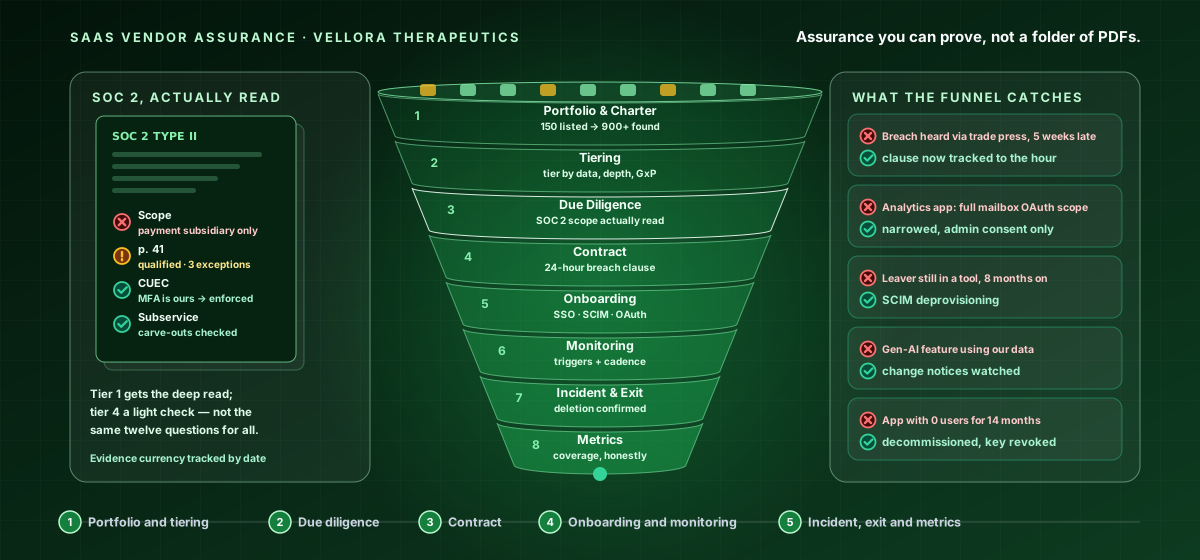
CY-SENIOR-109Senior Level · SaaS Vendor Assurance
SaaS Vendor Assurance Program — The Assurance Funnel
A senior-level GRC program course that builds and runs the assurance program covering your own SaaS vendors - discover the full portfolio, tier by inherent risk, actually read due-diligence evidence, negotiate enforceable security schedules, assure onboarding and integration, monitor continuously, handle vendor incidents and exit, and report honest program metrics. Four hands-on activities in every lesson.
15 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Discover the full SaaS portfolio and charter the assurance program with a cross-functional RACI.
- Tier every application by inherent risk and let tier drive proportionate assessment depth.
- Read and validate SOC 2, ISO 27001, and CAIQ evidence, and negotiate an enforceable security schedule.
- Assure onboarding, integration, and continuous monitoring, and handle vendor incident, exit, and program reporting.
Price:৳10,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.