← Back to catalogue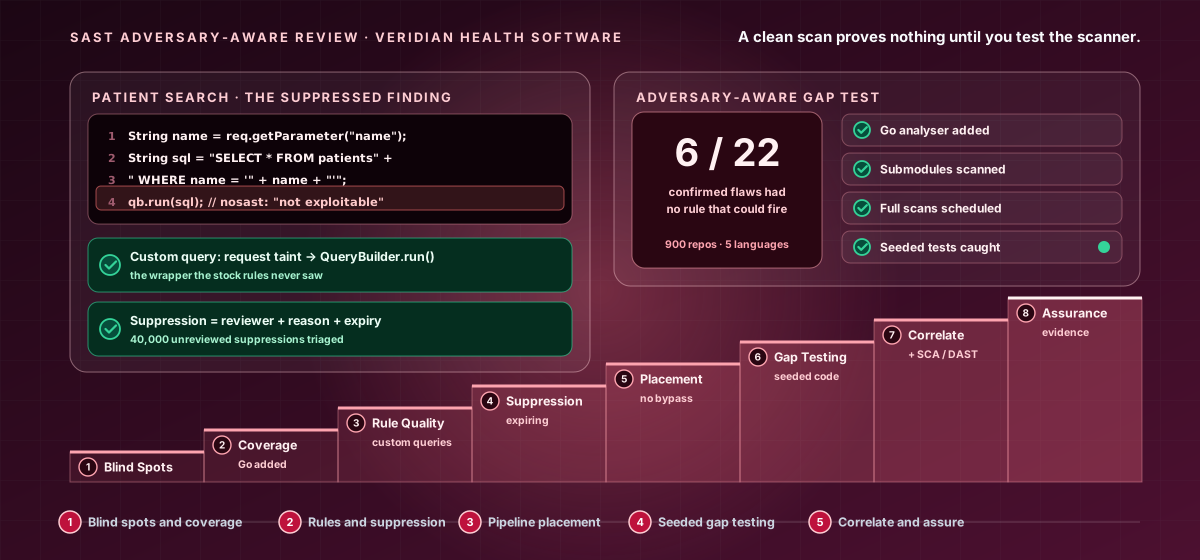
CY-EXPERT-022Expert Level · DevSecOps
SAST Adversary-Aware Review — The Analysis Staircase
An expert-level course that reviews an organisation's own static-analysis control the way someone trying to slip a vulnerability past it would look for gaps. Climb the analysis staircase across eight steps — visibility limits, coverage fidelity, rule quality, suppression governance, pipeline placement, adversary-aware gap testing with seeded code, correlation with SCA/DAST/runtime, and metrics/assurance — using real, defensive commands against your own scanner, rules, suppressions, branch protection, and evidence, strictly against your own authorised repositories.
18 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Map a SAST engine's real taint-analysis, interprocedural, and framework-modelling limits, and catalogue its structural false negatives.
- Audit and close real coverage gaps across languages, frameworks, monorepos, submodules, vendored code, and build-time transformations.
- Engineer, unit-test, and version custom queries that model an organisation's own sinks and sanitisers, closing proven rule gaps.
- Correlate SAST findings with SCA, DAST, and runtime evidence to confirm reachability and exploitability, and prove the control with metrics mapped to SSDF, PCI DSS 6.2/6.3, and NIS2.
Price:৳12,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.