← Back to catalogue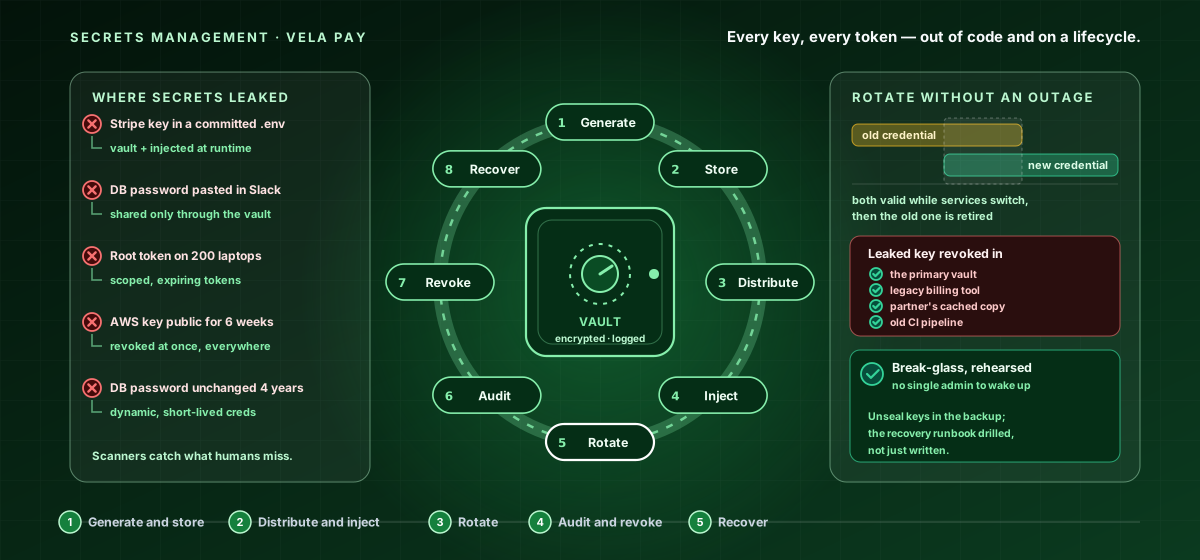
CY-MID-025Mid Level · Secrets Management
Secrets Management — The Secret Lifecycle
A hands-on mid-level course that keeps API keys, credentials, and tokens out of code and safely managed. Work the secret lifecycle - eight stations: Generate, Store, Distribute, Inject, Rotate, Audit, Revoke, and Recover - using a vault, dynamic short-lived secrets, runtime injection, rotation, and secret scanning to close the leaks. Grounded in vault/KMS practice; strictly defensive. Four hands-on activities in every lesson.
15 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Generate strong secrets and store them in a vault, never in code.
- Distribute and inject secrets at runtime without exposing them.
- Rotate, audit, and revoke secrets on a crypto-period and on demand.
- Scan for leaked secrets and recover safely with break-glass access.
Price:৳8,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.