← Back to catalogue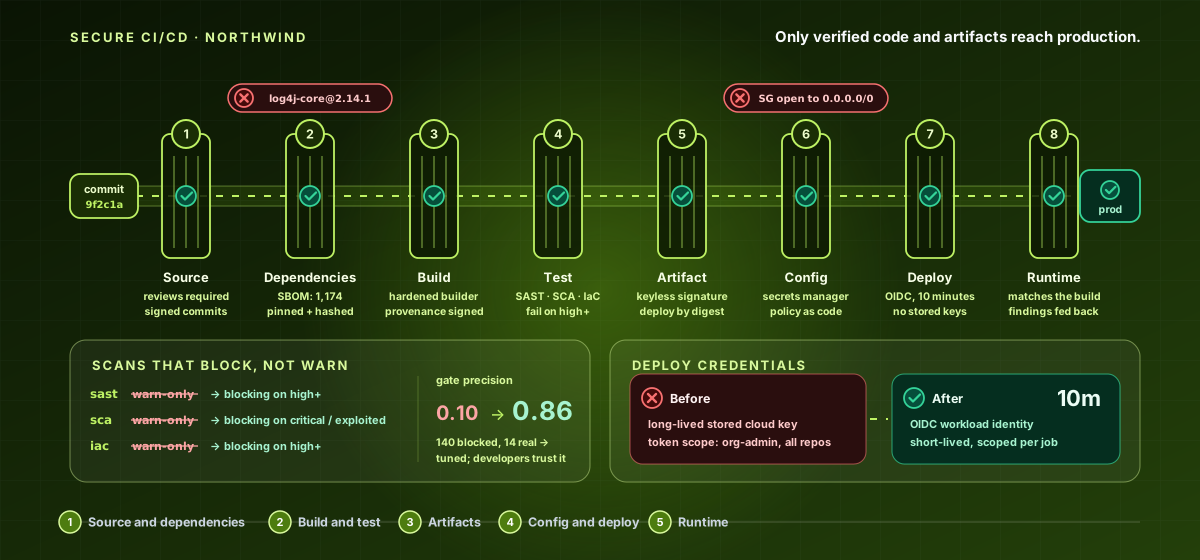
CY-MID-006Mid Level · Secure CI/CD Pipeline
Secure CI/CD Pipeline Security — The Pipeline Gates
A hands-on mid-level course that secures the software delivery pipeline so only trusted, verified code and artifacts reach production and the pipeline itself cannot be turned into an attack. Work the pipeline gates - eight gates code passes from commit to release: Source, Dependencies, Build, Test, Artifact, Config, Deploy, and Runtime - making security a gate that fails the build on real findings and verifying every artifact, with real branch protection, SCA/SBOM, SLSA provenance, SAST gates, artifact signing, and OIDC deploy credentials. Four hands-on activities in every lesson.
15 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Protect the source and verify dependencies with an SBOM and SCA.
- Protect and prove the build with isolation, reproducibility, and SLSA provenance.
- Make security tests gates that fail the build, and sign and verify artifacts.
- Deploy with short-lived credentials and gates, and verify runtime, feeding findings back.
Price:৳8,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.