← Back to catalogue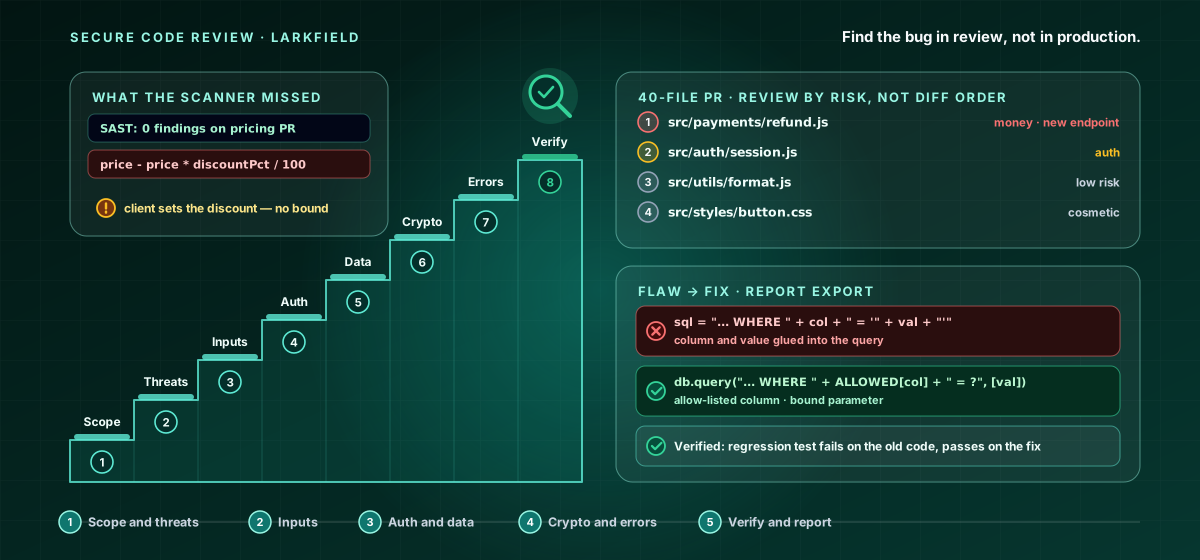
CY-MID-068Mid Level · Secure Code Review
Secure Code Review — The Review Staircase
A hands-on mid-level course that finds security bugs in code before they ship. Climb the review staircase - eight steps: Scope, Threats, Inputs, Auth, Data, Crypto, Errors, and Verify - reviewing real code for injection, broken access control, and secrets, and confirming each fix. Strictly defensive. Four hands-on activities in every lesson.
15 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Scope a review and reason from the code's threat model.
- Find input-handling, authentication, and access-control flaws in code.
- Spot data-exposure, crypto-misuse, and error-handling bugs.
- Confirm fixes and feed findings back to developers well.
Price:৳8,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.