← Back to catalogue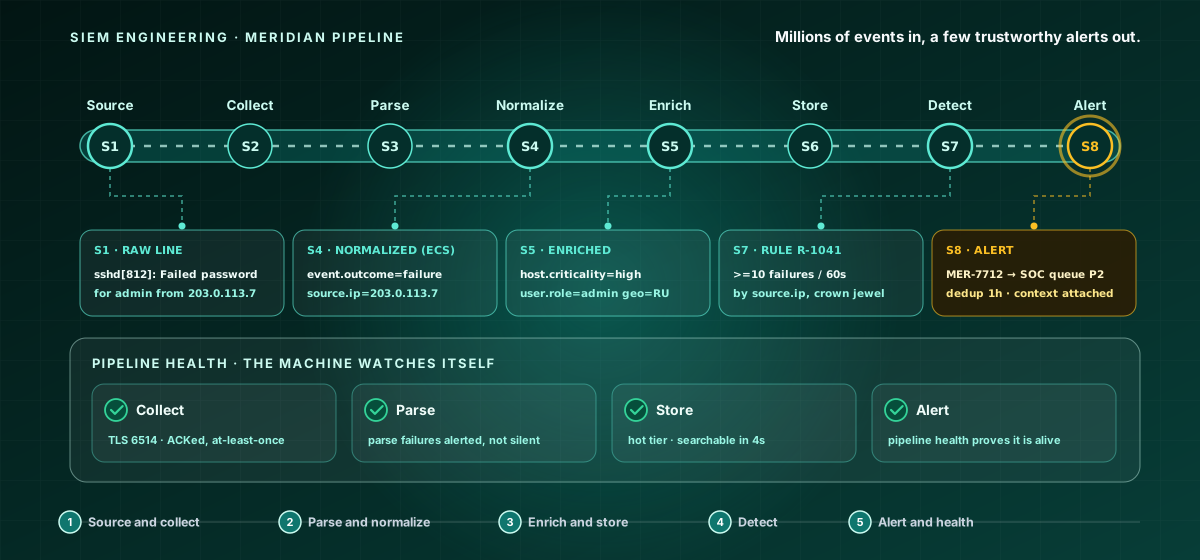
CY-EXPERT-003Expert Level · SIEM Engineering
SIEM Engineering — The Detection Pipeline
A deeply technical expert course that builds and assures the detection pipeline itself — the eight-stage machine that turns raw events into trustworthy alerts. Engineer sources, collection, parsing, normalization, enrichment, storage, detection, and alerting with real configs, real query syntax, and a tracer event proven at every stage. Four hands-on activities in every lesson.
18 hours8 chapters40 lessons265 activities8 labs
What you'll learn
- Model the SIEM as eight measurable stages, each silent in failure, proven end to end with tracer events.
- Engineer sources, reliable TLS collection with sized queues, and tested, drift-proof parsers.
- Normalize into a common schema, enrich with fresh context joins, and run tiered storage with defensible retention.
- Author engineered detections — Sigma, measured thresholds, sequences — and ship triage-ready alerts with pipeline health telemetry.
Price:৳12,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.