← Back to catalogue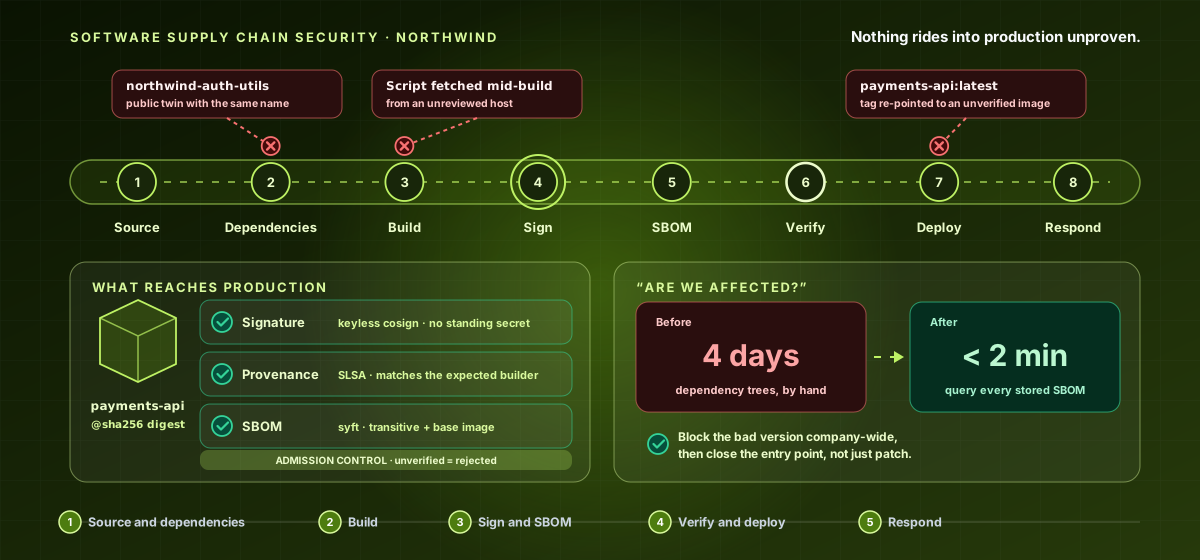
CY-MID-052Mid Level · Software Supply Chain Security
Software Supply Chain Security — The Supply Chain Pipeline
A hands-on mid-level course that secures everything your build trusts. Work the supply chain pipeline - eight stages: Source, Dependencies, Build, Sign, SBOM, Verify, Deploy, and Respond - defending against dependency, build, and artifact tampering with real SLSA, Sigstore, and SBOM work. Strictly defensive. Four hands-on activities in every lesson.
15 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Secure source and pin, vet, and monitor dependencies.
- Harden the build and sign artifacts with provenance (SLSA, Sigstore).
- Generate and consume SBOMs and verify before deploy.
- Respond to a compromised dependency or build quickly.
Price:৳8,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.