← Back to catalogue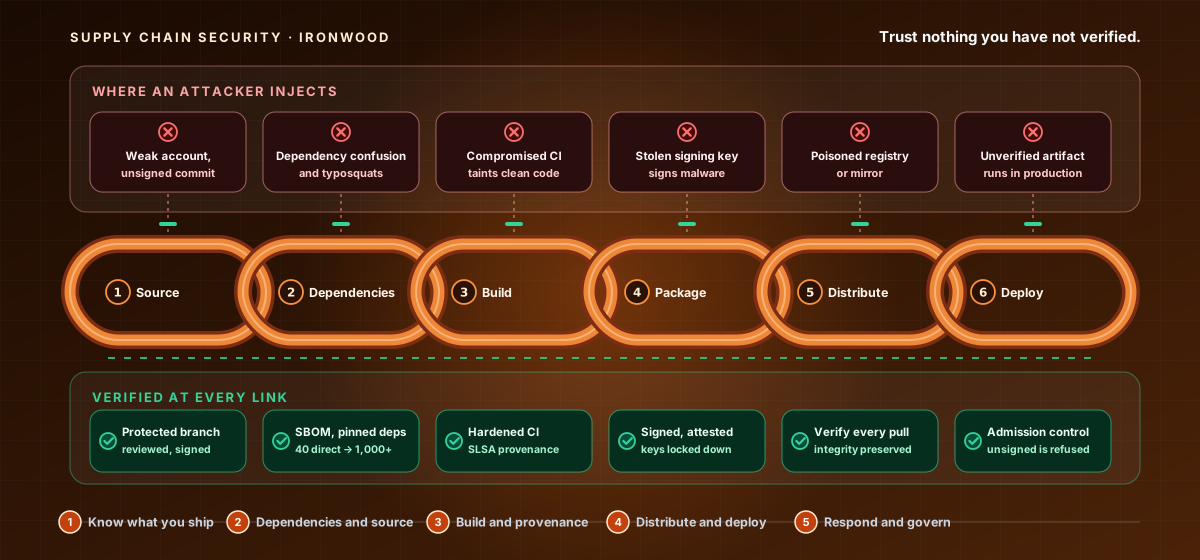
CY-EXPERT-046Expert Level · Supply Chain Security
Supply Chain Security — The Chain of Verified Trust
A twenty-hour, highly interactive expert-level course where you secure the software supply chain link by link — source, dependencies, build, artifacts, distribution, and deployment — knowing what is in your software and verifying integrity and provenance at every link. Trust is transitive; the chain is only as strong as its weakest link. Four hands-on activities in every lesson.
20 hours9 chapters45 lessons295 activities9 labs
What you'll learn
- Build an SBOM and inventory, and account for the transitive dependency tree.
- Secure dependencies, the source, and the build against supply-chain threats.
- Establish and verify provenance through signing, attestations, and admission control.
- Respond to supply-chain incidents and run an ongoing, risk-based program.
Price:৳12,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.