← Back to catalogue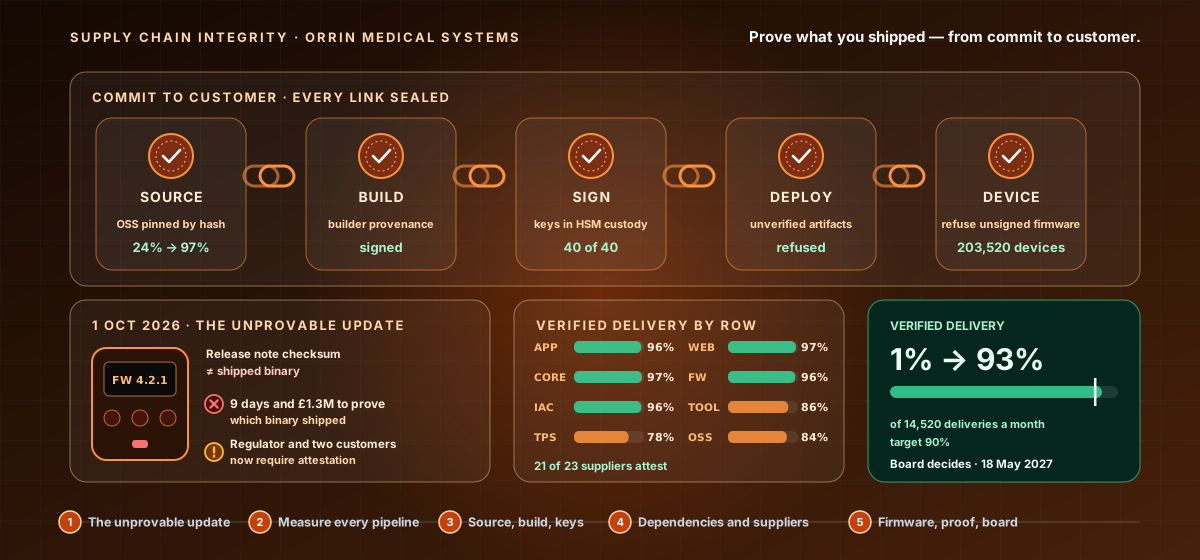
CY-PRO-067Pro Level · Supply Chain Security
Software and Hardware Supply Chain Integrity
Prove nothing in your software and hardware supply chain was tampered with.
40 hours12 chapters60 lessons433 activities12 labs
What you'll learn
- Measure software and firmware integrity honestly — provenance, deploy verification, key custody and SBOM accuracy by delivery — and contain a known exposure without stopping the business.
- Harden every link from commit to customer — source, build, signing, verification, dependencies and suppliers — and extend proof of origin to devices in the field, including those that cannot verify for themselves.
- Sustain integrity through indicators, drift detection, customer assurance and independent re-performance, and run the controls as a funded operating model.
- Price the transformation at the margin, set measurable risk appetite, route residuals to the authority that can accept them, and win a resolution the Board can be held to.
Price:৳15,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.