← Back to catalogue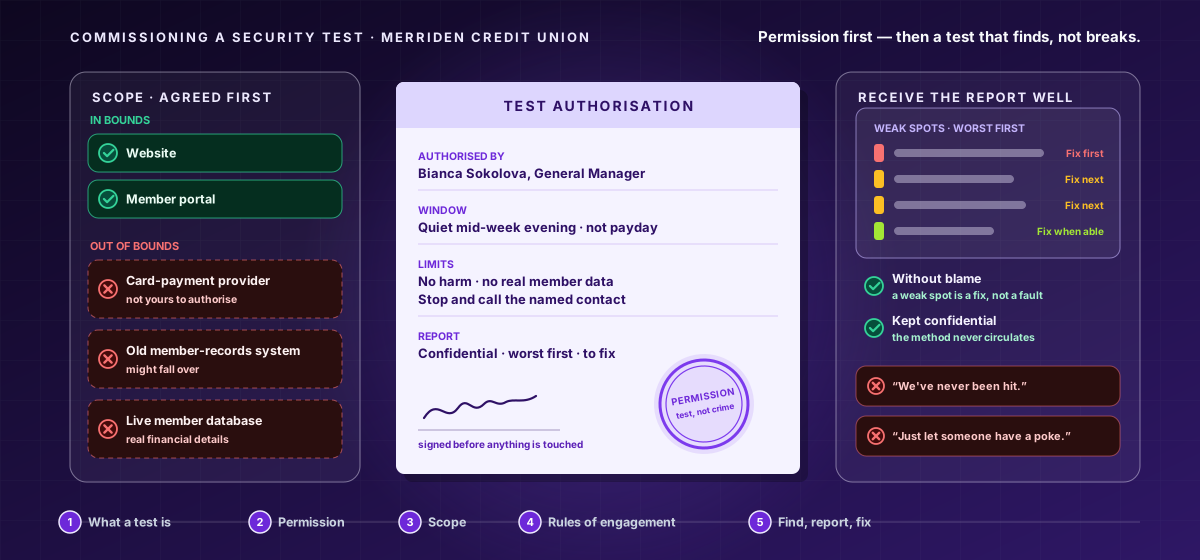
CY-BEGINNER-106Beginner · Ethical Hacking
The Agreed Test — Commissioning a Safe Security Check
A decision-maker's plain guide to safely commissioning and receiving an authorised security test: what such a test is, why written permission is everything, how to agree the scope and rules of engagement, the ethic of finding-not-breaking, and how to receive the report well. The commissioner's side only — never how to perform a test.
11 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- Explain what an agreed test is, and that permission is the only thing separating it from an attack — insisted on in writing, from the real owner.
- Agree the scope (what's in and out of bounds) and the rules of engagement (when, how far, no harm, no real data, and who to call).
- Expect the finding-not-breaking ethic, receive the report without blame, fix by priority, keep it confidential, and never circulate the method.
- See through 'we've never been hit' and 'just have a poke'. (Defensive/commissioning awareness only — no attack technique.)
Price:৳5,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.