← Back to catalogue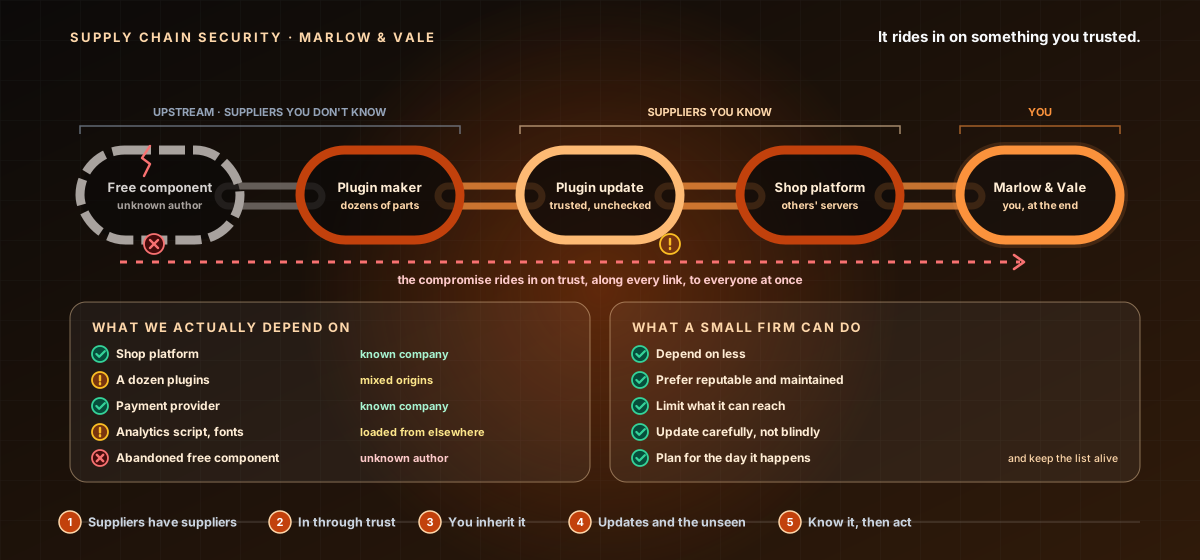
CY-BEGINNER-063Beginner · Supply Chain Security
The Chain — How a Supply-Chain Compromise Reaches You, and What a Small Firm Can Do
The attack does not come from a stranger. It rides in on a software update, a plugin, a component you installed because you trusted its source. Why your chain is longer than you think, why you inherit your suppliers' security, and what a small firm can actually do.
11 hours8 chapters32 lessons225 activities8 labs
What you'll learn
- See that your chain runs far past the vendors you chose, and that a compromise rides in on something you trusted.
- Understand that you inherit your suppliers' security, and why the update is the moment of trust.
- Accept you cannot verify the whole chain, know what you depend on, and find your weakest link.
- Do the five achievable things: depend on less, prefer maintained, update carefully, limit reach, and plan for compromise.
Price:৳5,000
Sign in to get accessSign in to enrol — you can pay by bKash or Nagad, or apply a promo code.